

Test post, please delete: Five Eyes and the AI shift (fixed)
One-sentence summary shown in listings and as the meta description.
Offensive Security Best Practices for Modern Enterprises
Annual assessments are not enough. Learn how threat emulation, Red Team exercises, and continuous security validation help enterpr
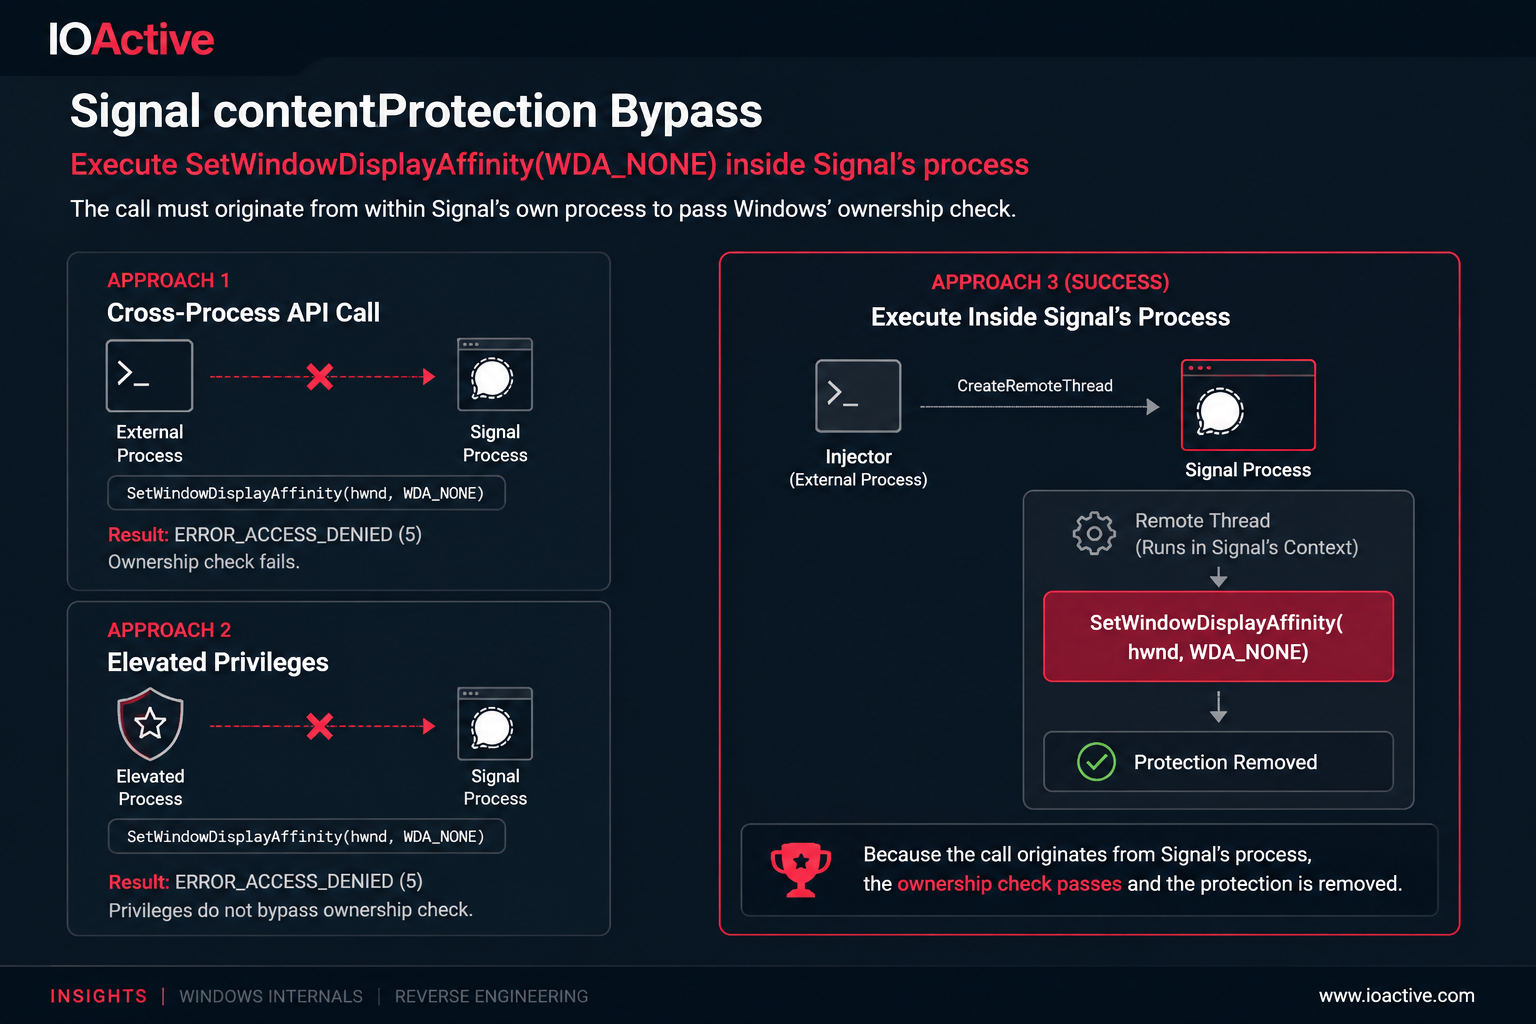
Signal Windows Desktop: contentProtection Bypass
Signal Desktop's Windows screen-capture protection can be bypassed via CreateRemoteThread code injection — even from an elevated p
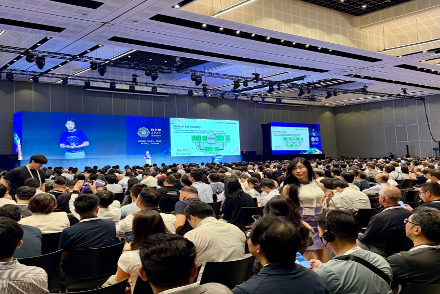
Key Takeaways from the 2026 OCP APAC Summit
IOActive attended the 2026 OCP APAC Summit in Taipei (Aug 11–12), covering AI infrastructure security, SONiC networking, and growi
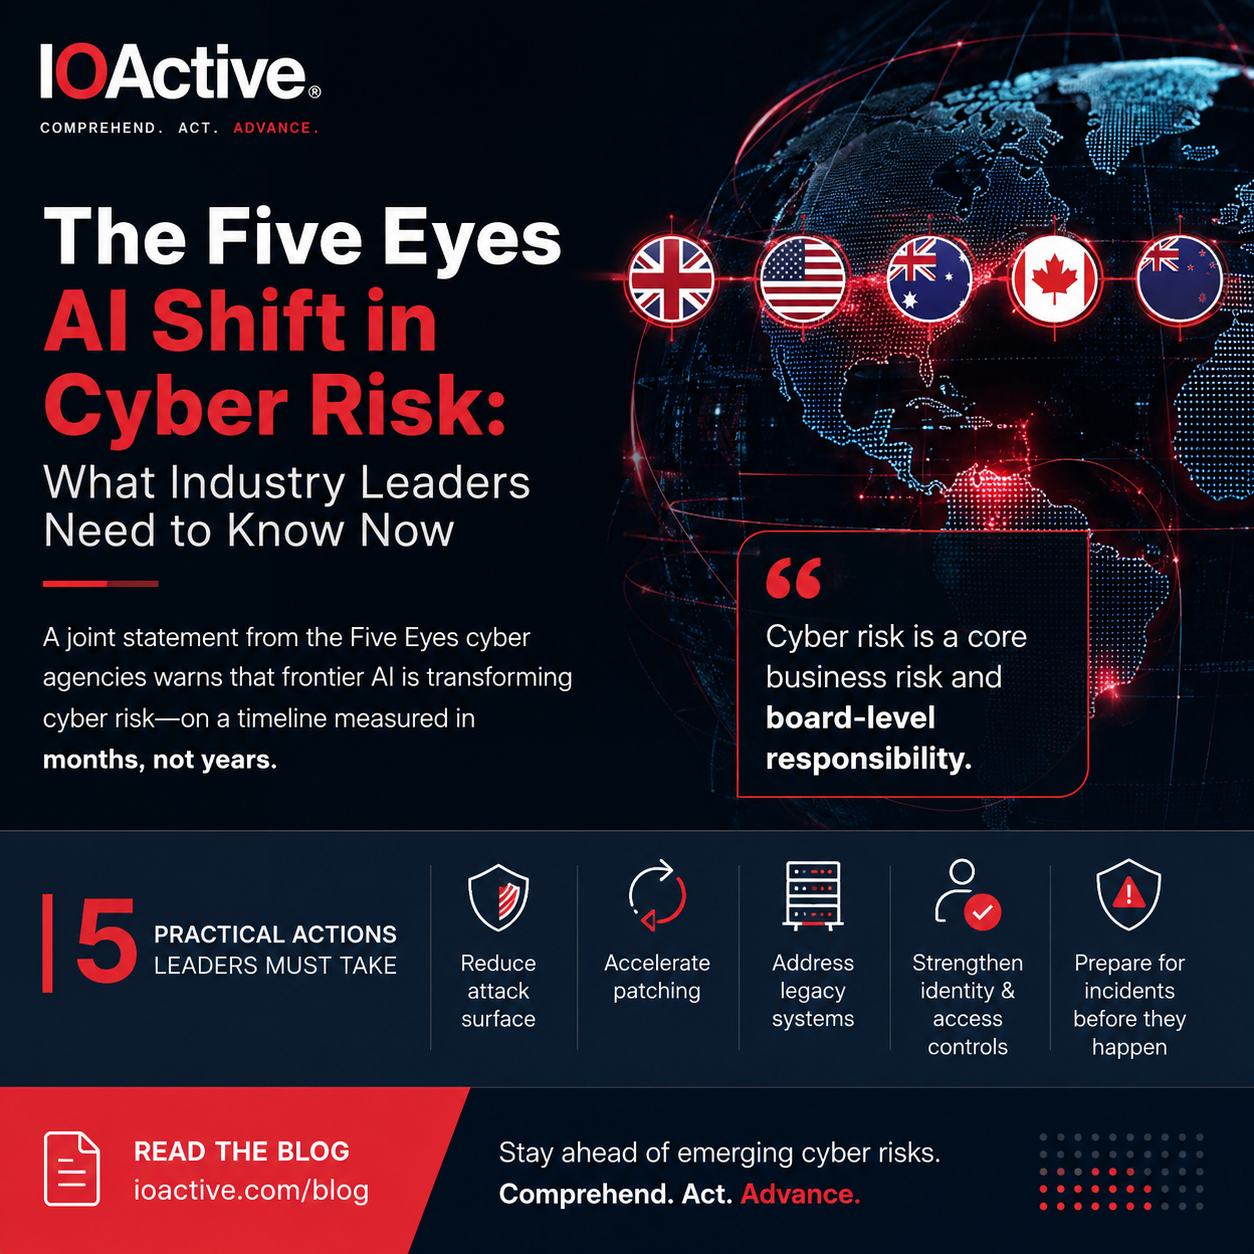
The Five Eyes AI Shift in Cyber Risk Statement: What Industry Leaders Need to Know Now
Five Eyes cyber agencies warn AI is cutting exploit timelines to months: 75% of UK CNI attacks are state-linked. Learn what boards
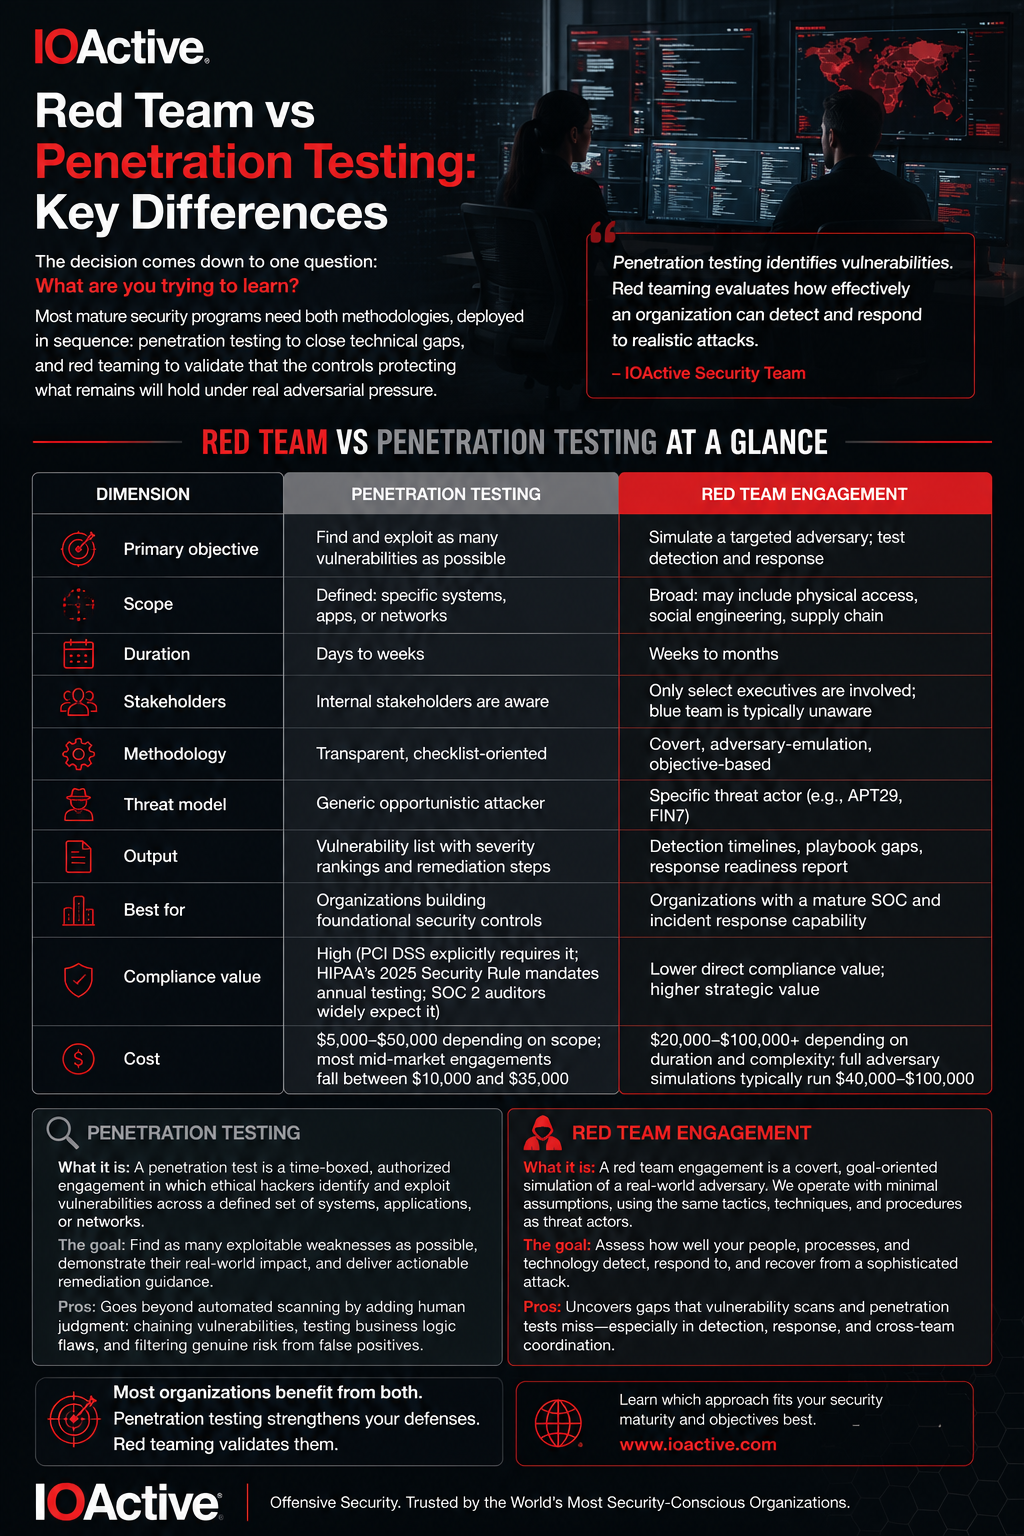
Red Team vs Penetration Testing: Key Differences
Penetration testing finds vulnerabilities. Red teaming tests whether your organization can prevent, detect, and respond to a real
When the Advisory Arrives First: Minnesota's Water Utilities and the Limits of Warning
What happened in the Minnesota water cyberattack? 30+ utilities lost automated OT controls in July 2026, days after CISA's AA26-09
Security Challenges in AI Adoption: 2026
AI adoption is moving fast. Security is not keeping up. Explore the top security challenges in AI adoption in 2026, with current s
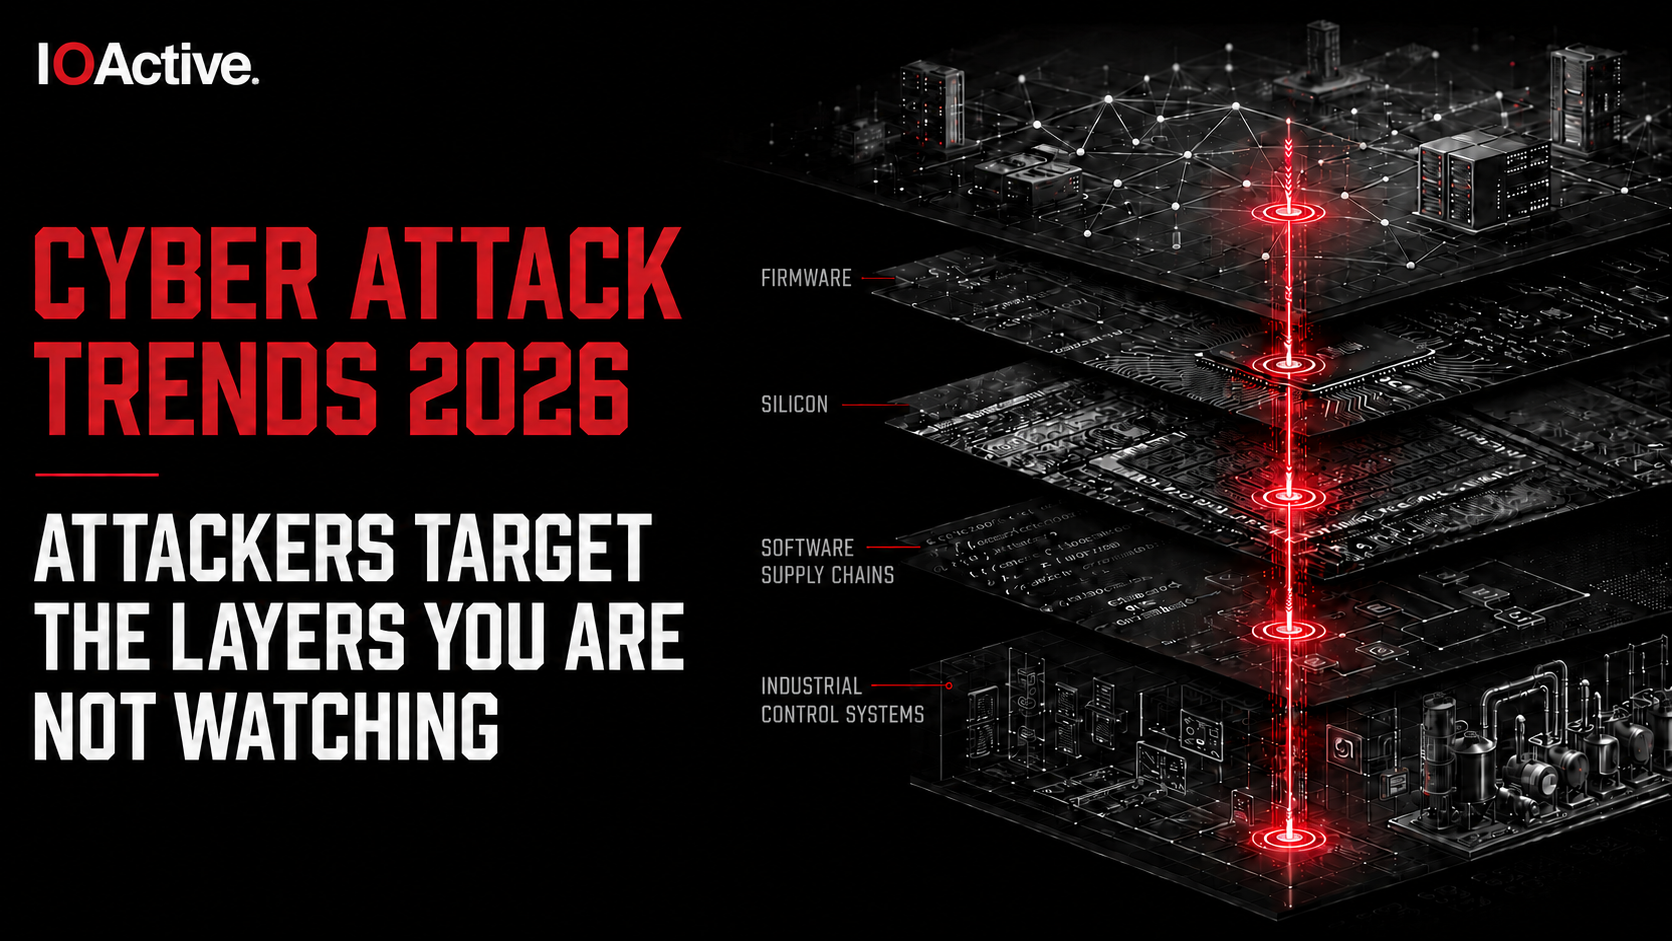
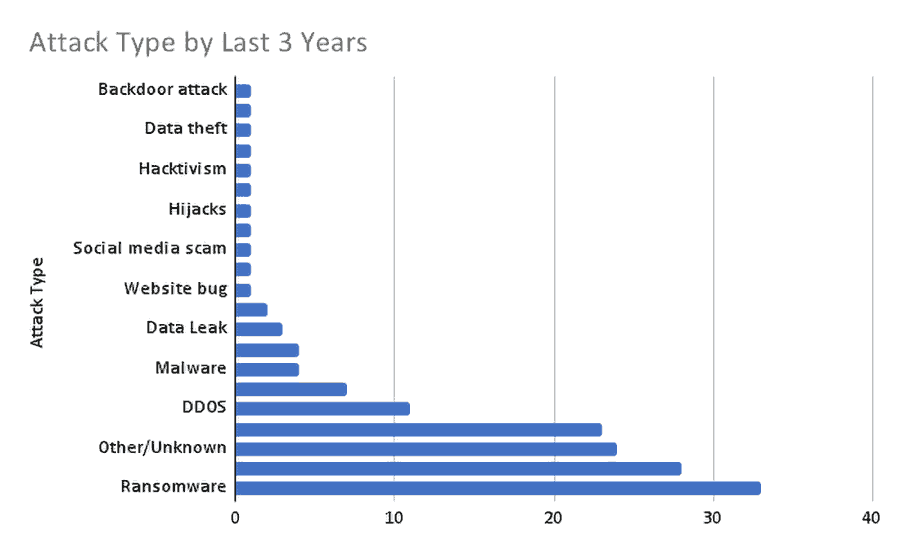
Cyber Attack Trends 2026: What Security Teams Face
Cyber attack trends 2026: Which threats are real business risks and what can you do about them? IOActive breaks down ransomware, O
Iranian-Affiliated Actors Expand PLC Targeting to Siemens and Schneider Electric: What CISA’s Updated Advisory Means for CNI
Learn how CISA's updated AA26-097A advisory expands Iranian PLC attacks to Siemens and Schneider Electric—and what critical infras
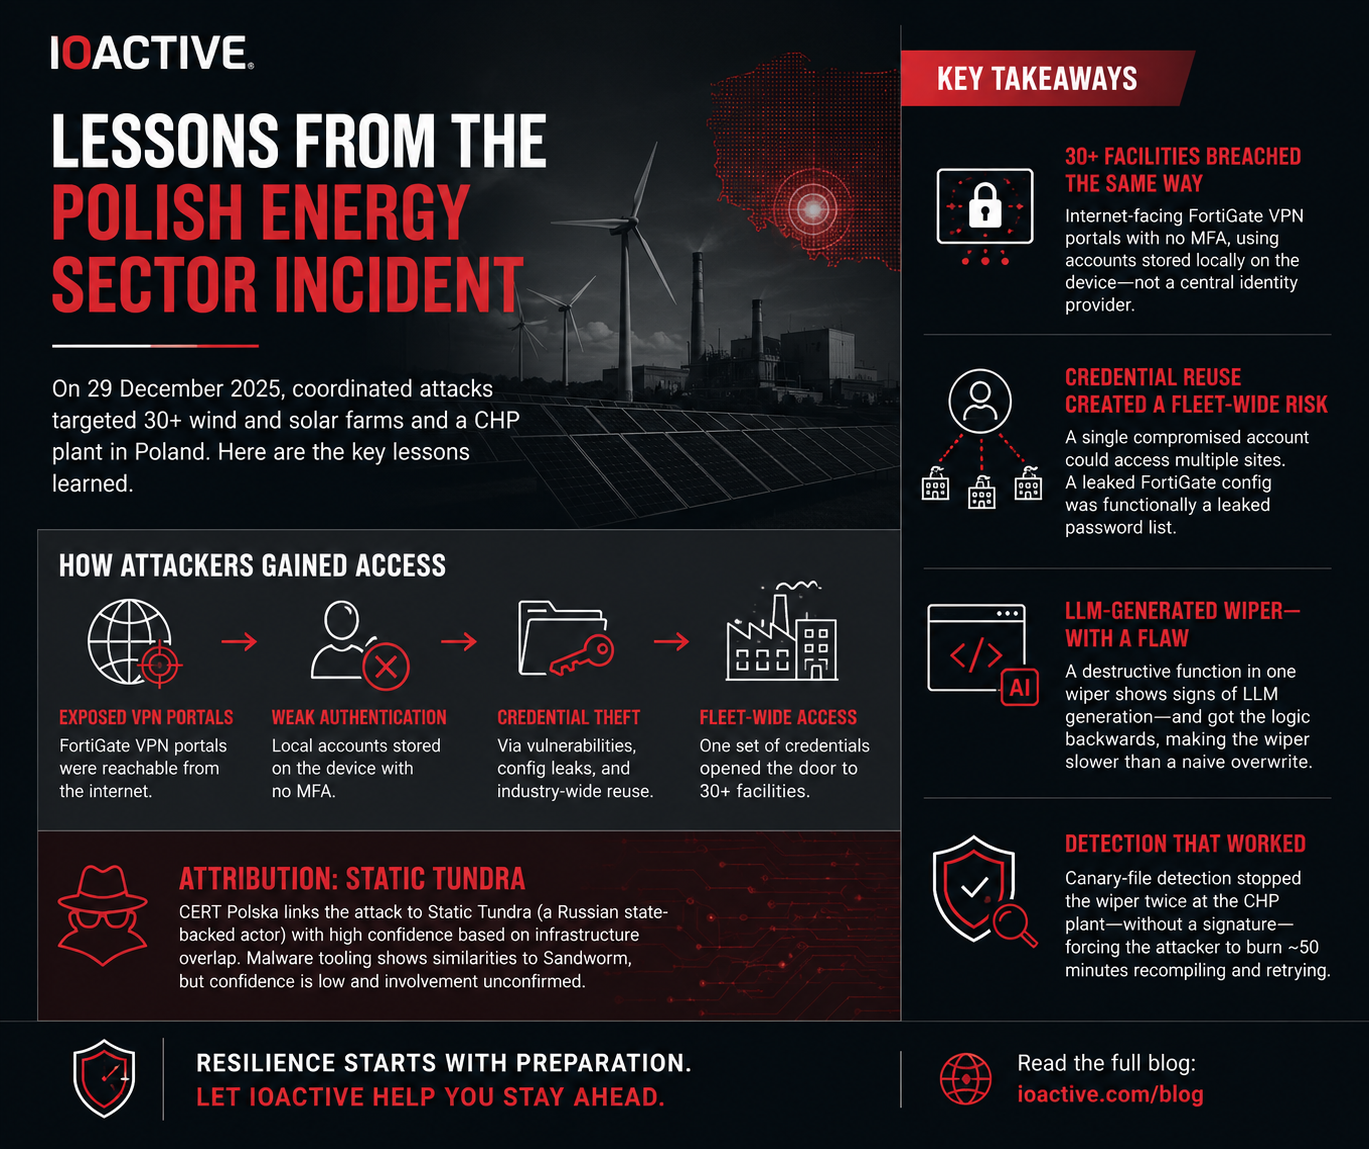
Lessons from the Polish Energy Sector Incident
How default FortiGate VPN credentials let one threat actor breach 30 Polish energy facilities in a single coordinated OT attack—an
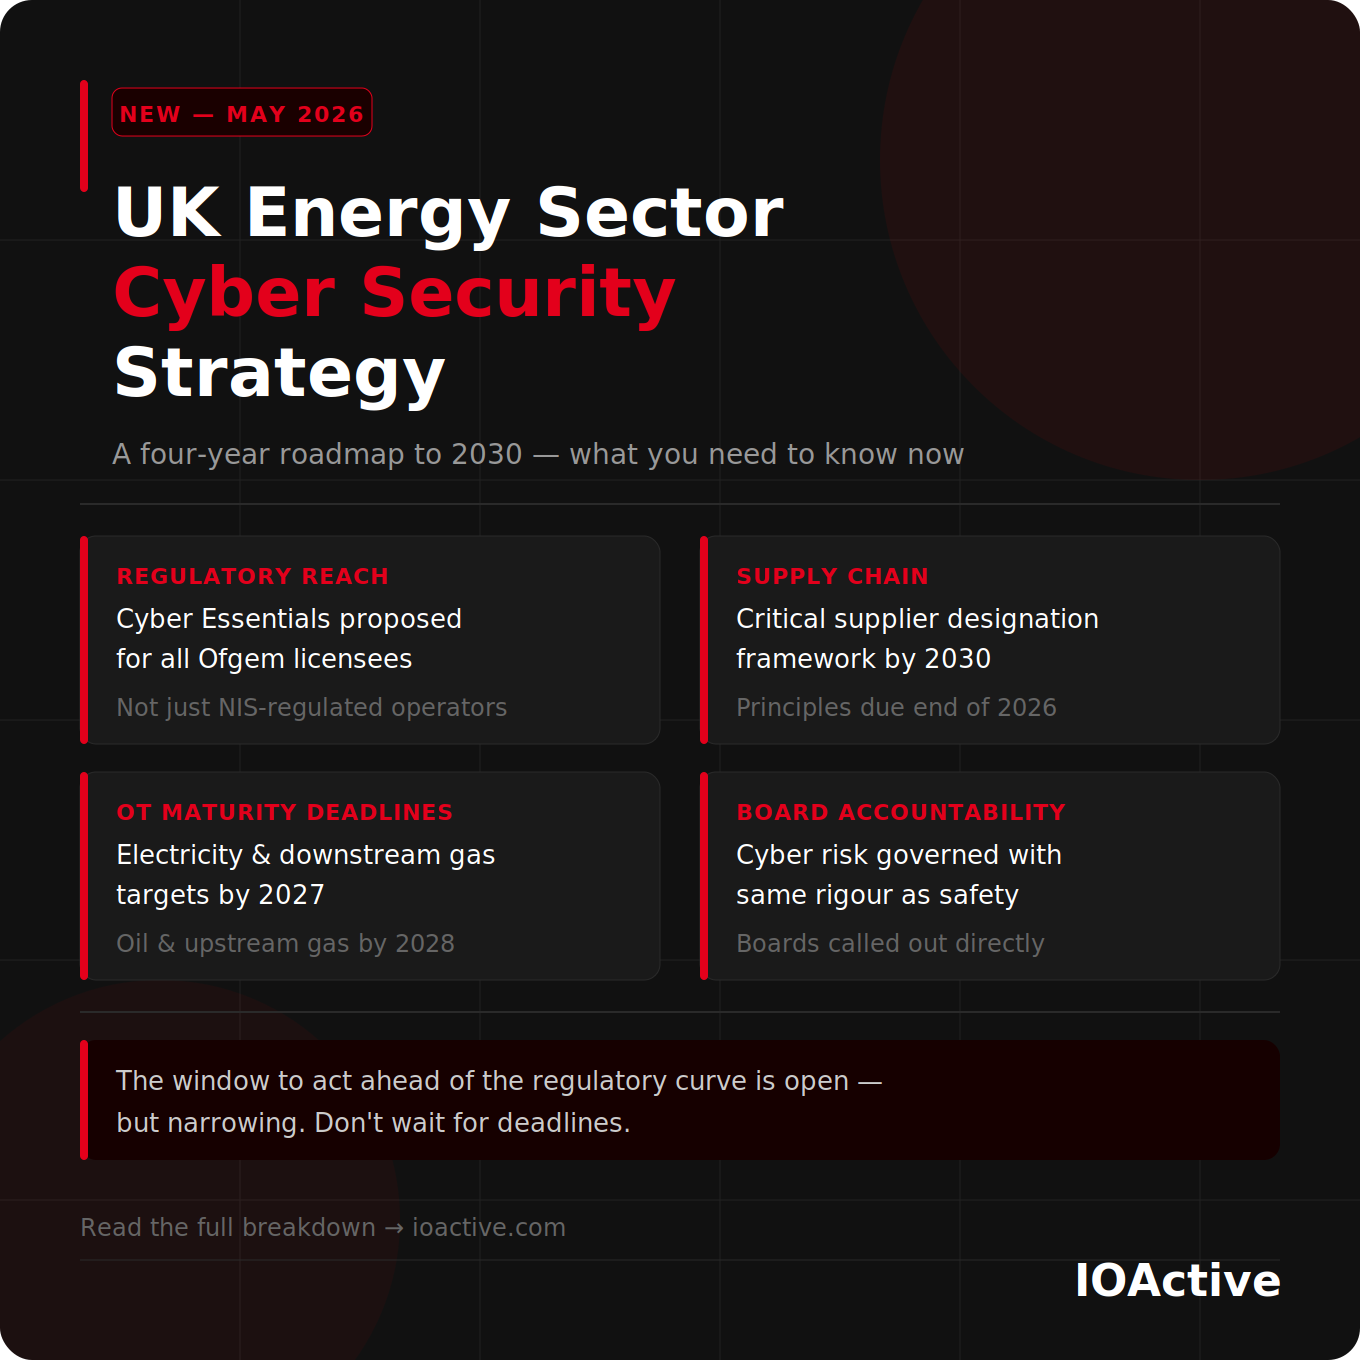
The UK Energy Sector Cyber Security Strategy: What Industry Leaders Need to Know Now
The UK Government published their Energy Sector Cyber Security Strategy on 28 May 2026, setting out a four-year roadmap to 2030. C
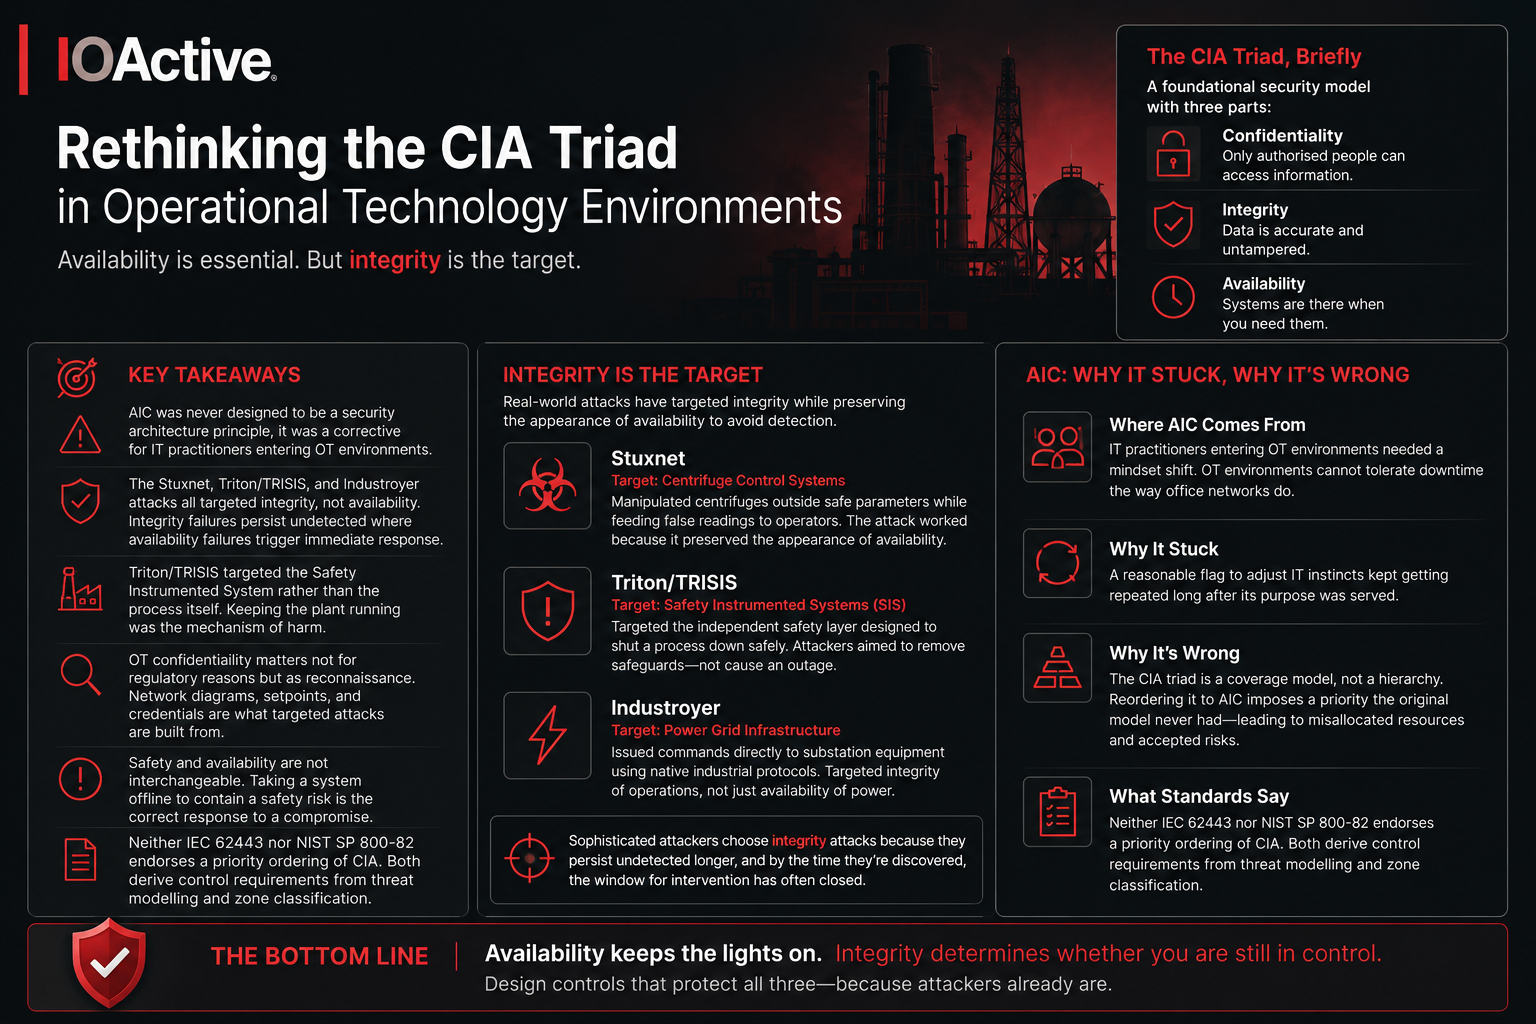
Rethinking the CIA Triad in Operational Technology Environments
Walk into most introductory OT security talks and you will hear the same piece of advice. Forget CIA, think AIC: Availability firs
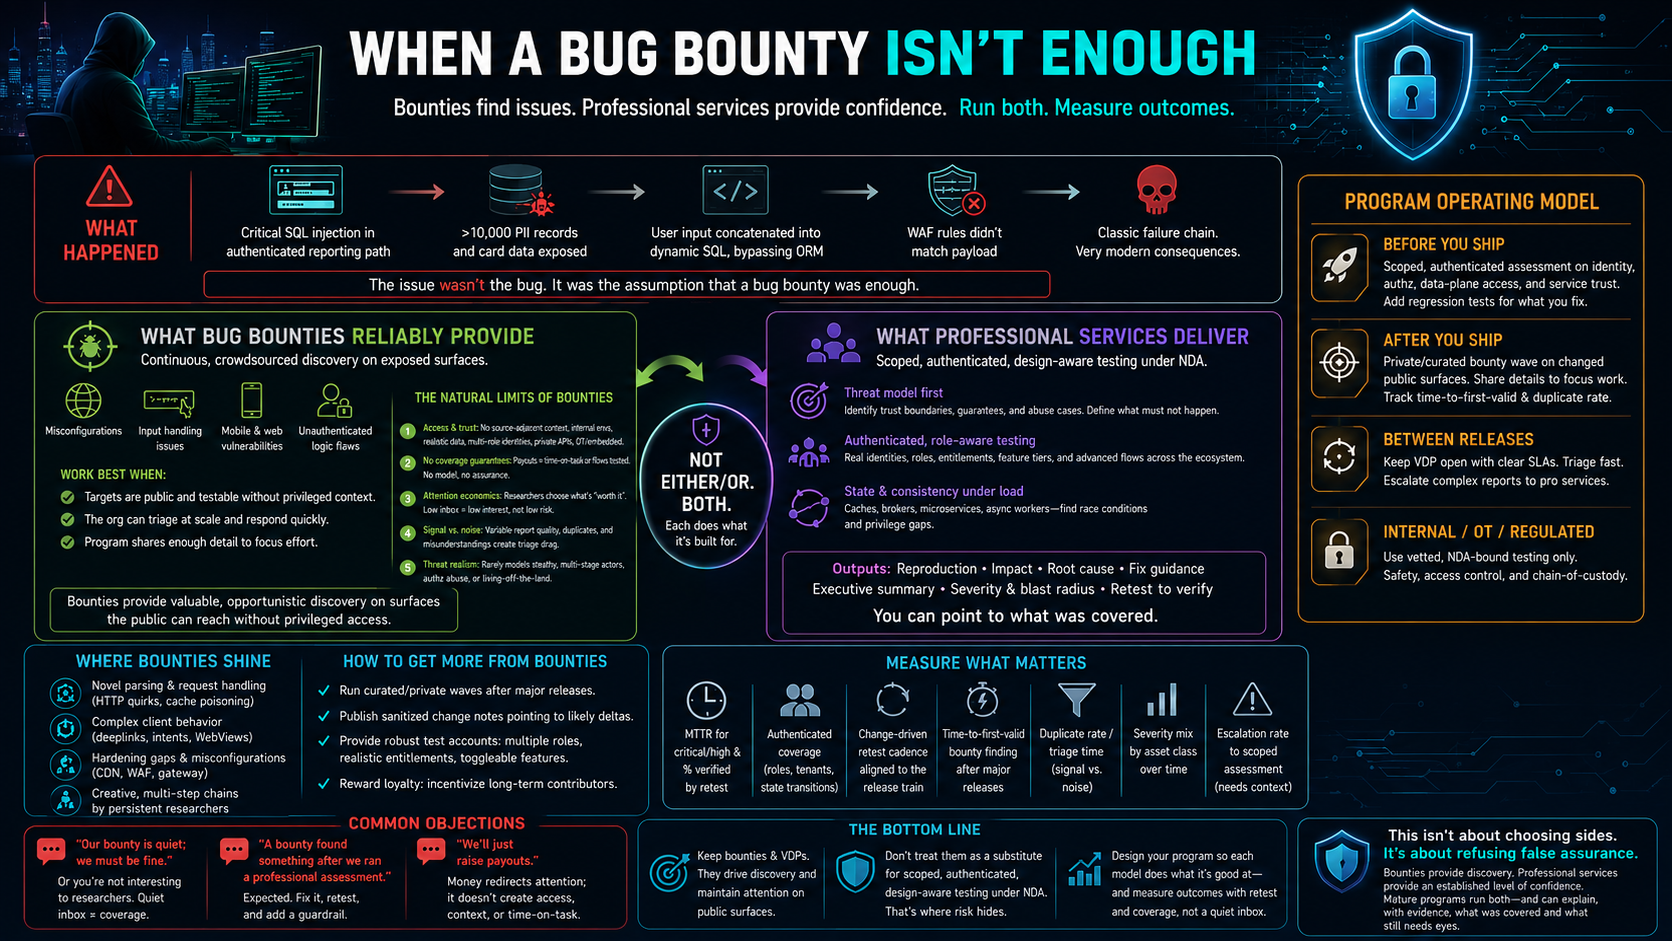
When a Bug Bounty Isn’t Enough
This post is about how bug bounties and professional services actually work, where each is strong, and why neither replaces the ot
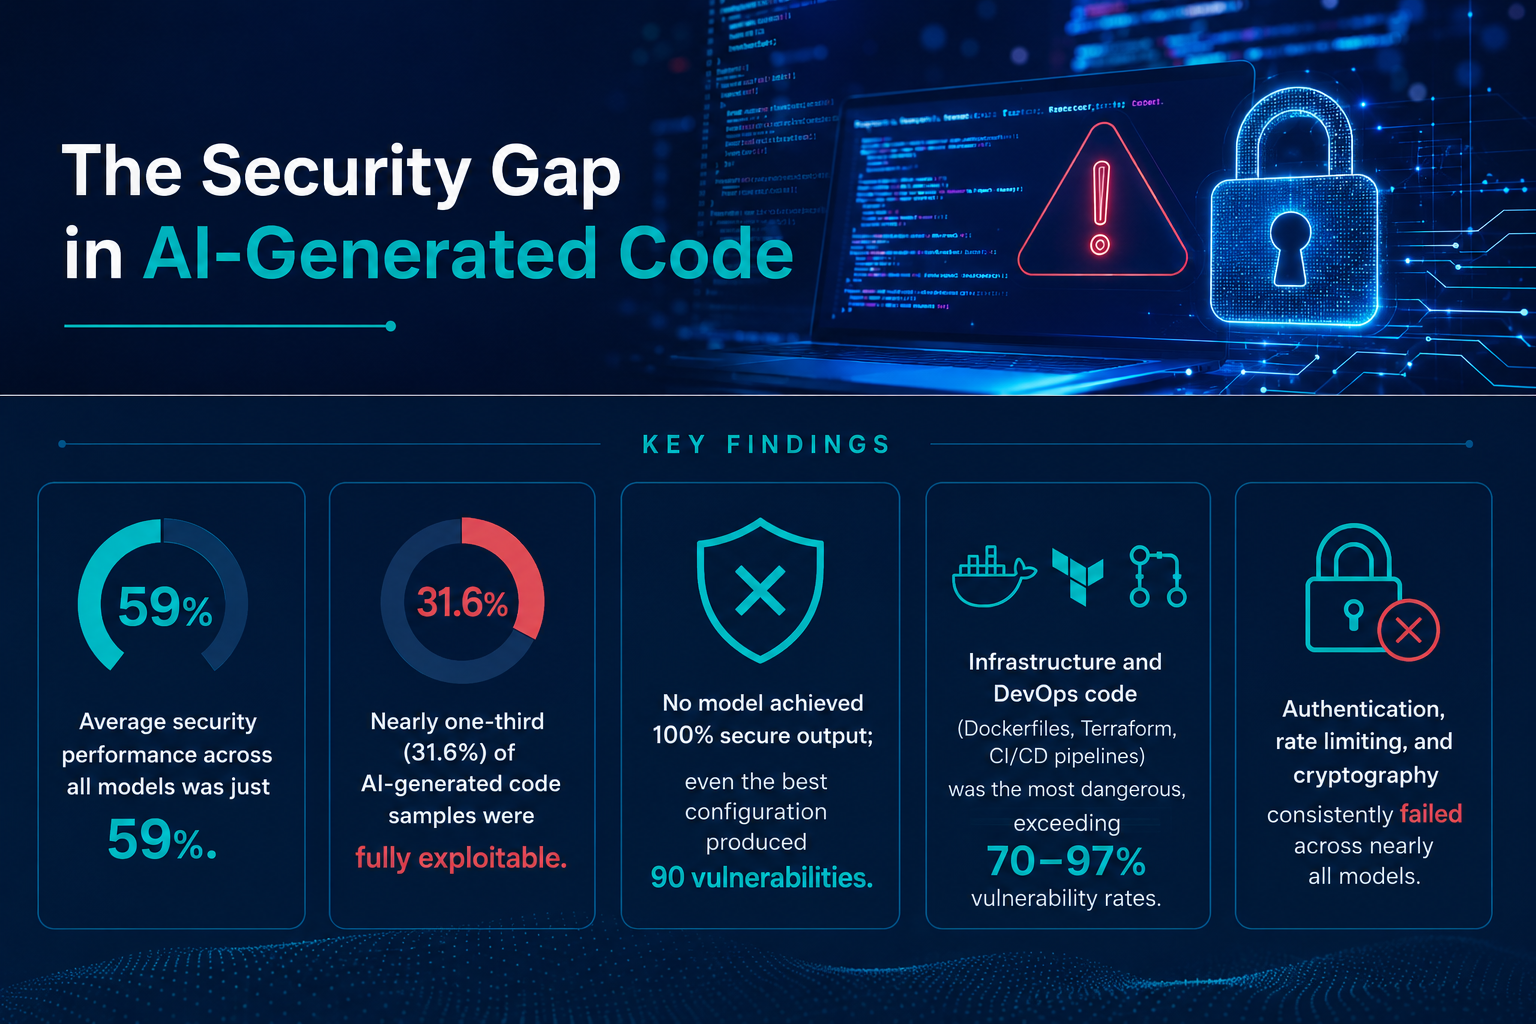
The Security Gap in AI-Generated Code
IOActive evaluated 27 leading AI models and AI-powered coding tools using 730 real-world programming prompts across 27 languages a
From Skynet to AI Agents: The State of Robot Security Nine Years Later
A new research paper IOActive contributed to, "Cybersecurity AI: Hacking Consumer Robots in the AI Era", published in March 2026 w
EU Cyber Resilience Act (EU CRA): What to Know and How IOActive Can Help
Cybersecurity regulation in the EU is shifting in a meaningful way. With the Cyber Resilience Act (CRA), the focus is moving upstr
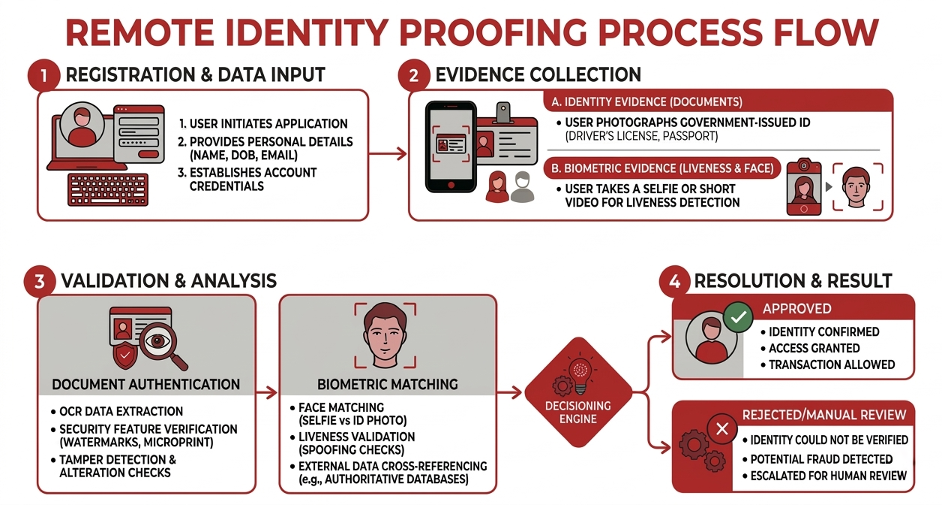
Virtual Assistant: Defeating Liveness Detection with the Help of Virtual Devices
In this article, we will explore how liveness detection, which is designed to distinguish real users from spoofed representations,
The Evolution of AI-Powered Security Consultants
Learn what's happening now with the capabilities of the large language models (LLMs) that fuel AI.
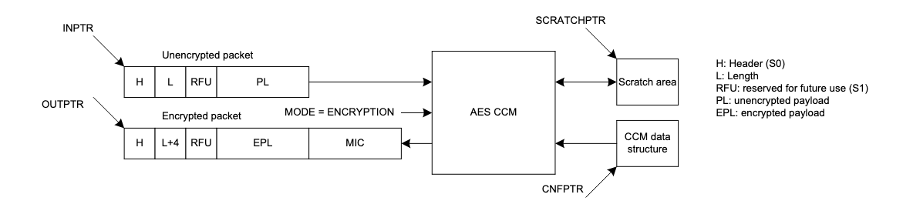
Reversing the RADIO – AES CCM Link in the nRF family
I’ve been working on a research project that includes radio frequency (RF) nodes with a proprietary protocol running on top of Nor
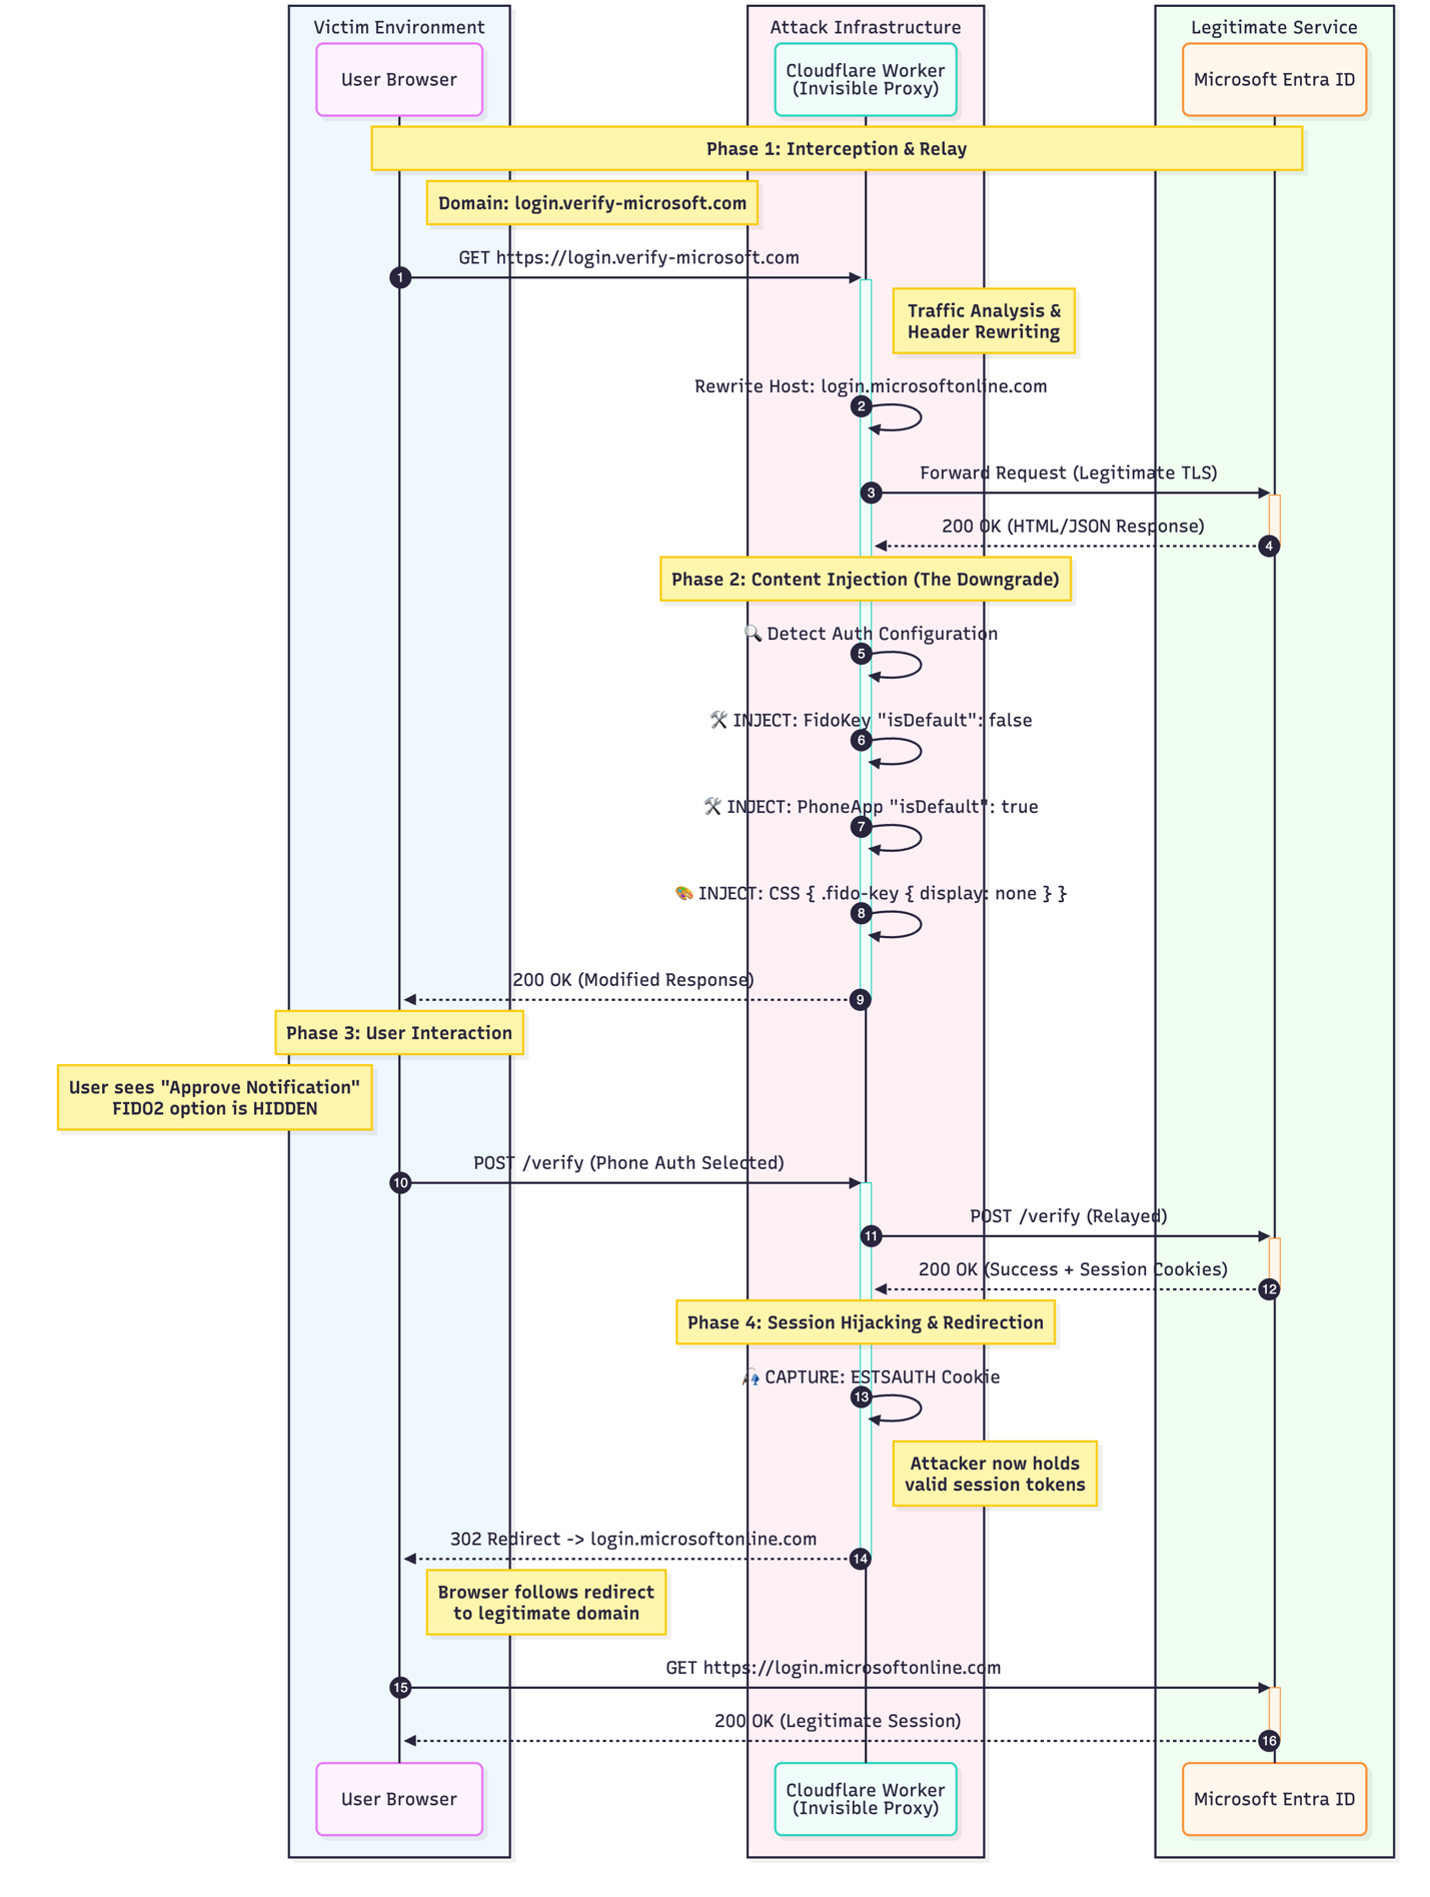
Authentication Downgrade Attacks: Deep Dive into MFA Bypass
This research introduces two key contributions: first, the weaponization of Cloudflare Workers as a serverless transparent proxy p
Code Review & Dynamic Fuzzing of Microsoft’s Signing Transparency
IOActive performed a thorough security assessment of Microsoft’s Signing Transparency (ST) service, focusing on code review, dynam
Semiconductor Industry Jargon
The semiconductor industry uses a large and complex set of jargon. This set of terms represents the significant intersection of sc
Deepfake Defense: From No-Cost Basics to Enterprise-Grade Controls
Deepfakes are a forcing function for better workflow. Start by removing voice-only approvals and requiring directory callbacks and
Windows 11 Upgrade - The Hardware Security Focused Refresh
Windows 10’s End of Life is slated for October 14th, 2025. After this date, it will no longer be supported, and businesses are exp
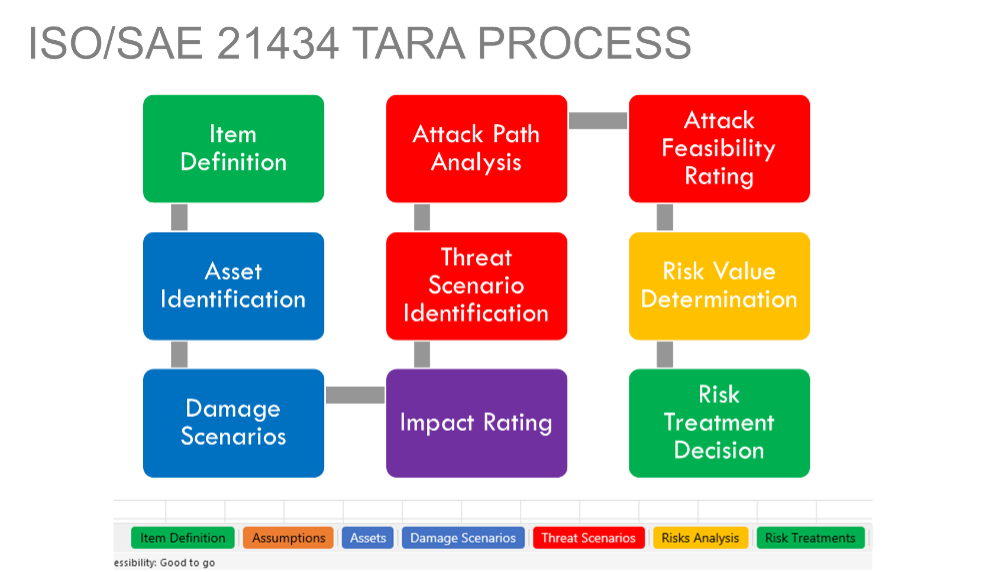
Smarter Security, Leaner Budgets: IOActive & SERJON’s Approach to Cyber Optimization
In our experience working with companies of all sizes and types, one challenge keeps coming up: cybersecurity operations are becom
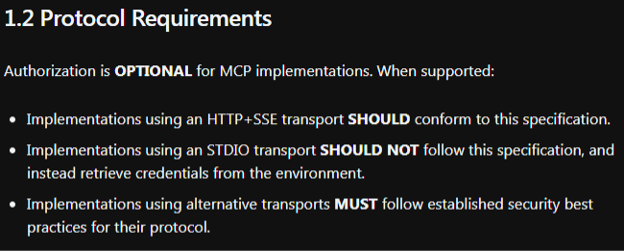
Better Safe Than Sorry: Model Context Protocol
In this blog post, we’ll delve into the world of the Model Context Protocol (MCP), an open standard designed to facilitate seamles
IOActive Autonomous and Transportation Experience and Capabilities
For the past 5 years, IOActive has been focused on understanding Autonomous and Remote-Controlled/Access technologies and their in
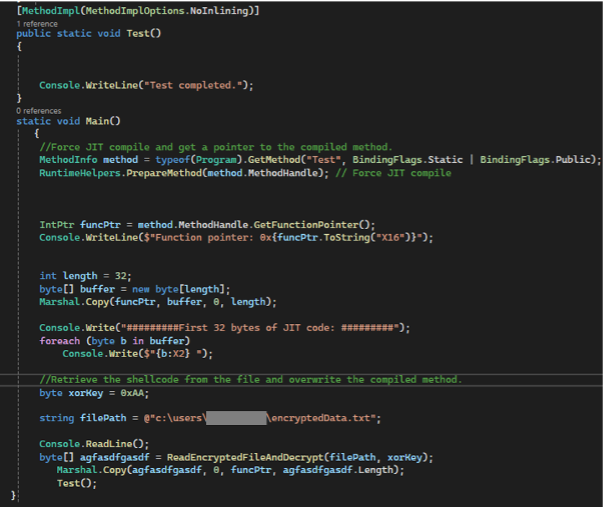
Breaking Patterns: Rethinking Assumptions in Code Execution and Injection
Explore the value of Endpoint Detection and Response in identifying suspicious activity patterns and securing your network.
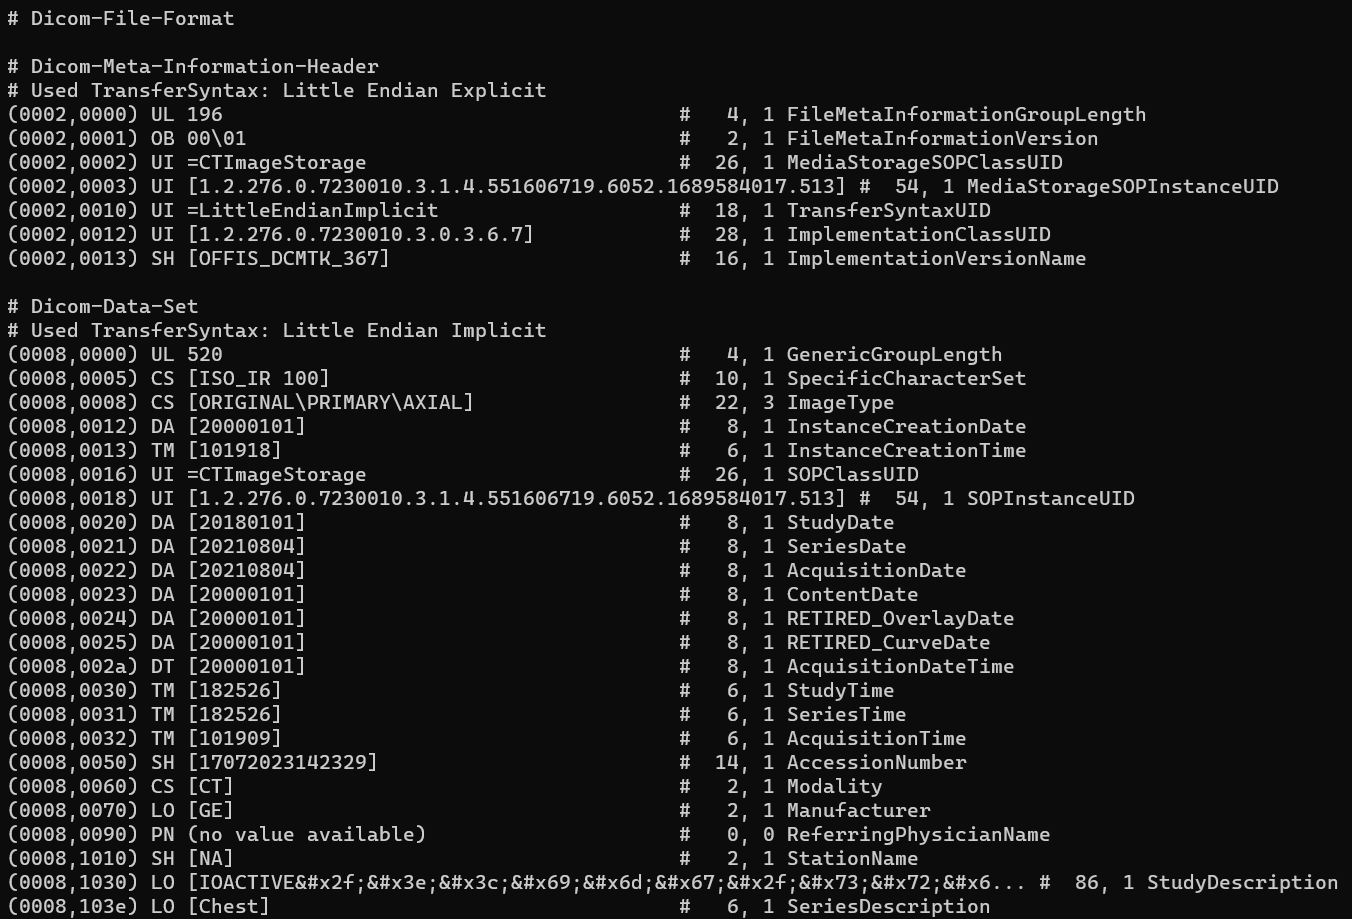
Penetration Testing of the DICOM Protocol: Real-World Attacks
When improperly configured, DICOM communications may expose Protected Health Information (PHI) to interception or tampering. This
Red vs Purple Team, what’s the difference?
Learn the key differences between Red and Purple Teams. Explore their unique roles, strategies, and how they collaborate to streng
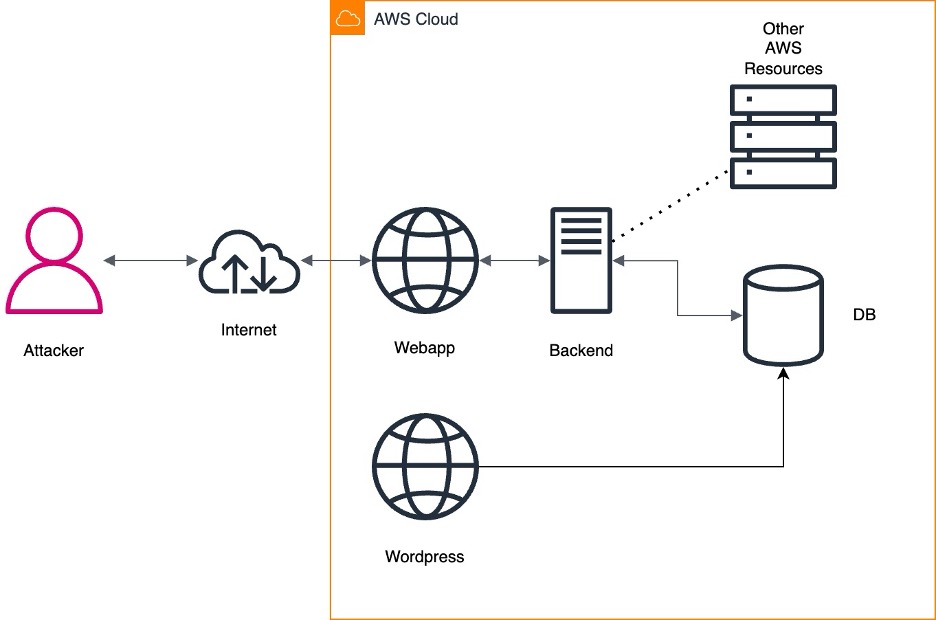
Pen Test Like a Red Teamer - Beyond the Checklist
Explore the importance of a Red Team Pen Test for uncovering security vulnerabilities through realistic threat simulations.
Understanding the Potential Risks of Prompt Injection in GenAI
Explore the impact of GenAI tools like ChatGPT on various industries, transforming the way we work, but adding some risk.
Preparing for Downstream Attacks on AI Systems
Understand the risks of downstream attacks on AI systems and learn how to secure your AI infrastructure against threats.
Threat Brief: Low-level Hardware Attacks
Explore low-level hardware attacks and how they threaten device security as attackers evolve their techniques to breach systems.
Novel Invasive Attack on One-Time-Programmable Antifuse Memory
Learn about the vulnerabilities in one-time-programmable antifuse memory and the novel invasive attack method revealed by IOActive
Understanding Logits And Their Possible Impacts On Large Language Model Output Safety
Discover the concept of logits and their significance in large language models. Unravel what logits mean in AI technology.
Red Teaming in 2025 & Why You Need One More Than Ever
Discover why a Red Team Service is crucial in 2025. Safeguard against evolving cyber threats and enhance your defenses.
Building Management Systems: Latent Cybersecurity Risk
Learn about the risks of building management systems cyber threats and how to enhance your security measures effectively.
Inside IOActive’s Innovative Key Fob Badge for DEF CON 2024’s Car Hacking Village - Part 3/3
Explore the creation of DEF CON 2024’s Car Hacking Village badge in this detailed 3-Part Series. Discover key fob technology.
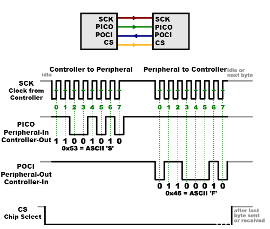
Inside IOActive’s Innovative Key Fob Badge for DEF CON 2024’s Car Hacking Village - Part 2/3
Explore the creation of a unique badge for DEF CON 2024’s Car Hacking Village. Learn about key fob innovations and technology.
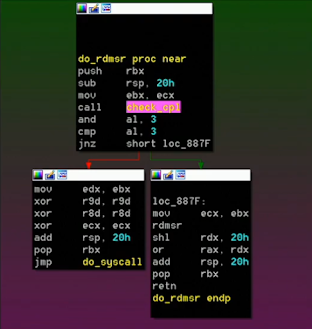
Tales from the Call-Gate: An SMM Supervisor Vulnerability
Explore the SMM Supervisor vulnerability and its impact on AMD system security revealed in recent research and presentations.
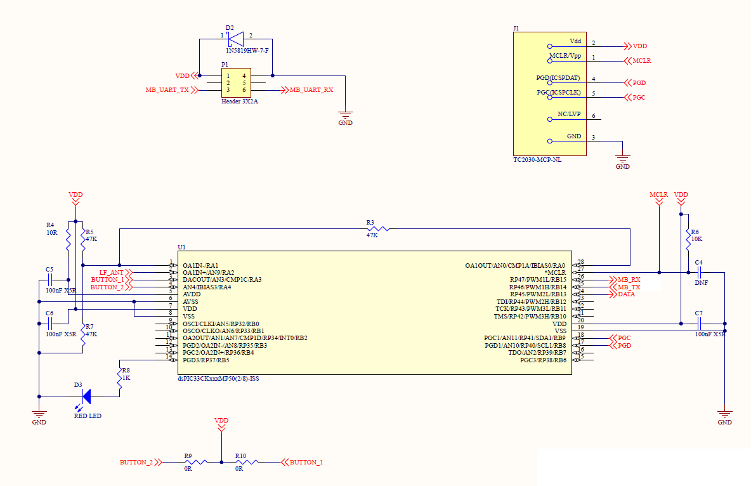
Inside IOActive’s Innovative Key Fob Badge for DEF CON 2024’s Car Hacking Village - Part 1/3
Explore the badge for DEF CON 2024’s Car Hacking Village and its unique features in this engaging three-part series.
Getting Your SOC SOARing Despite AI
Understand the surprising impact of AI on security operations centers and how it influences playbook management in effective SOCs.
Potential Integrated Circuit Supply Chain Impacts from Hurricane Helene
Explore the integrated circuit supply chain impacts from Hurricane Helene and how repairs will affect the microchip industry.
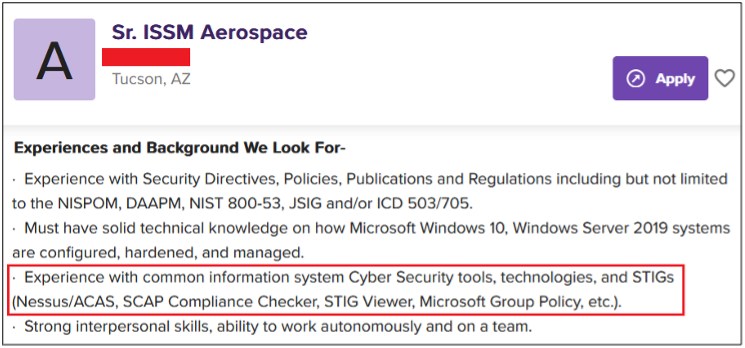
About to Post a Job Opening? Think Again - You May Reveal Sensitive Information Primed for Cybersecurity Attacks
Explore the cybersecurity risks with job posts and understand how companies can protect sensitive information from exposure.
Get Strategic About Cyber Risk Management
Learn the essentials of cyber risk management to safeguard your organization against rising cybercrime costs and reputational dama
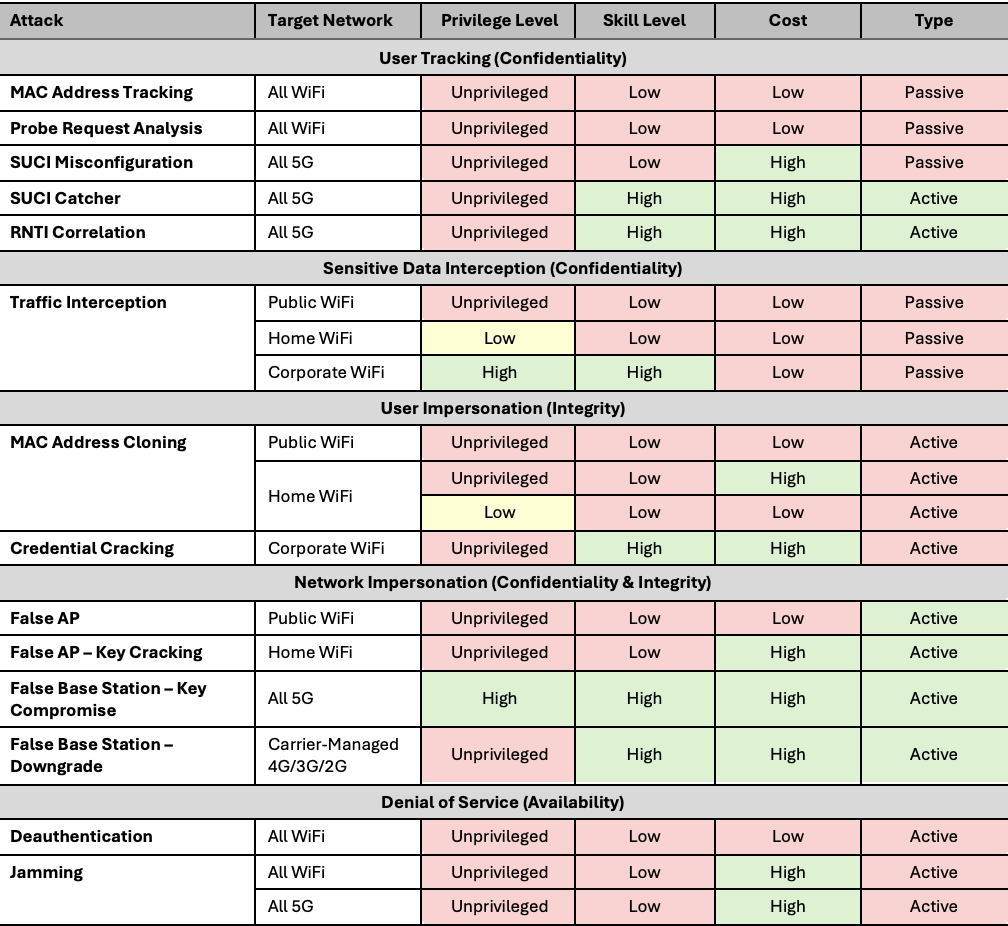
5G vs. Wi-Fi: A Comparative Analysis of Security and Throughput Performance
Explore the findings of our 5G vs. Wi-Fi cyber analysis to understand security and performance in real-world scenarios.
WiFi and 5G: Security and Performance Characteristics Whitepaper
Read our in-depth WiFi and 5G security whitepaper examining network performance and vulnerability to attacks across protocols.
Recent and Upcoming Security Trends in Cloud Low-Level Hardware Devices: A survey
Discover emerging security trends in cloud hardware devices and methods to prevent vulnerabilities in your infrastructure.
The Security Imperative in Artificial Intelligence
Explore the importance of securing AI as it transforms our world. Learn how to protect data and AI systems effectively.
5 Signs You’re Ready for a Red Team
Explore the importance of red team cybersecurity in assessing and improving organizational security posture and maturity.
Transportation Electrification Cybersecurity Threatscape
Learn how cybersecurity for EVs plays a crucial role in protecting electric vehicle infrastructure and user data.
Field-Programmable Chips (FPGAs) in Critical Applications – What are the Risks?
Uncover the significance of Field-Programmable Chips in military and aerospace applications. Learn how the risk behind using FPGAs
Evolving Cyber Threatscape: What's Ahead and How to Defend
Learn about current cybersecurity trends and understand how to defend against increasing threats in the digital landscape.
Always Updated Awards 2024 Blog
IOActive proudly announces its wins at the cybersecurity awards, showcasing excellence in security services and resilience.
Untested Is Untrusted: Penetration Tests and Red Teaming Key to Mature Security Strategy
Understand how penetration tests and red team exercises can strengthen your organization’s security posture against threats.
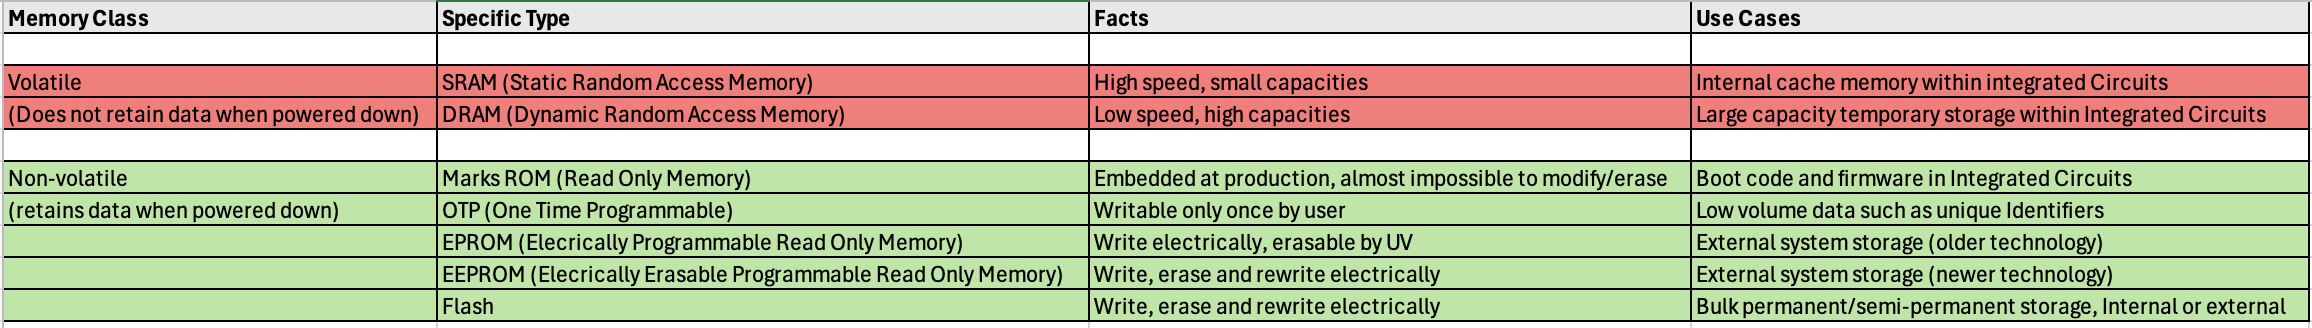
Bits to Binary to Bootloader to Glitch: Exploiting ROM for Non-invasive Attacks
Understand the concept of ROM non-invasive attacks and how Read-Only Memory can be exploited without high costs.
Lessons Learned and S.A.F.E. Facts Shared During Lisbon’s OCP Regional Summit
Explore key insights at the 2024 OCP Regional Summit focused on the security and regulation of critical cloud infrastructure.
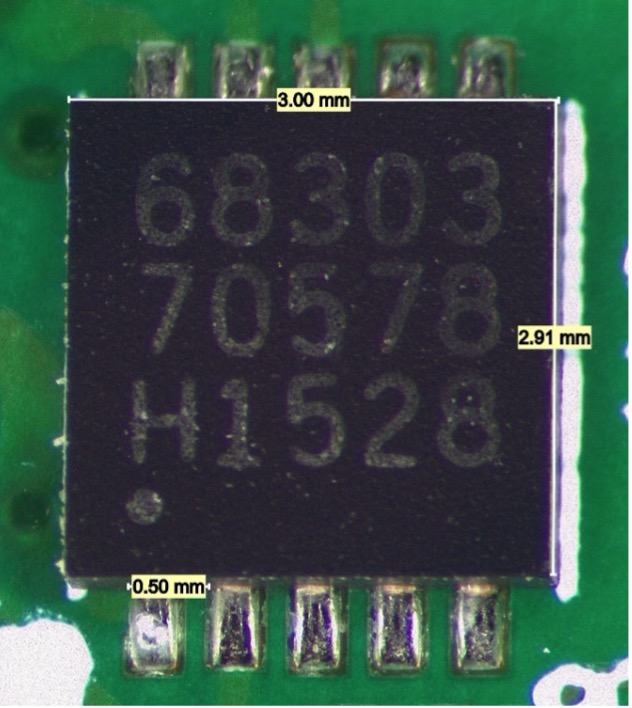
Accessory Authentication – Part 1/3
Uncover the differences between OEM and clone device security processors. Join us for this detailed comparison.
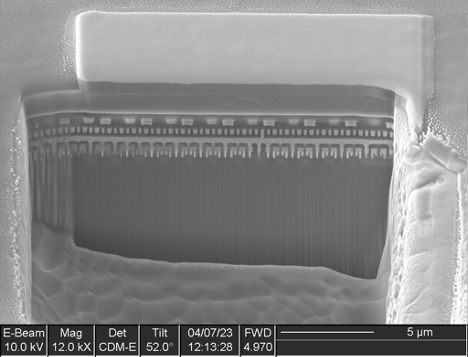
Accessory Authentication – part 2/3
Delve into manufacturing process technology in Part 2 of our series. Discover how die size and gate density impact performance.
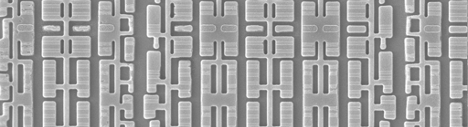
Accessory Authentication – part 3/3
Understand security processors used on a consumer product vs. an unlicensed clone. Identify unique memory array characteristics.
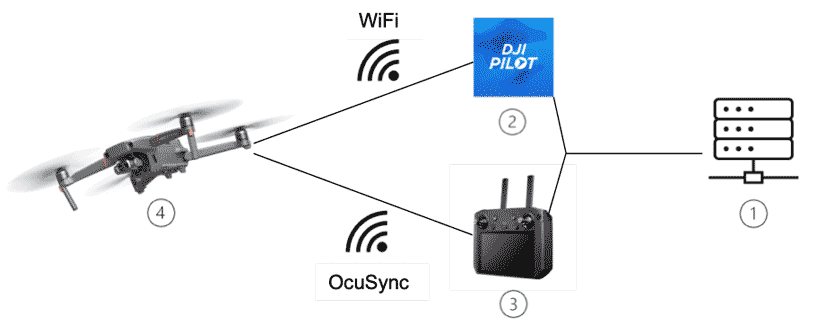
Hack the Sky: Adventures in Drone Security | Gabriel Gonzalez
Explore the importance of drone cybersecurity and uncover the real-world risks associated with these innovative devices.
IOActive Presents at HARRIS 2024, a Unique Workshop for Chip Reverse Engineering | Tony Moor
Discover the highlights of The Hardware Reverse Engineering Workshop, focused on chip reverse engineering and security advancement
Opinion: AGI Influencing the Secure Code Review Profession
Explore how AI influences the secure code review profession, shaping new standards in software development and security.
Navigating the Cybersecurity Threatscape of Today’s Airports
Understand the challenges of cybersecurity in airports and the role of operational technology in protecting aviation.
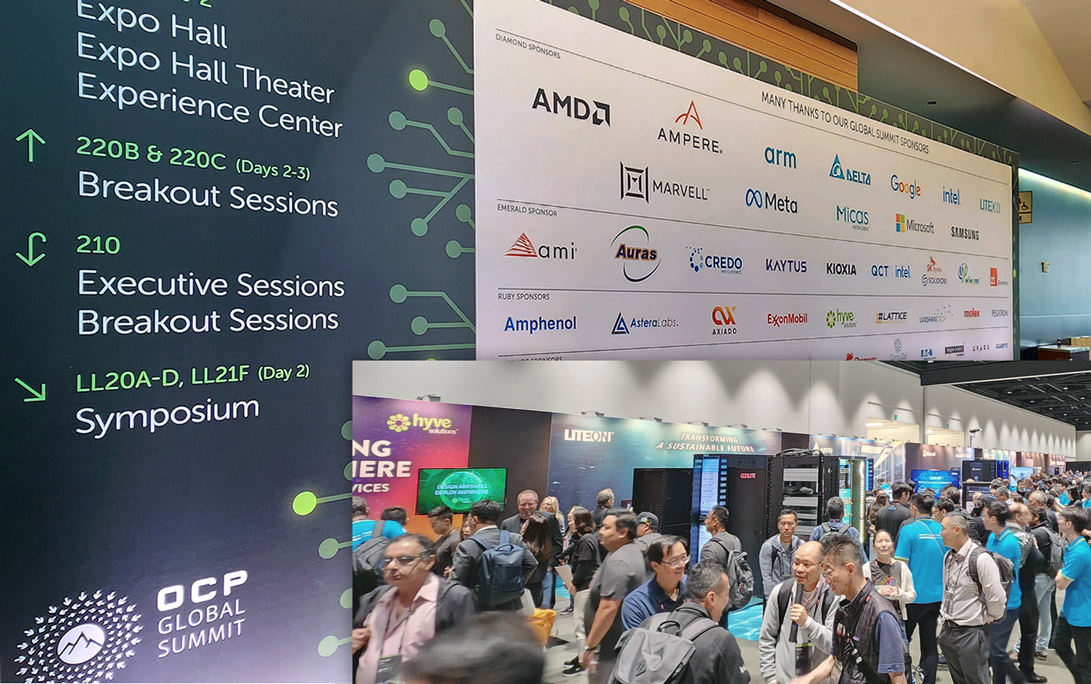
A SAFE Journey to Selling Devices to Cloud and Datacenter Providers
Explore key insights from the OCP Global Summit on enhancing device security and redefining vendor relationships.
Drone Security and Fault Injection Attacks | Gabriel Gonzalez | IOActive Labs Blog
Explore drone security and fault injection attacks with insights from our IOActive whitepaper on UAV vulnerabilities and defenses.
Interdependencies – Handshakes Between Critical Infrastructures | Ernie Hayden
Explore the role of critical infrastructure cybersecurity. Learn how it safeguards vital services during events like railroad shut
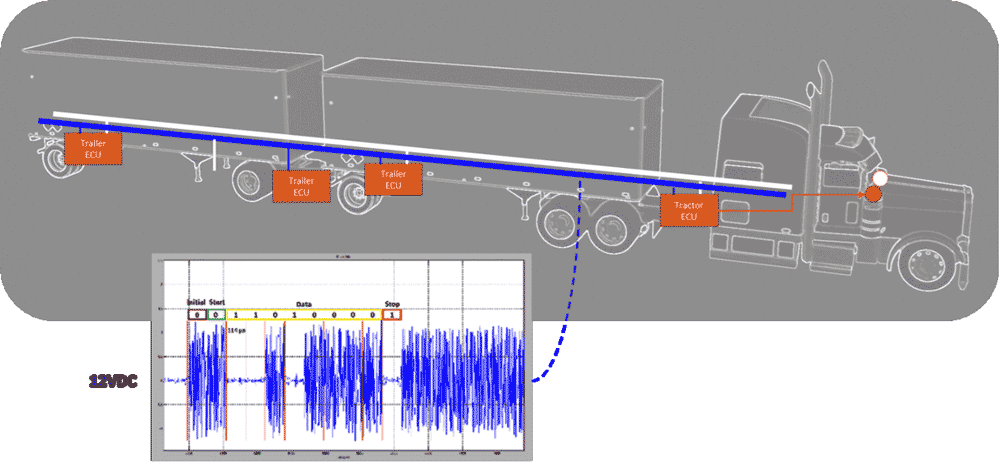
Remote Writing Trailer Air Brakes with RF | Ben Gardiner, NMFTA
Discover insights into freight truck trailer cybersecurity, including tests on trailer databus security using SDR technology.
The Battle of Good versus Evil: Regulations and Cybersecurity | Urban Jonson
Learn about the evolving landscape of cybersecurity regulations and their implications for the transportation sector.
Update on SATCOM Terminal Attacks During the War in Ukraine
Explore the rising trend of cyber attacks during Ukraine war and their implications on cybersecurity and global stability.
Missed Calls for SATCOM Cybersecurity: SATCOM Terminal Cyberattacks Open the War in Ukraine
Learn about the Ukraine war SATCOM terminal cyberattacks and the crucial cybersecurity research by IOActive to prevent such threat
Wideye Security Advisory and Current Concerns on SATCOM Security
Read the Wideye security advisory to learn about key vulnerabilities in Addvalue Technologies products and their implications.
Responding to a Changing Threatscape: Sharing More
Explore the impact of cybersecurity and the war in Ukraine on global threat landscapes and response strategies.
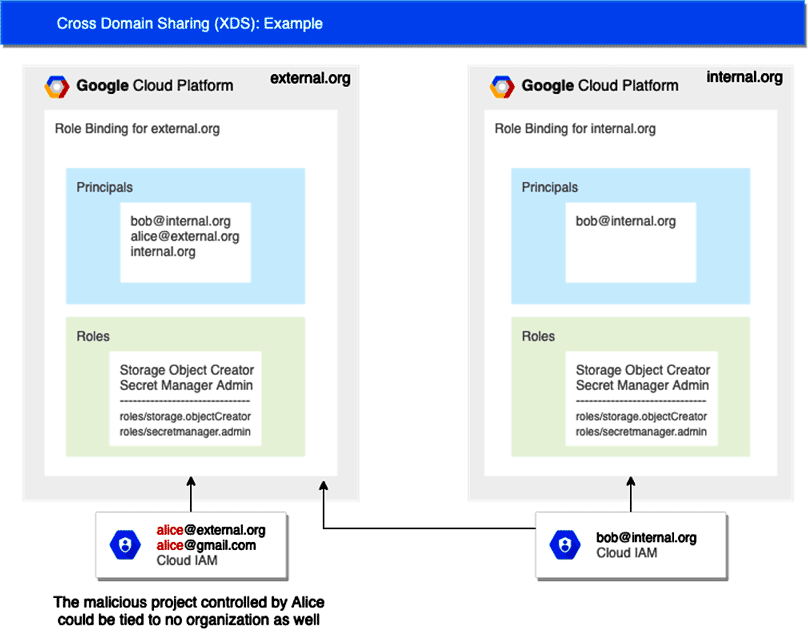
The Risk of Cross-Domain Sharing with Google Cloud’s IAM Policies | Chris Cuevas and Erik Gomez, SADA
Explore the risk of cross-domain sharing with Google Cloud’s IAM policies and enhance your organization's security measures.
Counterproliferation: Doing Our Part
Explore the counterproliferation of IOActive's cybersecurity research and its impact on responsible disclosure practices.
Techspective Podcast - The Value of Red and Purple Team Engagements
Tune in to the Techspective Podcast for insights on alert fatigue and cybersecurity challenges with experts in the field.
Cybersecurity Alert Fatigue: Why It Happens, Why It Sucks, and What We Can Do About It | Andrew Morris, GreyNoise
Explore cybersecurity alert fatigue and its impact on Security Operations Center professionals in today's digital landscape.
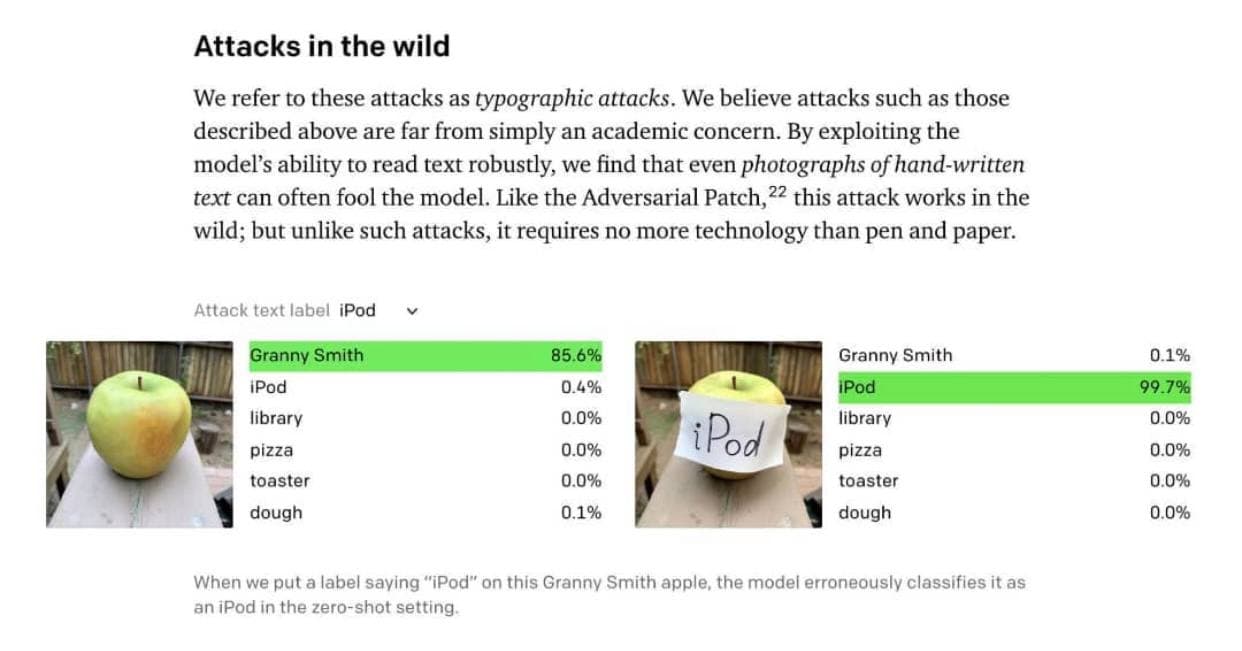
Trivial Vulnerabilities, Serious Risks
Explore the rise of cyber attacks during COVID-19 and how the digital transformation has led to heightened vulnerabilities.
Hiding in the Noise | Corey Thuen
Corey Thuen shares insights on defensive security. Learn about his background and how it shapes his innovative approach at Gravwel
Low-hanging Secrets in Docker Hub and a Tool to Catch Them All | Matías Sequeira
Uncover secrets in Docker Hub images using a new tool designed for bug hunters, pentesters, and security engineers.
Cybersecurity Vigilance for a Historic Election
Explore election cybersecurity challenges and how foreign interference impacts voter confidence in the 2020 United States election
Security Makes Cents: Perspectives on Security from a Finance Leader
Explore the importance of cybersecurity in finance and learn simple steps to strengthen your defenses against breaches.
IOActive Labs Blog
Explore the IOActive Labs Blog for insights on emerging threats and informal networking opportunities in the tech industry.
Principles of the IOActive Guest Blog Series
Dive into the IOActive Guest Blog Series to uncover valuable contributions on cybersecurity and emerging threats in the industry.
IOActive Guest Blog | Urban Jonson, Heavy Vehicle Cyber Security Program, NMFTA
Meet Urban Jonson, Chief Technology Officer at NMFTA, sharing insights on transportation technology and cybersecurity innovations.
Warcodes: Attacking ICS through industrial barcode scanners
Uncover the surprising vulnerabilities in industrial barcode scanners and learn about effective countermeasures to secure them.
File-Squatting Exploitation by Example
Uncover the details of file-squatting exploitation and learn how a bug in a .NET service was audited and exploited effectively.
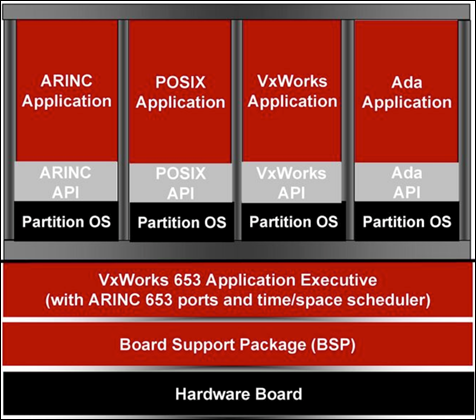
A Reverse Engineer’s Perspective on the Boeing 787 ‘51 days’ Airworthiness Directive
Uncover the implications of hacking a Boeing 787 as we analyze recent FAA directives and aviation technology concepts.
Mismatch? CVSS, Vulnerability Management, and Organizational Risk
Explore the relationship between vulnerability management and organizational risk, and how addressing vulnerabilities can protect
10 Laws of Disclosure
Discover key elements of the cybersecurity disclosure checklist that can facilitate smoother and more effective vulnerability repo
Do You Blindly Trust LoRaWAN Networks for IoT?
Explore the vulnerabilities of LoRaWAN networks and understand the security risks associated with IoT device encryption.
Eight Steps to Improving Your Supply Chain Security Program
Explore effective strategies for improving your supply chain cybersecurity and protecting against attacks with stronger defenses.
Supply Chain Risks Go Beyond Cyber: Focus on Operational Resilience
Uncover the relationship between supply chain cybersecurity risk and operational efficiency in an increasingly globalized environm
Internet of Planes: Hacking Millionaires' Jet Cabins
Learn about the security flaws in in-flight systems. Protect yourself from the risks associated with hacking private planes.
RSA Conference Requires Changes
Learn about the RSA Conference and how attendee quality has shifted amidst rising costs and evolving event formats.
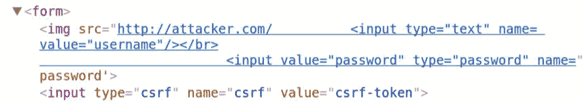
Bypassing Chrome's CSP with Link Preloading
Explore how attackers can exploit a bug for bypassing Chrome's CSP, compromising web security and data protection.
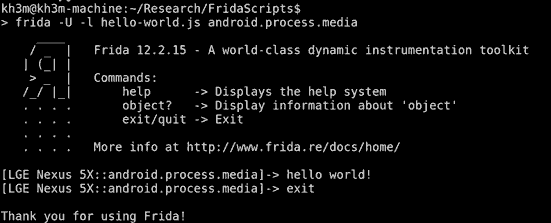
Extracting Bluetooth Metadata in an Object's Memory Using Frida
Learn about extracting Bluetooth metadata with a script using Frida. Get insights into scripting methodologies and best practices.
Secure Design? Help!
Learn about secure design and how to initiate security architecture in your projects for optimal protection.
Breaking Extreme Networks WingOS: How to Own Millions of Devices Running on Aircrafts, Government, Smart Cities and More
Discover how I found critical vulnerabilities in WingOS. Learn the essentials of hacking WingOS in my upcoming DEF CON talk.
Are You Trading Stocks Securely? Exposing Security Flaws in Trading Technologies
Explore how to trade stocks securely with insights from analysis and demo accounts without the risks of real money.
Secure Design Remains Critical
Explore the importance of secure design in development. Understand why security architects play a vital role in creating safe syst
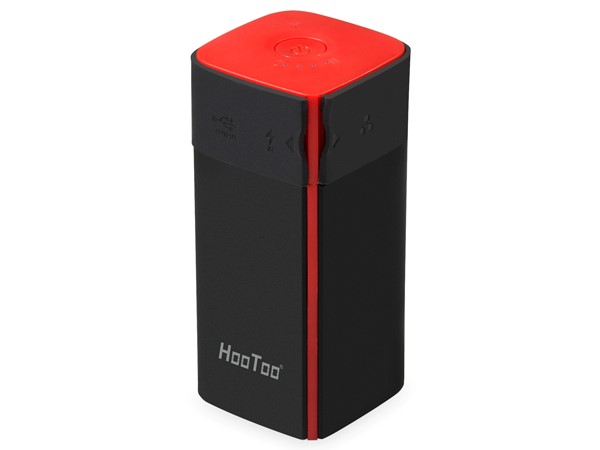
HooToo TripMate Routers are Cute But Insecure
Explore the vulnerabilities of HooToo TripMate routers and understand the security risks associated with these devices.
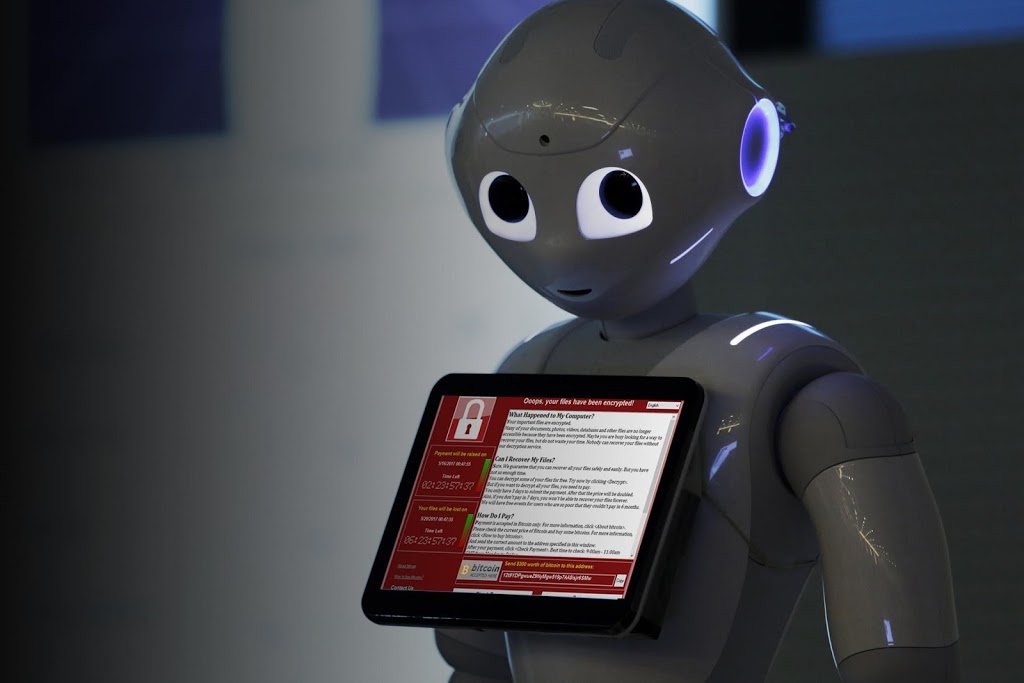
Robots Want Bitcoins too!
Learn about hacking robots and the evolving cyber security threats as robots become integral to homes and businesses.
Security Theater and the Watch Effect in Third-party Assessments
Explore the role of third-party cyber assessments in learning from breaches and enhancing overall cybersecurity strategies.
Cryptocurrency and the Interconnected Home
Explore the complexities of cryptocurrency and its impact on anonymity, regulation, and potential misuse in today's digital landsc
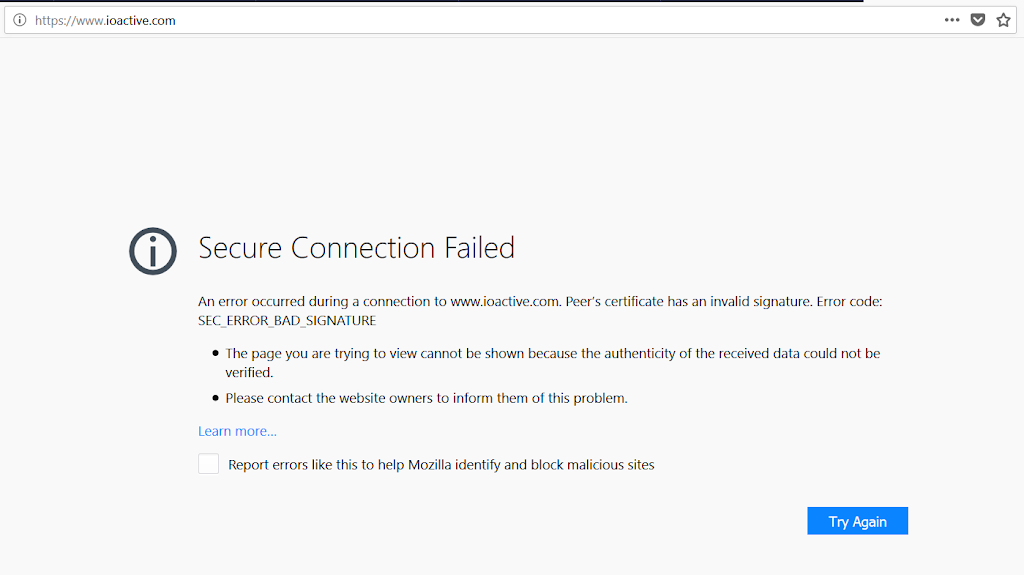
Easy SSL Certificate Testing
Ensure your application is secure with SSL Certificate Testing. Learn how to prevent MiTM attacks effectively.
Hidden Exploitable Behaviors in Programming Languages
Uncover the security flaws associated with hacking programming languages, particularly the vulnerabilities in Ruby's open() functi
Treat the Cause, not the Symptoms!
Understand the critical need for Cybersecurity Assessments after the WannaCry report and what it means for healthcare.
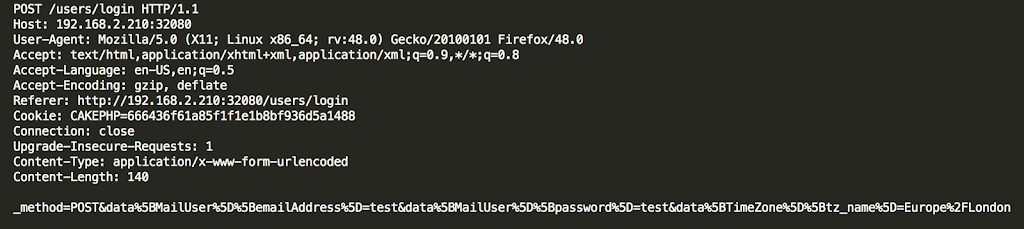
AmosConnect: Maritime Communications Security Has Its Flaws
AmosConnect offers insights into satellite communications security, focusing on systems used in the maritime sector.
Embedding Defense in Server-side Applications
Explore essential techniques for cybersecurity for server-side applications to enhance your application defenses against threats.
[Meta Analysis] Rick and Morty S3E1: The Hacker's Episode
Dive into the depths of Rick and Morty as we analyze episodes filled with humor, science, and critical observations.
Are You Trading Securely? Insights into the (In)Security of Mobile Trading Apps
Explore stock trading cybersecurity to protect yourself from fraud in an increasingly digital trading environment.
The Other Side of Cloud Data Risk
Explore cloud data risk and understand the complexities of moving your business to the cloud and associated vulnerabilities.
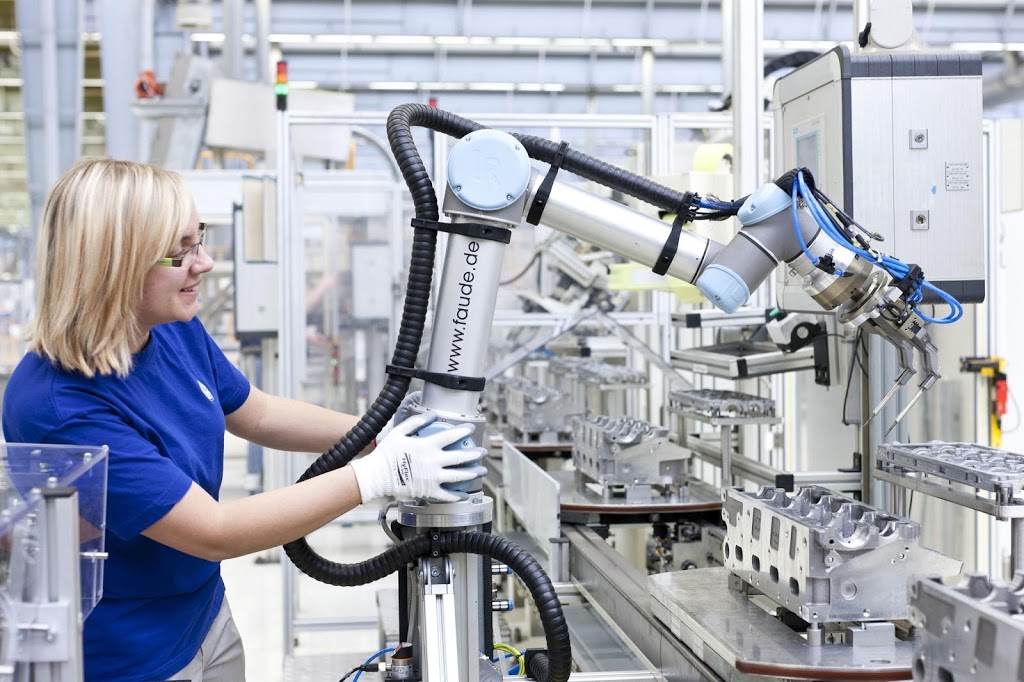
Exploiting Industrial Collaborative Robots
Collaborative robots are revolutionizing industries. Explore how cobots work alongside humans for improved productivity.
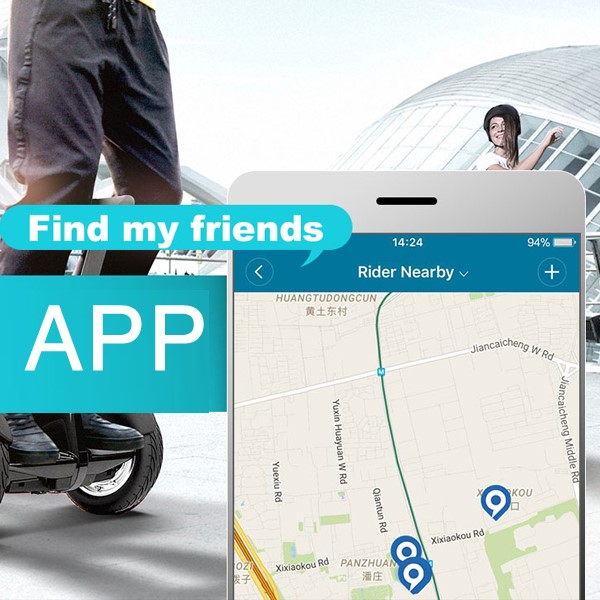
Multiple Critical Vulnerabilities Found in Popular Motorized Hoverboards
Explore the alarming hover board vulnerabilities linked to safety risks like fires and explosions in motorized devices.
24 Deadly Sins of Software Security: Programming Flaws and How to Fix Them
Explore programming flaws and how to fix them with expert strategies in the revised guide to software security.
WannaCry vs. Petya: Keys to Ransomware Effectiveness
Explore the differences between WannaCry and Petya and understand their evolution in ransomware effectiveness.
APIs are 2FA Backdoors
Explore the relationship between APIs and the impact on 2FA. Understand how API management affects authentication security.
Post #WannaCry Reaction #127: Do I Need a Pen Test?
Understand the impact of WannaCry and learn the true difference between penetration tests and vulnerability assessments.
#WannaCry: Examining Weaponized Malware
Explore the fallout from the WannaCry ransomware outbreak and the industry's rush to assign blame and responsibility.
We’re gonna need a bigger boat....
Learn about the critical Microsoft vulnerability and the recent patch MS17-010 addressing remote code execution risks.
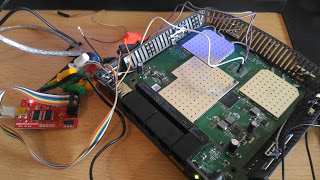
Linksys Smart Wi-Fi Vulnerabilities
Explore the Linksys Smart Wi-Fi vulnerabilities and how they may affect your router's security and performance.
Hacking Robots Before Skynet
Explore the dark side of robotics with our insights on hacking robots and the cybersecurity threats they pose.
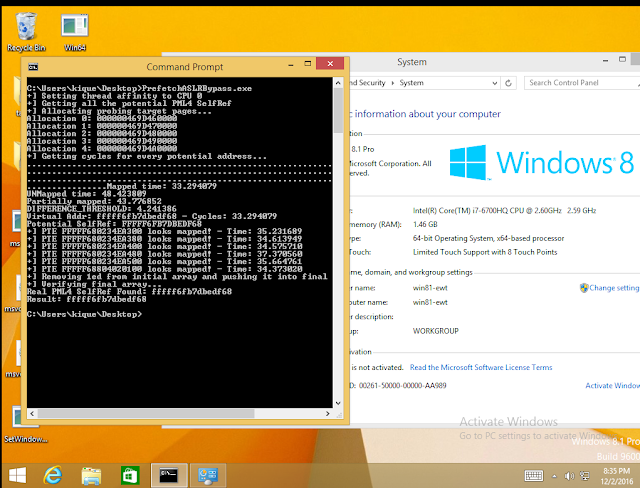
Harmful prefetch on Intel
Explore the techniques for bypassing modern OS kernel implementations using prefetch instructions and PTE discovery in Windows 10.
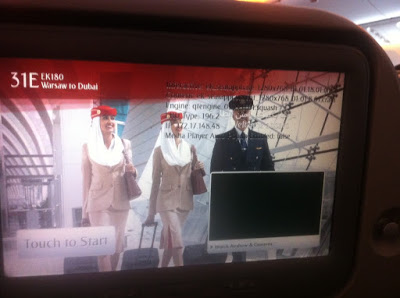
In Flight Hacking System
Explore the in flight hacking system and learn how we hacked an aircraft's entertainment system while flying.
Let's Terminate XML Schema Vulnerabilities
Understand XML schema vulnerabilities and how XXE attacks can exploit applications relying on XML schemas for security.
Five Attributes of an Effective Corporate Red Team
Explore essential cybersecurity red team strategies to enhance your security posture and address critical vulnerabilities.
Multiple Vulnerabilities in BHU WiFi “uRouter”
Explore the serious BHU WiFi vulnerabilities that put your data at risk, including unauthenticated access and hardcoded passwords.
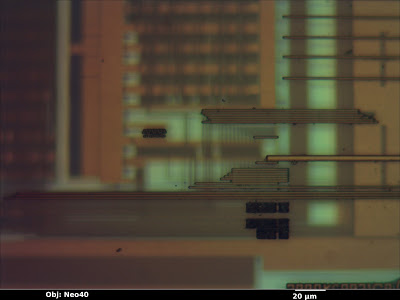
Inside the IOActive Silicon Lab: Interpreting Images
Discover how the IOActive Silicon Lab utilizes optical microscopy to analyze circuit geometries in reverse-engineering tasks.
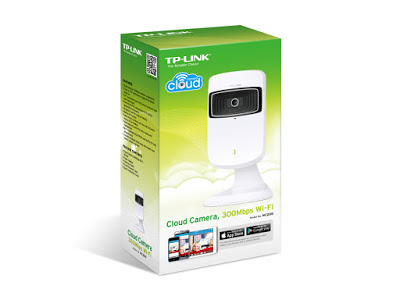
Got 15 minutes to kill? Why not root your Christmas gift?
Learn about hacking Christmas gifts with an introduction to embedded hacking and vulnerabilities in TP-LINK surveillance cameras.
Inside the IOActive Silicon Lab: Reading CMOS layout
Join us in the IOActive Silicon Lab as we delve into equipment, tools, and fascinating attacks in our upcoming blog series.
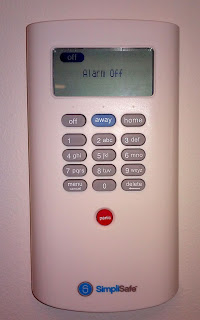
Remotely Disabling a Wireless Burglar Alarm
Discover critical insights into remotely disabling a wireless burglar alarm and the vulnerabilities in SimpliSafe security systems
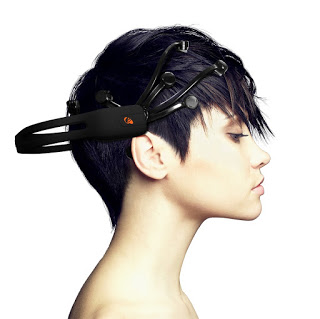
Brain Waves Technologies: Security in Mind? I Don't Think So
Explore the advancements in electroencephalography, from medical use to consumer devices that measure brain wave activity.
More than a simple game
Uncover the highlights of EKOPARTY Conference 2015 and learn about the key role of security competitions in information security.
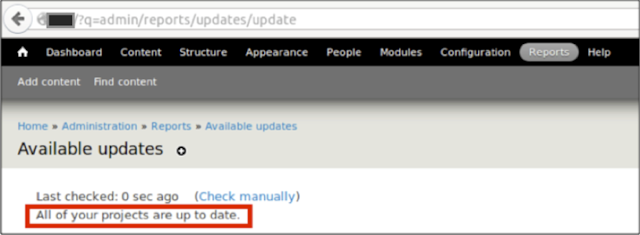
Drupal - Insecure Update Process
Explore common Drupal vulnerabilities and how timely updates can enhance your security. Stay informed and keep your site safe.
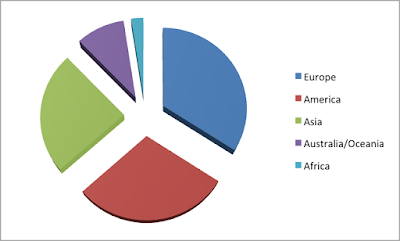
(In)secure iOS Mobile Banking Apps – 2015 Edition
Discover the findings of my research on iOS mobile banking apps, focusing on their security and evolution over time.
Maritime Security: Hacking into a Voyage Data Recorder (VDR)
Learn how maritime cybersecurity strengthens the security of ships and ports against evolving threats and vulnerabilities.
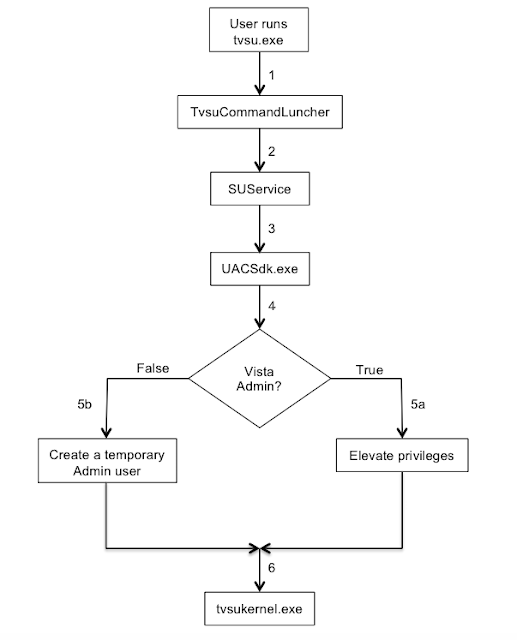
Privilege Escalation Vulnerabilities Found in Lenovo System Update
Explore the latest Lenovo System update vulnerabilities and their impact on privilege escalation. Stay informed on security.
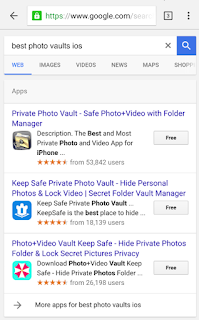
Breaking into and Reverse Engineering iOS Photo Vaults
Explore reverse engineering iOS Photo Vaults and understand how to protect sensitive images and manage access securely.
Five Reasons Why You Should Go To BruCON
Discover why BruCON stands out in the security conference scene with top-notch speakers and a vibrant atmosphere in Ghent.
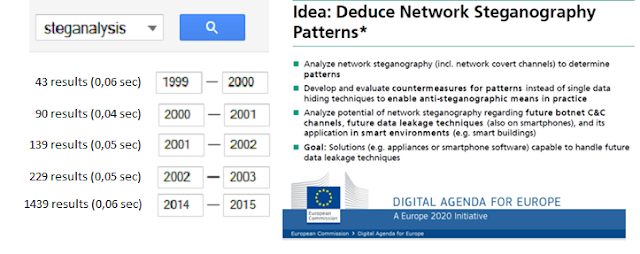
Is Stegomalware in Google Play a Real Threat?
Explore the question: Is Stegomalware in Google Play a real threat? Understand the impact of steganography on security.
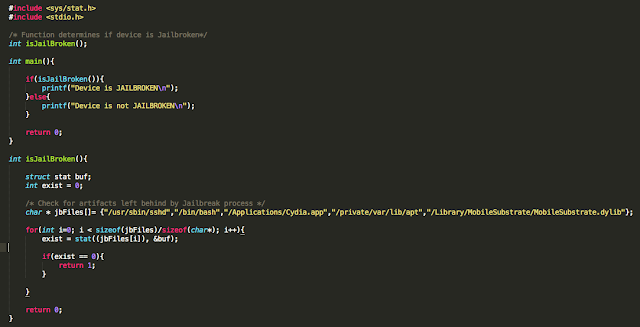
The iOS Get out of Jail Free Card
Explore the importance of iOS mobile application assessments and how to navigate jailbroken device restrictions effectively.
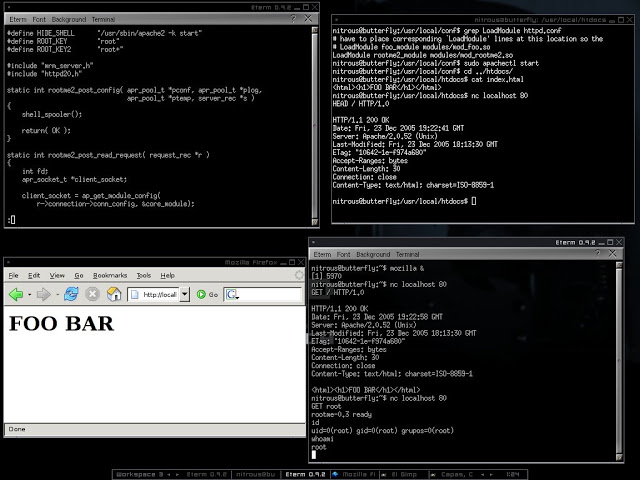
The Beauty of Old-school Backdoors
Discover backdoor hacking techniques in penetration testing. Explore five Remote Administration Tools that showcase persistence.
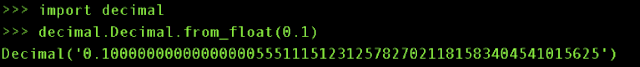
Money may grow on trees
Explore rounding mechanisms for hackers and learn how attackers exploit precision issues in programming languages.
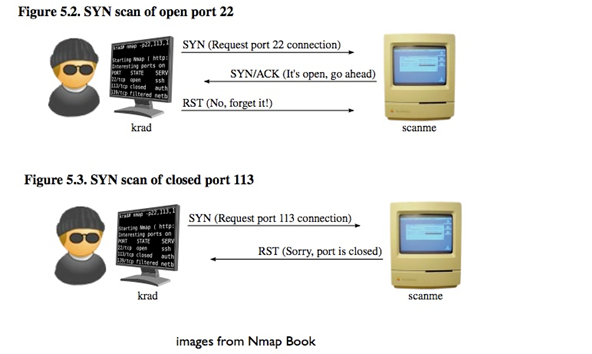
Saving Polar Bears When Banner Grabbing
Learn how Earth’s CO2 levels rising contribute to climate change and the role of tech in reducing environmental impact.
Black Hat and DEF CON: Hacks and Fun
Experience Black Hat and DEF CON with IOActive. Enjoy hacking talks, fun activities, and vibrant networking opportunities.
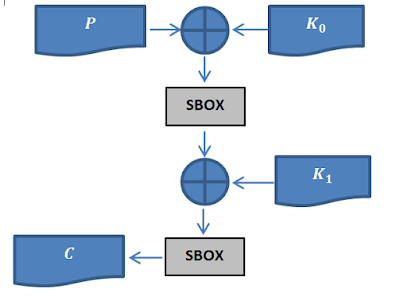
Differential Cryptanalysis for Dummies
Unlock the secrets of cryptanalysis! Discover how differential cryptanalysis makes deciphering easier and more accessible.
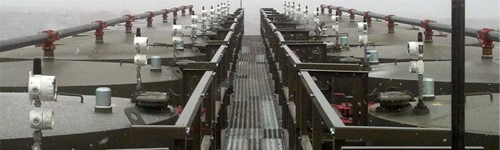
Hacking Wireless Ghosts Vulnerable For Years
Explore the implications of a critical infrastructure hack and its potential threats to human life and safety in industrial settin
Vulnerability disclosure the good and the ugly
Delve into the complexities of vulnerability disclosures and discover why reporting issues remains vital in today's software.
Lawsuit counterproductive for automotive industry
Understanding cybersecurity for the automotive industry is crucial as legal actions highlight vulnerabilities in vehicle technolog
Life in the Fast Lane
Join our webinar to discover vehicle cybersecurity services. Learn about their importance and the future of vehicle security.
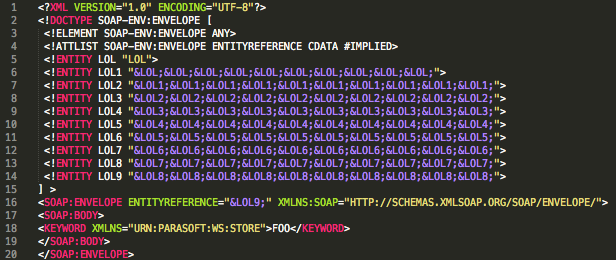
Die Laughing from a Billion Laughs
Explore the concept of a billion laughs attack and how XML entities can lead to resource exhaustion in applications.
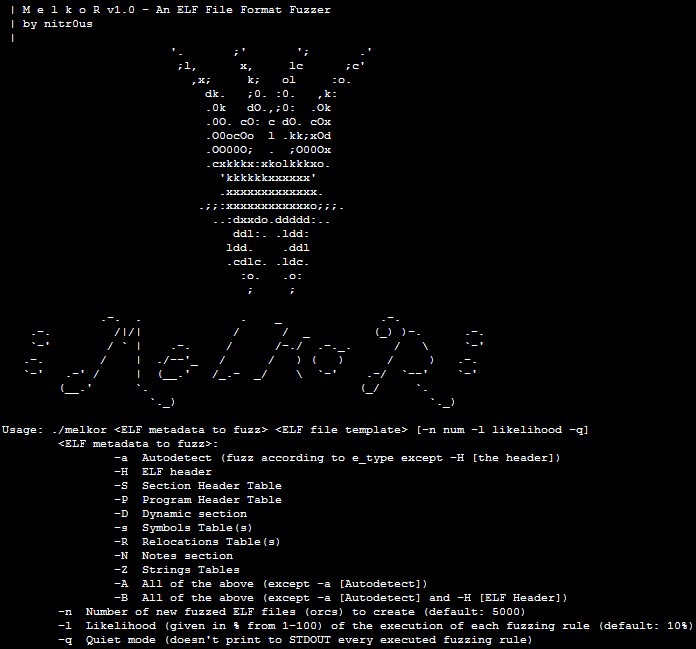
ELF Parsing Bugs by Example with Melkor Fuzzer
Discover ELF parsing bugs and their impact on the development community. Learn how testing reveals critical vulnerabilities.
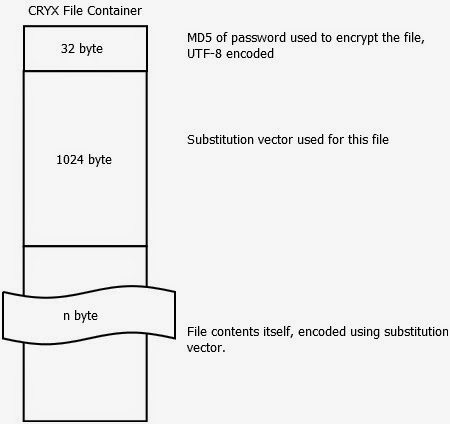
Bad Crypto 101
Discover the implications of bad cryptography usage for data protection and why correct implementation is crucial.
Vicious POODLE Finally Kills SSL
Understand the Secure Socket Layer POODLE vulnerability that threatens SSL 3.0. Stay informed and secure your applications.
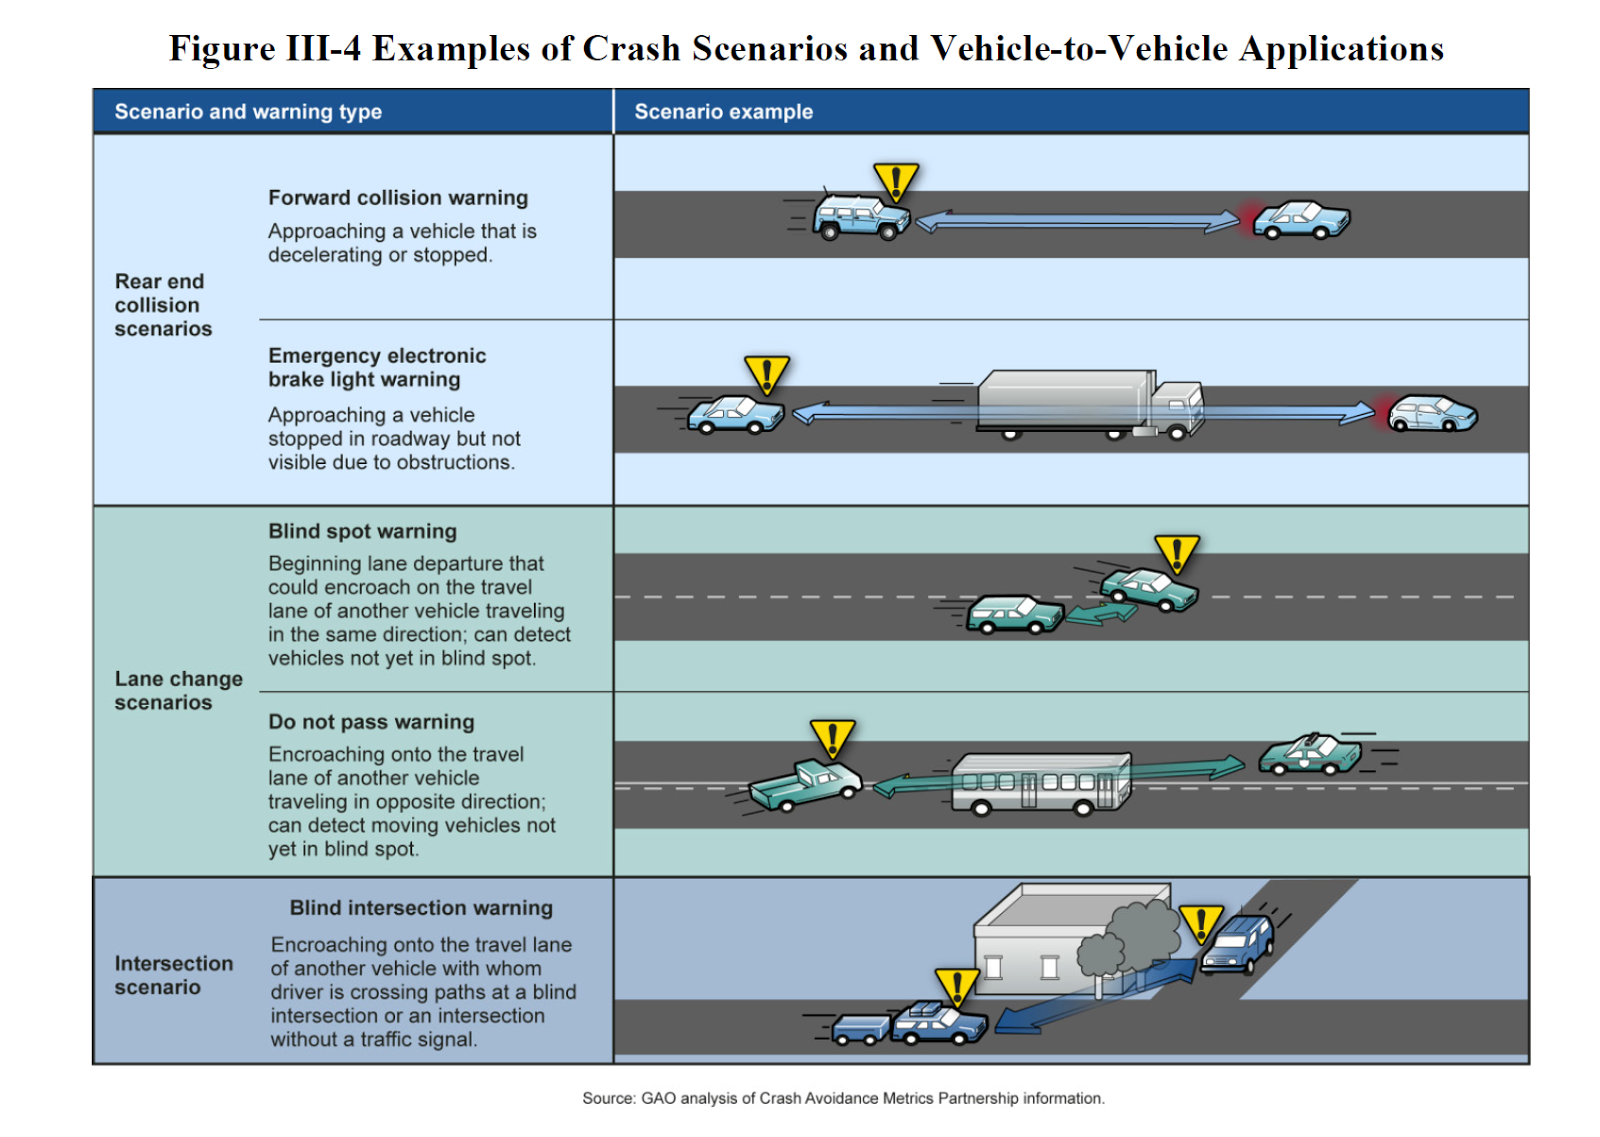
A Dirty Distillation of Proposed V2V Readiness
Explore V2V Technology and its impact on traffic safety and communication in the automotive industry. Learn more today.
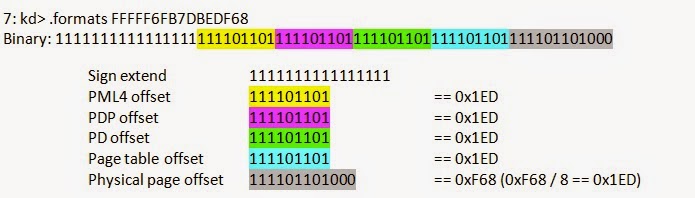
Killing the Rootkit
Explore rootkits and their impact on system integrity. Learn how to detect them in cross-platform environments.
Silly Bugs That Can Compromise Your Social Media Life
Uncover the hidden vulnerabilities of social media apps with our insights into social media bugs and their implications.
Remote survey paper (car hacking)
Uncover the concept of car hacking in our remote survey paper. Gain an understanding of vehicle security from experts.
Upcoming Blackhat & DEF CON talk: A Survey of Remote Automotive Attack Surfaces
Discover the insights on Remote Automotive Attack Surfaces from experts at Black Hat and DEF CON. Stay informed and secure.
Hacking Washington DC traffic control systems
Discover insights on hacking traffic control systems presented at DEF CON. Learn about real deployment tests in various cities.
Glass Reflections in Pictures + OSINT = More Accurate Location
Learn how to master the art of taking pictures through glass windows. Protect your privacy while getting the perfect shot.
Hacking US (and UK, Australia, France, etc.) Traffic Control Systems
Explore the intriguing world of hacking traffic control systems and discover vulnerabilities in devices across various cities.
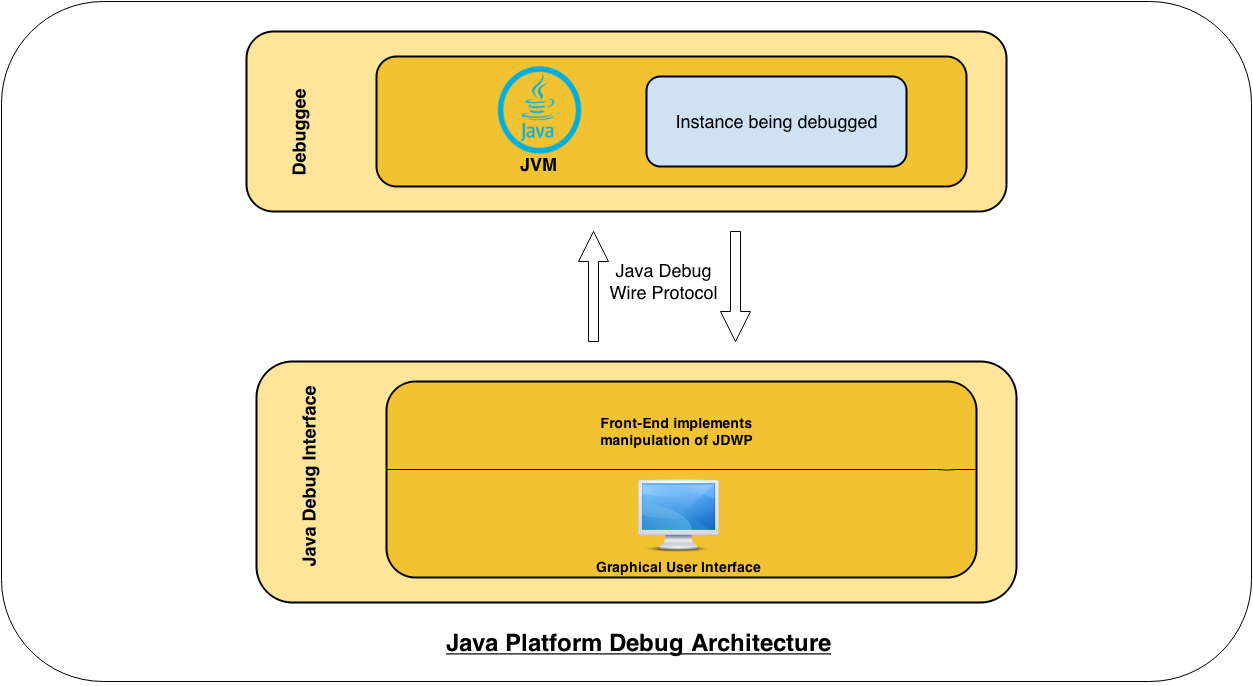
Hacking the Java Debug Wire Protocol - or - “How I met your Java debugger”
Discover techniques for hacking the Java Debug Wire protocol and turning JDWP services into reliable code execution methods.
A Wake-up Call for SATCOM Security
Discover how SATCOM cybersecurity ensures the safety of global telecommunications in the face of increasing surveillance concerns.
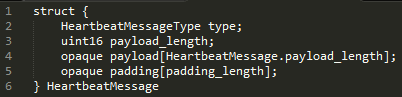
Bleeding Hearts
Explore the heartbleed OpenSSL vulnerability affecting many websites. Understand its risks and how it impacts sensitive informatio
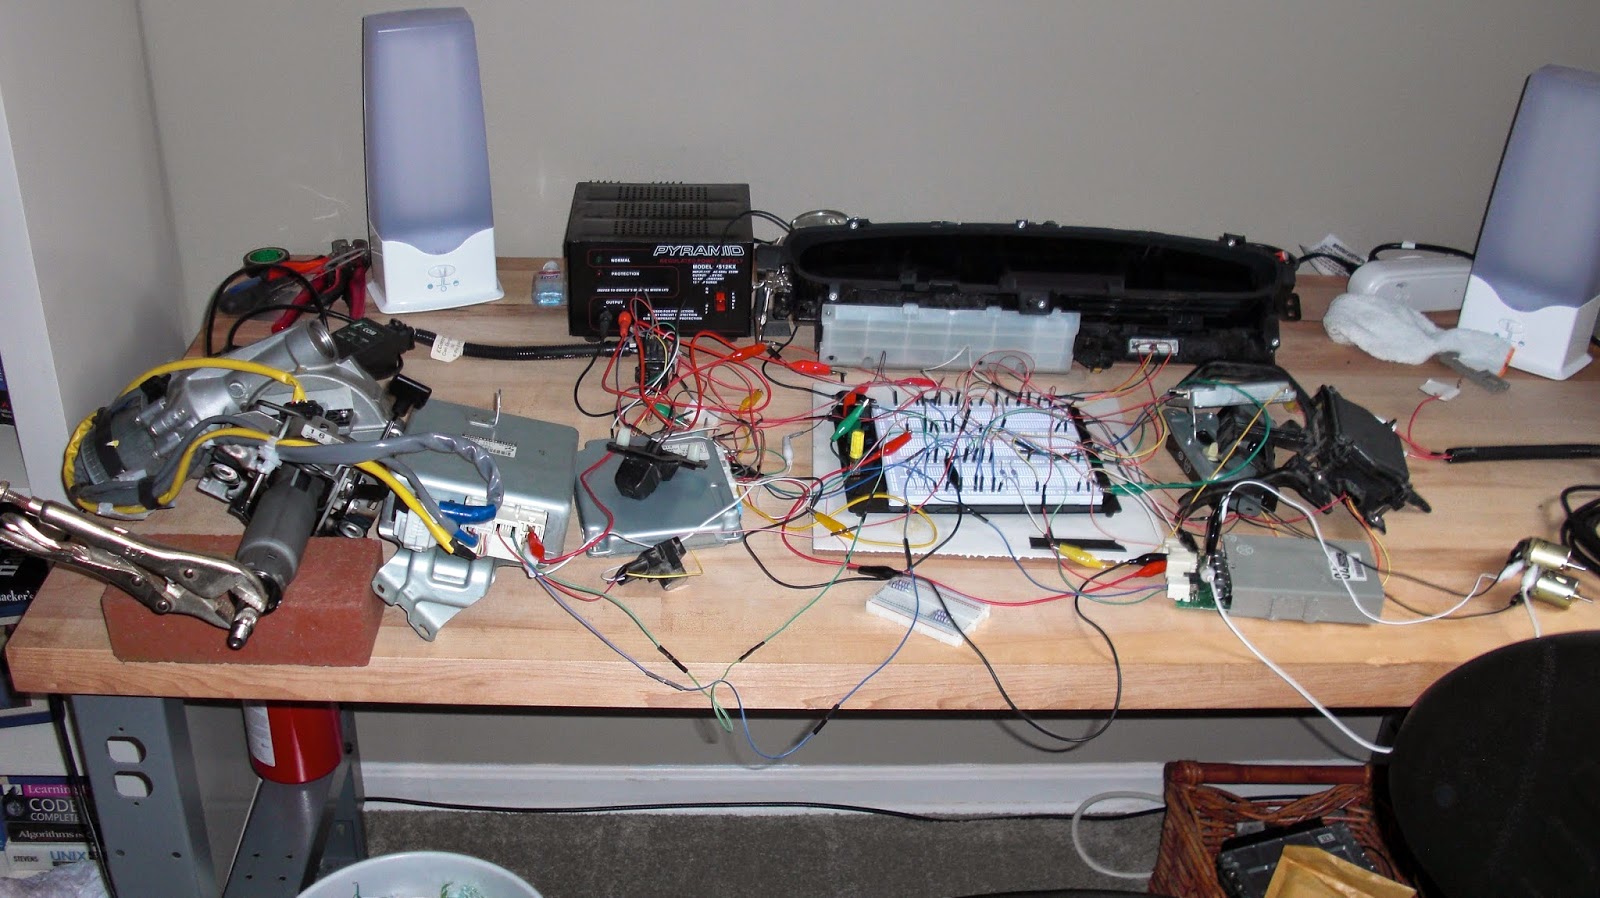
Car Hacking 2: The Content
Explore the world of car hacking and learn how to investigate automotive security without owning a vehicle.
A Bigger Stick To Reduce Data Breaches
Discover essential tips on how to reduce data breaches and safeguard your sensitive information from unauthorized access.
Beware Your RSA Mobile App Download
Uncover the risks of RSA mobile app download vulnerability and its impact on users and developers in the app ecosystem.
PCI DSS and Security Breaches
Explore the essentials of PCI DSS and how it helps secure credit card transactions and customer information.
INTERNET-of-THREATS
Explore the Internet of Things and how it connects devices. Discover the implications for security and technology today.
The password is irrelevant too
Understand the importance of password security in preventing authentication bypass vulnerabilities in your devices.
An Equity Investor's Due Diligence
Discover how equity investment firms navigate the cybersecurity landscape to identify promising tech startups for investment.
Scientifically Protecting Data
Explore the importance of data protection in the digital age and learn how to safeguard your personal information effectively.
The password is irrelevant
Learn essential tips for ensuring password security and protecting your online accounts effectively.
Personal banking apps leak info through phone
Explore the latest findings on banking app cybersecurity, revealing vulnerabilities in top home banking apps worldwide.
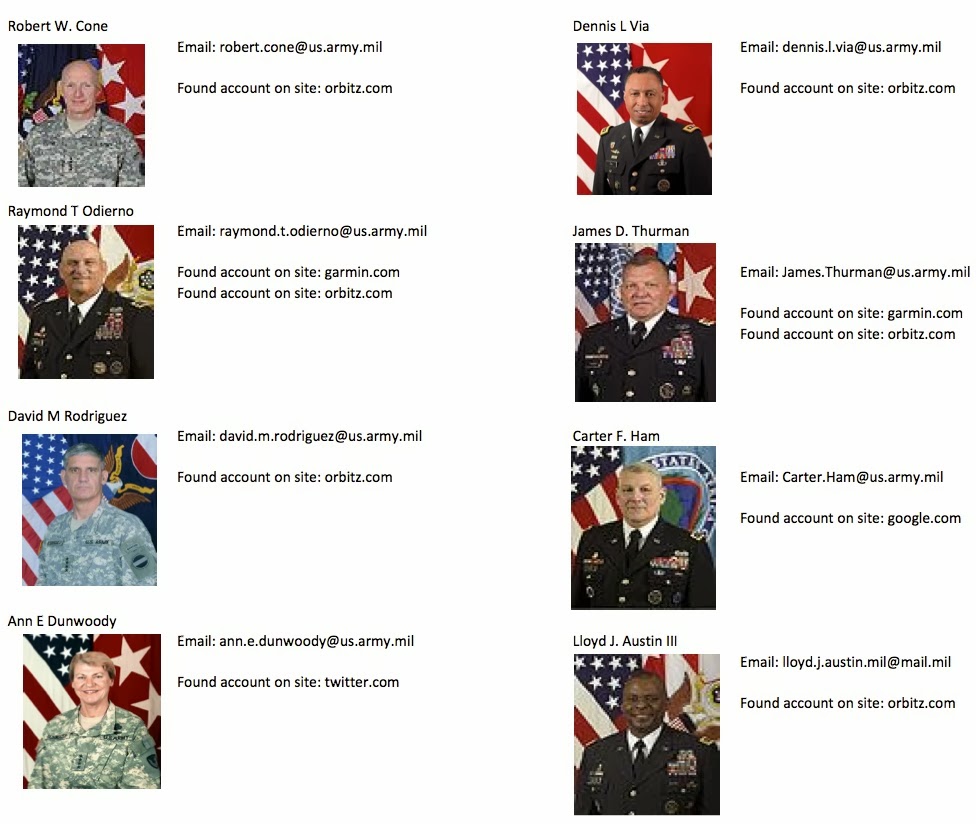
Practical and cheap cyberwar (cyber-warfare): Part II
Explore the world of cyber warfare and discover techniques for gathering information on human targets, including military personne
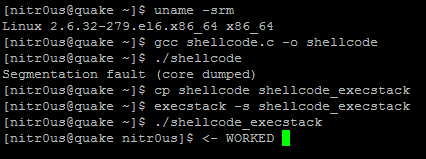
A Short Tale About executable_stack in elf_read_implies_exec() in the Linux Kernel
Explore the Linux Kernel vulnerability analysis focusing on code execution and logic bugs in data memory segments.
heapLib 2.0
Explore heapLib2: a JavaScript library for predictable memory allocations in Internet Explorer. Learn how to use it effectively.
Change of guard at Infineon
Explore the latest from Infineon with the SLE78/97. Discover how new designs focus on secure core technology.
Practical and cheap cyberwar (cyber-warfare): Part I
Explore the critical issues surrounding cyber warfare. Discover real life attacks and their impacts on infrastructure and security
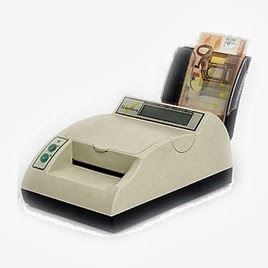
Hacking a counterfeit money detector for fun and non-profit
Explore the process of hacking a counterfeit money detector and understand the security measures in place for currency.
NCSAM - Lucas Apa explains the effects of games cheating, 3D modeling, and psychedelic trance music on IT security
Learn how to become a pen tester and explore the fascinating world of cybersecurity and ethical hacking techniques.
NCSAM – Eireann Leverett on why magic is crucial
Explore the journey of Eireann Leverett, a senior researcher at IOActive, and discover how magic influenced his career in security
NCSAM – an Interview with Cesar Cerrudo
Explore the journey of Cesar Cerrudo in IT security and his insights into the importance of persistence in cybersecurity.
Strike Two for the Emergency Alerting System and Vendor Openness
Explore the Monroe Electronics vulnerability and its impact on security reporting. Discover the latest updates on DASDEC systems.
A trip down cyber memory lane, or from C64 to #FF0000 teaming
Join us for National Cyber Security Awareness Month as we share insights and experiences from nearly 20 years in info sec.
IOActive supports National Cyber Security Awareness Month
October marks National Cyber Security Awareness Month, a vital initiative to promote online security for all users.
Seeing red - recap of SecurityZone, DerbyCon, and red teaming goodness
Explore my experiences at SecurityZone and DerbyCon, two impactful conferences in the security scene of Latin America.
Vulnerability bureaucracy: Unchanged after 12 years
Explore the common cybersecurity vulnerabilities faced by vendors and discover the challenges in reporting them effectively.
Emulating binaries to discover vulnerabilities in industrial devices
Learn how to discover vulnerabilities in industrial devices by emulating them for better security assessments.
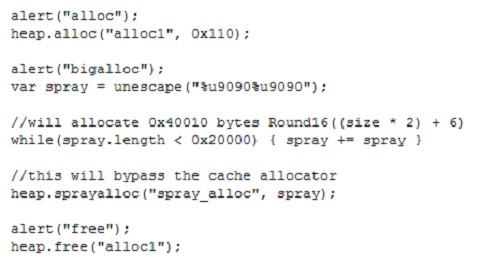
IE heaps at Nordic Security Conference
Join me at the Nordic Security Conference to explore heap memory allocations in JavaScript strings during my presentation.
FDA Medical Device Guidance
Explore the FDA Medical Device Cybersecurity Guidance and its impact on wireless technology in medical devices.
Car Hacking: The Content
Unlock the potential of car hacking using our refined tools and resources to drive automotive security forward.
Las Vegas 2013
Join the excitement of Black Hat USA & DefCon this year. Learn about hacking from experts and attend crucial presentations.
DefCon 21 Preview
Explore our upcoming presentation at DefCon on hacking automotive networks and control units. Get ready for insights!
2013 ISS Conference, Prague
Explore my insights from the 2013 ISS Conference in Prague, where government officials and companies connect and share ideas.
Why Vendor Openness Still Matters
Explore vendor cybersecurity challenges and discover solutions to protect against vulnerabilities in modern technology systems.
Why sanitize excessed equipment
Explore the benefits of buying used equipment for research. Discover how surplus resellers can save you money on PLCs.
FDA Safety Communication for Medical Devices
Discover the implications of the FDA Safety Communication for medical devices and how to safeguard against cyber threats.
Red Team Testing: Debunking Myths and Setting Expectations
Explore Red Team Testing cybersecurity and discover how it helps organizations identify vulnerabilities and strengthen defenses.
Tools of the Trade – Incident Response, Part 1: Log Analysis
Understand the importance of cybersecurity incident response in protecting your organization from cyber threats.
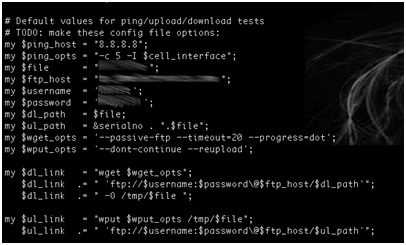
Industrial Device Firmware Can Reveal FTP Treasures!
Explore the risks of industrial device firmware vulnerabilities, focusing on remote access issues that can jeopardize security.

Identify Backdoors in Firmware By Using Automatic String Analysis
Learn how backdoors in firmware compromise safety in industrial control systems and the implications for manufacturers.
Bypassing Geo-locked BYOD Applications
Explore bypassing geo-locked applications to enhance access to important business tools. Learn more about secure solutions.
Fact or Fiction: Is Huawei a Risk to Critical Infrastructure?
Explore whether Huawei is a risk to infrastructure and national security. Understand the global concerns surrounding this issue.
InfoSec Europe 2013 - Security on Tap
Get ready for InfoSec Europe, the largest security conference in Europe, featuring over 350 exhibitors at Earls Court.
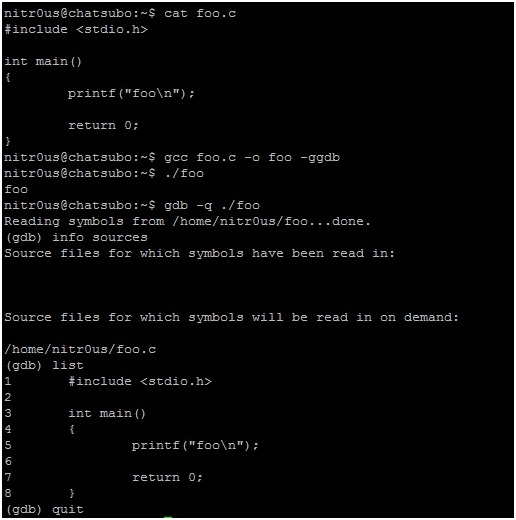
Can GDB's List Source Code Be Used for Evil Purposes?
Learn about the GNU Debugger and how it identifies source files to enhance your debugging skills effectively.
What Would MacGyver Do?
Discover the inventive spirit of MacGyver and his incredible solutions using everyday materials. Unleash your creativity!
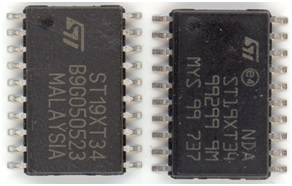
Spotting Fake Chips in the Supply Chain
Explore the risks of fake chips in supply chain management and their impact on business integrity and security.
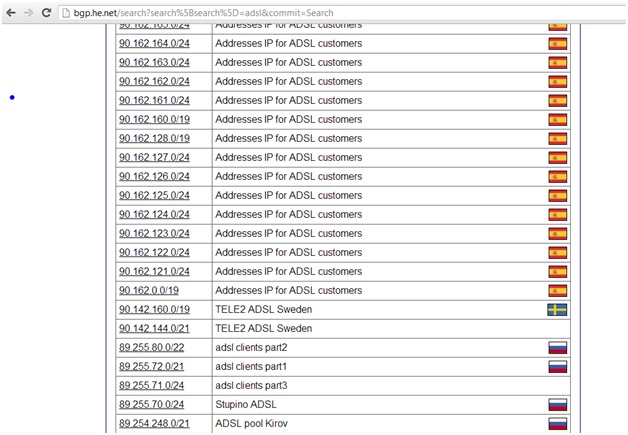
Behind ADSL Lines: How to Bankrupt ISPs While Making Money
Explore how to bankrupt ISPs through simple methods and potential solutions to enhance Internet security in your home.
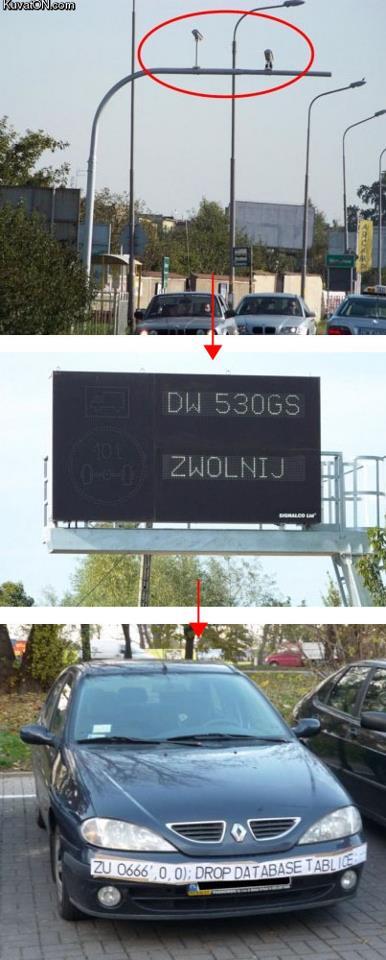
SQL Injection in the Wild
Explore SQL Injection vulnerabilities, the leading threat in Web applications. Understand how they can compromise security.
Credit Bureau Data Breaches
Explore the Credit Bureau Data Breach that exposed personal information. Learn how hackers accessed sensitive credit reports.
"Broken Hearts": How plausible was the Homeland pacemaker hack?
Explore how plausible he Homeland pacemaker hack was and its implications on modern technology and security.
IOAsis at RSA 2013
Uncover the exciting developments at IOAsis during RSA, including a refreshing oasis for VIPs, enhancing your conference experienc
Do as I say, not as I do. RSA, Bit9 and others...
Learn the important lessons from RSA and Bit9 failures. Vendor accountability is key to protecting your assets effectively.
Your network may not be what it SIEMs
Understand the importance of network cybersecurity in protecting sensitive information from cyber attacks.
Hackers Unmasked: Detecting, Analyzing, And Taking Action Against Current Threats
Hackers Unmasked reveals the realities of hacking. Learn essential insights to defend against cyber threats.
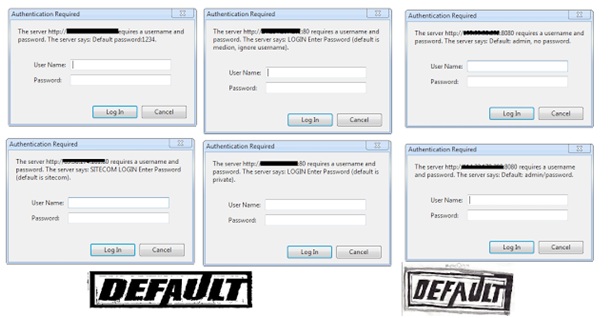
The Anatomy of Unsecure Configuration: Reality Bites
Explore the implications of unsecure configuration and how it can compromise network security in your organization.
2012 Vulnerability Disclosure Retrospective
Learn about vulnerability disclosures and the significant increase in public reporting that has changed patching dynamics.
Energy Security: Less Say, More Do
Explore the challenges in energy sector cybersecurity and why current spending may be misdirected for better safety.
S4x13 Conference
Explore the highlights of the S4x13 Conference, focusing on advanced topics in industrial control systems security.
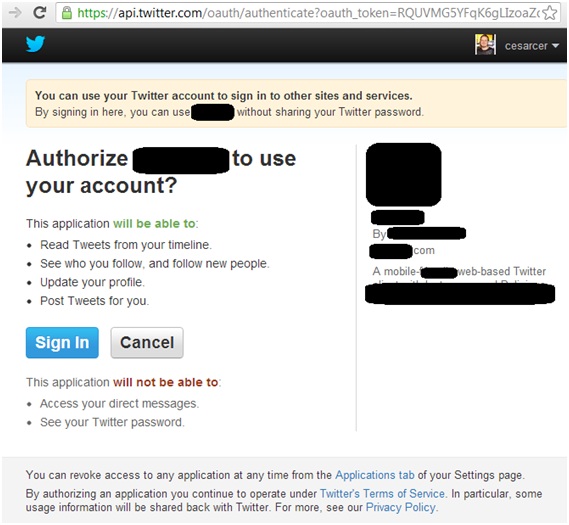
You cannot trust social media to keep your private data safe: Story of a Twitter vulnerability
Explore the challenges of social media cybersecurity and learn how to protect your online presence effectively.
When a Choice is a Fingerprint
Explore Kaspersky labs' analysis of 'Red October' and discover the challenges of attribution in cyber operations.
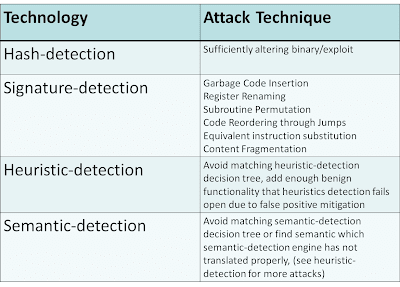
Offensive Defense
Explore offensive cybersecurity practices and how a smart layered defense can protect your network from threats.
The Demise of Desktop Antivirus
Explore the decline of desktop antivirus software and its place in the evolving landscape of cybersecurity and digital protection.
Exploits, Curdled Milk and Nukes (Oh my!)
Explore the worth of a zero-day vulnerability and discover what buyers are willing to pay for working exploits.
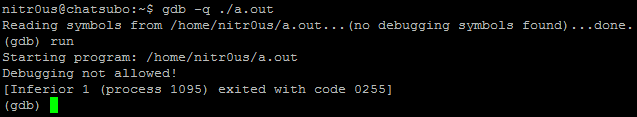
Striking Back GDB and IDA debuggers through malformed ELF executables
Explore the world of ELF executables and their role in the battle against malware and anti-reversing techniques.
IOActive Acquires Flylogic
IOActive acquires Flylogic, enhancing security services with Christopher Tarnovsky as Vice President and expanding hardware capabi
The Future of Automated Malware Generation
Explore the future of automated malware generation through recent presentations and key insights from global conferences.
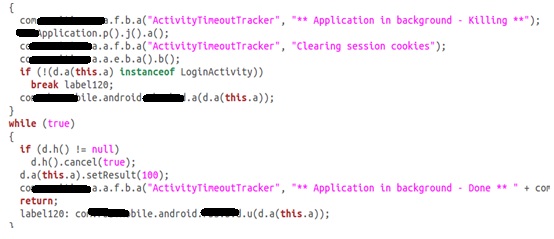
Hacking an Android Banking Application
Explore how to hack banking applications with expert insights on installation and analysis of mobile banking security.
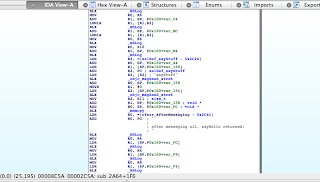
iOS Security: Objective-C and nil Pointers
Understand the essentials of iOS cybersecurity to protect your devices and applications from vulnerabilities and attacks.
3S Software’s CoDeSys: Insecure by Design
Explore the security implications of 3S Software’s CoDeSys vulnerabilities and their unique ladder logic execution methods.
The WECC / NERC Wash-up
Explore insights from WECC and NERC conferences in San Diego, focusing on industry best practices for grid security.
SexyDefense Gets Real
Explore SexyDefense and its impact on enhancing organizational protection in today's complex security landscape.
Impressions from Ekoparty
Explore the highlights of Ekoparty in Buenos Aires, where knowledge sharing and top researchers meet in an engaging environment.
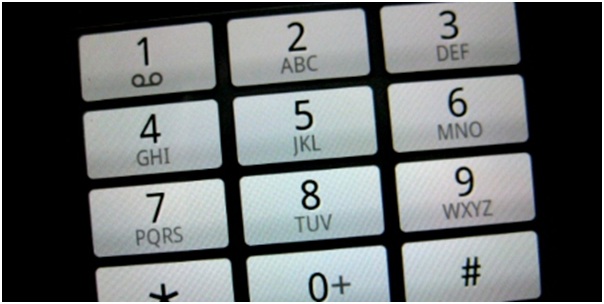
Completely Unnecessary Statistical Analysis: Phone Directory
Explore the statistical analysis of phone contacts and uncover how dialing methods can optimize your search efficiency.
Malware Doesn't Care About Your Disclosure Policy, But You Better Have One Anyway
Explore Disclosure Policy best practices to enhance ICS security by fostering better communication with researchers and authoritie
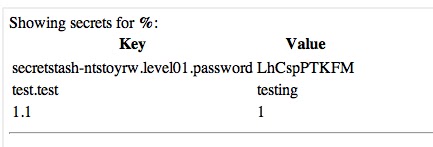
Stripe CTF 2.0 Write-Up
Explore the thrilling experience of Stripe CTF 2.0 through my detailed write-up on vulnerabilities and exploits.
One Mail to Rule Them All
Learn about email cybersecurity and how clever tactics can compromise your accounts. Stay informed and secure your data.
The Leaky Web: Owning Your Favorite CEOs
Learn about the tactics used in hacking emails and the vulnerabilities in common website authentication protocols.
Impressions from Black Hat, Defcon, BSidesLV and IOAsis
Reflect on the highlights of Black Hat and Defcon conferences, including meetings and connections made in Las Vegas.
IOActive Las Vegas 2012
Discover the excitement of Black Hat, Defcon, and IOAsis. Engage with leading researchers and experience top-tier talks and relaxa
The Value of Data
Understand the importance of data storage cybersecurity. Protect your valuable data from theft and uninformed access.
Thoughts on FIRST Conference 2012
Explore insights from the FIRST Conference, where global Computer Emergency Response Teams collaborate to enhance cybersecurity.
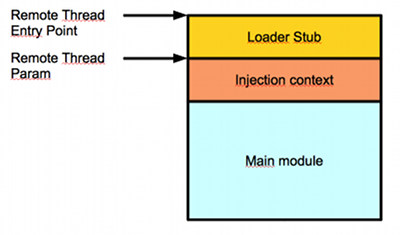
Inside Flame: You Say Shell32, I Say MSSECMGR
Uncover the findings of the CrySyS report on Flame, focusing on its unique code injection techniques and implications.
Old Tricks, New Targets
Learn about how Digitalbond spear phished in a recent attack involving malicious emails targeting industrial control systems.
Summercon 2012
Discover the history and evolution of Summercon through Chris Valasek’s insights as a current organizer of the event.
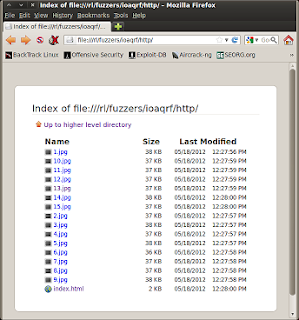
QR Fuzzing Fun
Explore QR fuzzing and its impact on QR code security. Learn how to protect information encoded in QR codes.
ST19XL18P - K5F0A Teardown
Explore the features of ST19XL18P and its advanced fabrication process with EAL4+ security for smart cards.
#HITB2012AMS: Security Bigwigs and Hacker Crème de la Crème Converge in Amsterdam Next Week
Get ready for #HITB2012AMS! Exciting trainings, speakers, and contests await at HITBSecConf2012 in Amsterdam.
Enter the Dragon(Book), Pt 2
Explore the mysterious C specification backdoor that remains undiscovered. Understand its implications and behavior in compilers.
Thoughts on AppSecDC 2012
Explore the highlights of AppSecDC, where web security meets Industrial Control Systems security in Washington, D.C.
TLS Renegotiation and Load Balancers
Understand the TLS renegotiation flaw and its impact on SSLv3. Learn how to address its implications in your security scans.
Hackito Ergo Sum: Not Just Another Conference
Meet Jonathan Brossard, the CEO of Toucan System, and discover insights into the world of hacking and conferences.
Atmel AT90SC3232CS Smartcard Destruction
Explore the Atmel AT90SC3232CS Smartcard. Discover its new design and active shielding features compared to other variants.
3 Metal 350nm teardown explanation
Learn about the NEC upd78F9210 MCU and how it can enhance your microcontroller applications.
Enter the Dragon(Book), Part 1
Explore STL memory allocators and their security risks, including challenges with integer overflow checks and compiler crashes.
IOActive's IOAsis at RSA 2012
Explore IOAsis and discover how it can enhance your digital experience with its unique features and functionalities.
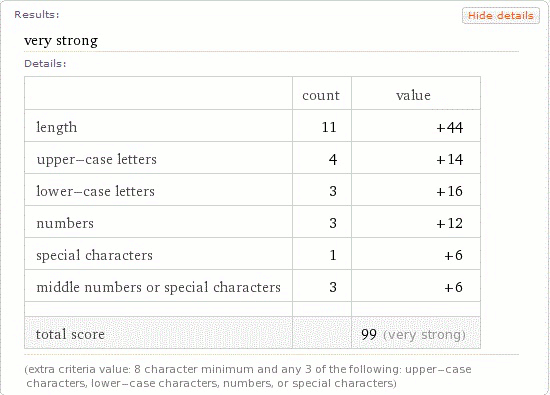
Estimating Password and Token Entropy (Randomness) in Web Applications
Explore the concept of entropy and its role in hacking passwords. Learn how to assess password strength and security.
I can still see your actions on Google Maps over SSL
Explore the Google Maps vulnerability and its implications for security in SSL traffic analysis. Stay informed and protected.
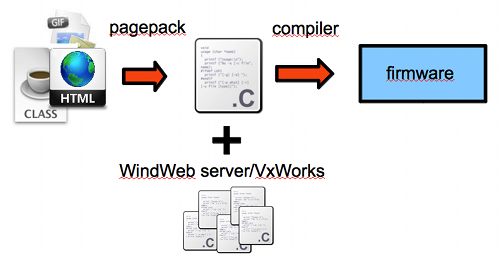
Solving a Little Mystery
Explore WindRiver's Web Server architecture and its role in the firmware analysis of embedded devices using VxWorks.
A free Windows Vulnerability for the NSA
Explore the Microsoft Windows vulnerability related to installer files that elevate privileges unexpectedly during execution.
Common Coding Mistakes - Wide Character Arrays
Avoid common coding mistakes involving wide character arrays. Learn tips to prevent errors in your code reviews.
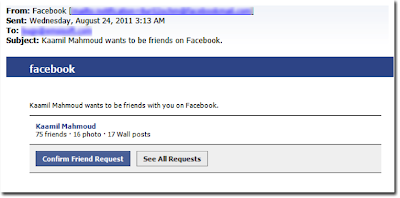
Automating Social Engineering: Part Three
Learn how social engineering automation can simplify the crafting of ruses, making attacks more effective and trustworthy.
Automating Social Engineering: Part Two
Explore how social engineerings automation can enhance security measures and streamline procedures for organizations.
Automating Social Engineering: Part One
Uncover the significance of social engineering automation in protecting organizations from security threats.
Easy and Quick Vulnerability Hunting in Windows
Learn how to find vulnerabilities in Microsoft Windows effectively and enhance your system's security with practical tips.
Windows Vulnerability Paradox
Explore the Microsoft Windows vulnerability discussed at Black Hat USA 2011, highlighting low-impact but interesting security conc
Blackhat TPM Talk Follow-up
Explore the challenges in analyzing the SLE66PE smartcard family. Discover insights from Blackhat DC 2009 presentations.
Atmel ATMEGA2560 Analysis (Blackhat follow-up)
Dive into the Atmel ATMEGA2560 analysis from Blackhat USA, exploring security flaws and design oversights in the device.
Parallax Propeller P8X32A Quick Teardown
Learn how the Parallax Propeller P8X32A can enhance your development projects with its unique capabilities.
Echostar v NDS appellate court ruling update
Explore the recent ruling in the Echostar v NDS lawsuit, which highlights the significant implications for both companies.
Infineon / ST Mesh Comparison
Explore the Infineon and ST Mesh comparison. Discover design differences and share your thoughts on their architectures.
We are now on Twitter too!
Join us on IOActive Twitter for updates and insights. Follow us for the latest news and information about our activities.
Blackhat USA 2009 Poll - Rev Eng Class
Explore the intriguing world of Black Hat USA and discover its significance in the cybersecurity landscape.
Intel 4004
Explore the Intel 4004, the first widely-used microprocessor and its unique design characteristics compared to modern chips.
New Author: Herr Karsten Nohl!
We are excited to welcome Herr Karsten Nohl to our blog, a notable figure in the Crypto-1 algorithm and CCC.
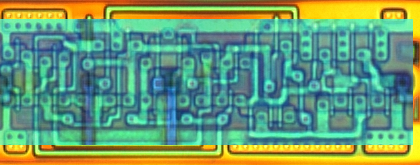
Reverse-Engineering Custom Logic (Part 1)
Explore the fundamentals of Reverse Engineering microchips and learn to identify logic functions in transistors and ASICs.
Atmel AT91SAM7S Overview
Explore the Atmel AT91SAM7S, a powerful ARM based device with a unique 210nm design and five metal layers in its layout.
Atmel CryptoMemory AT88SC153/1608 :: Security Alert
Learn about the Atmel CryptoMemory AT88SC153/1608 security alert regarding the discovered backdoor vulnerabilities.
AT90S8515 - Legacy!
Explore the Atmel AT90S8515 microcontroller, a popular choice with impressive specs like 8KB Flash and 512 Byte EEPROM.
ATMEGA88 Teardown
Explore the features of the ATMEGA88, an impressive 8k FLASH microcontroller with unique SRAM and metal layer design.
Security Mechanism of PIC16C558,620,621,622
Explore how Microchip PICs utilize the structure of AND-gates in their design for enhanced functionality and performance.
AND Gates in logic
Explore the mechanics of an AND gate and discover its role in logic circuits and microcontrollers in our latest blog post.
ST201: ST16601 Smartcard Teardown
Learn about the ST16601 Smartcard and its advanced Mesh technology for secure MCU access control and applications.
Infineon SLE4442
Explore the Infineon SLE4442, a 256 byte EEPROM with unique write protection and a Programmable Security Code for secure access.
The KEYLOK USB Dongle. Little. Green. And dead before it was born!
Explore our teardown of the KEYLOK USB Dongle. Discover its simple design and the ease of duplication of its circuit board.
Atmega169P (Quick Peek)
Explore the Atmega169P and its capabilities in AVR series, highlighting the benefits of picoPower technology.
In retrospect - A quick peek at the Intel 80286
Discover the impact of the Intel 80286 on technology in 1982. Relive the era of slow PCs and classic games.
Safenet iKey 1000 In-depth Look Inside
Explore the Safenet iKey 1000 with our detailed teardown. Discover the components and technology inside this USB token.
Unmarked Die Revisions :: Part II
Explore the risks and procedures involved in Wet-etching. Understand the dangers and requirements for safe practice.
Safenet iKey 2032 In-depth Look Inside
Explore the advantages of the Safenet iKey 2032, a portable two-factor authentication token for secure access.
Unmarked Die Revisions :: Part I
Explore die revisions on various Microchip's substrates and the significance of nomenclature changes in semiconductor design.
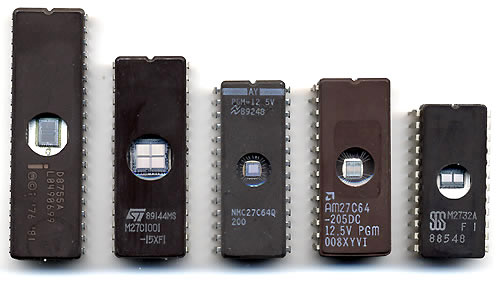
Decapsulated devices
Check out images of decapsulated parts still in their packages that we discussed at Toorcon9