

Test post, please delete: Five Eyes and the AI shift (fixed)
One-sentence summary shown in listings and as the meta description.
Offensive Security Best Practices for Modern Enterprises
Annual assessments are not enough. Learn how threat emulation, Red Team exercises, and continuous security validation help enterpr
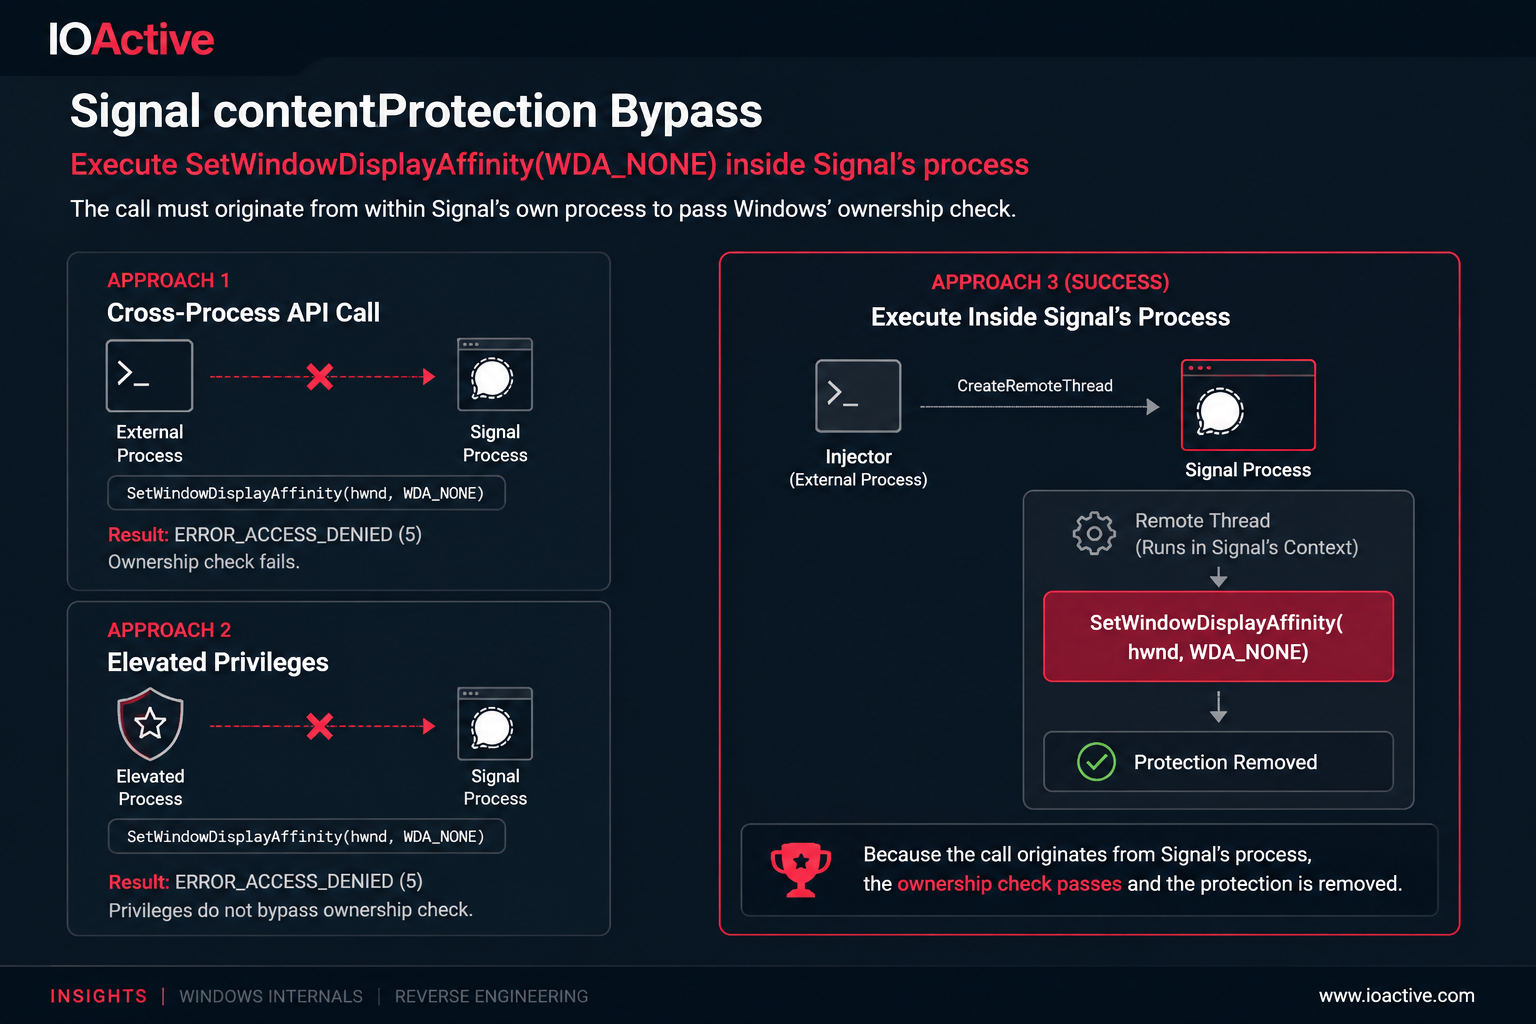
Signal Windows Desktop: contentProtection Bypass
Signal Desktop's Windows screen-capture protection can be bypassed via CreateRemoteThread code injection — even from an elevated p
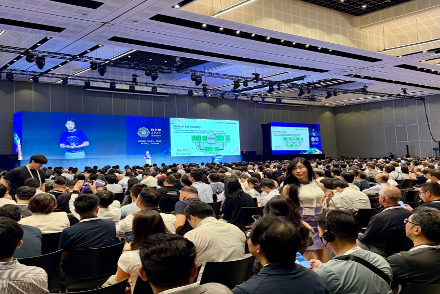
Key Takeaways from the 2026 OCP APAC Summit
IOActive attended the 2026 OCP APAC Summit in Taipei (Aug 11–12), covering AI infrastructure security, SONiC networking, and growi
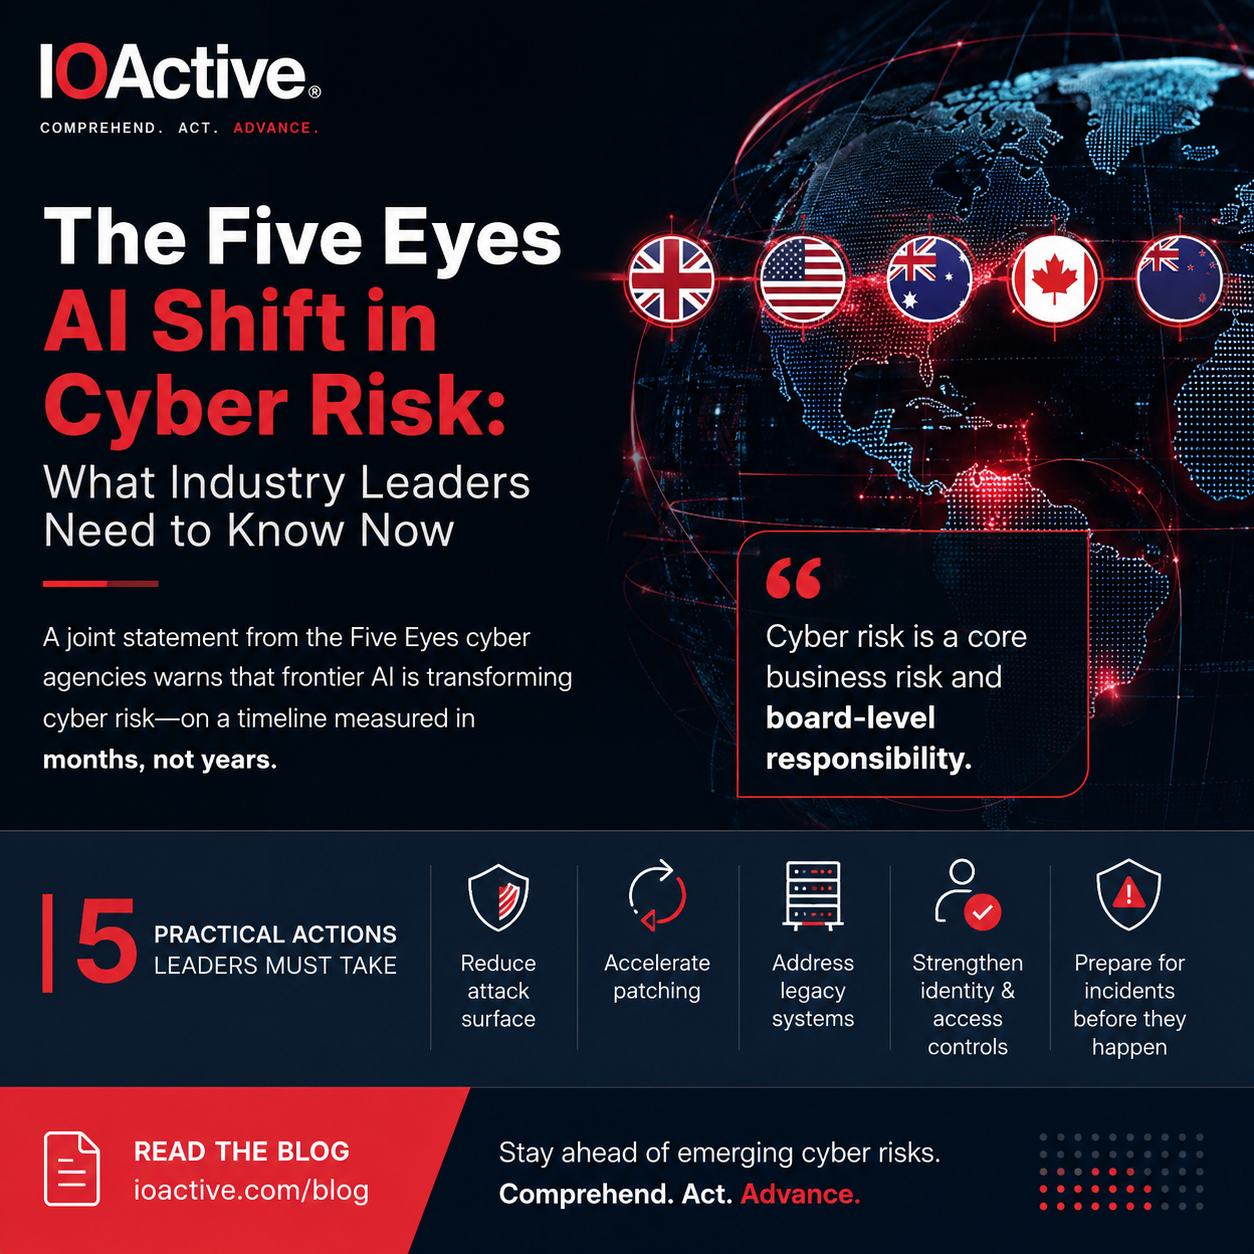
The Five Eyes AI Shift in Cyber Risk Statement: What Industry Leaders Need to Know Now
Five Eyes cyber agencies warn AI is cutting exploit timelines to months: 75% of UK CNI attacks are state-linked. Learn what boards
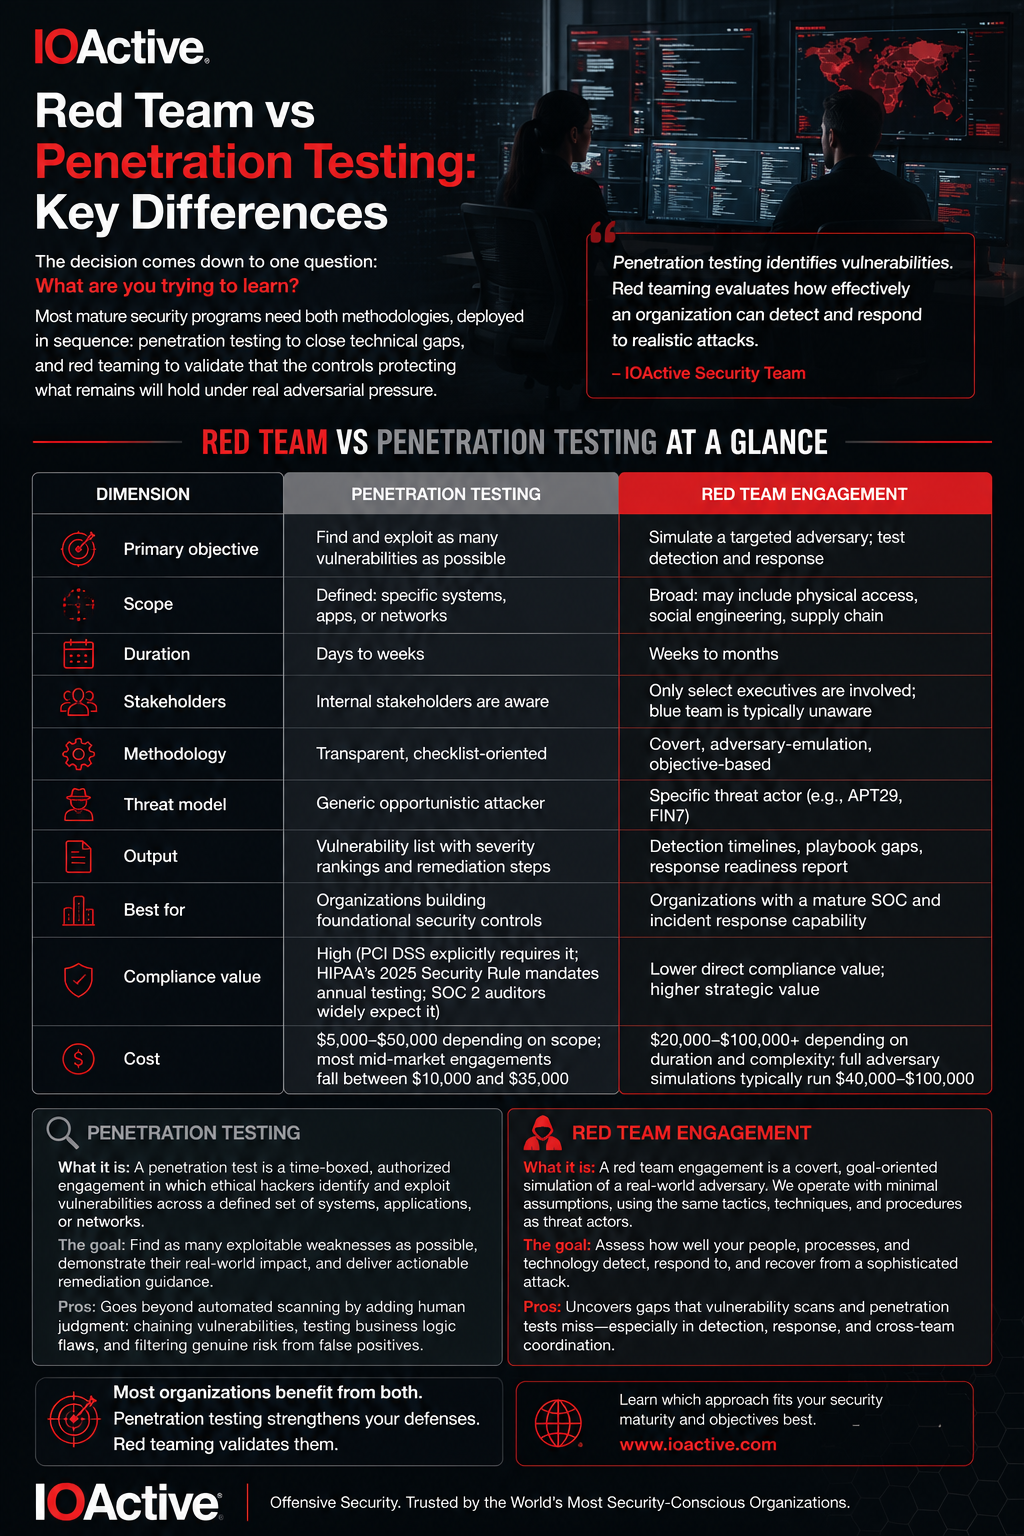
Red Team vs Penetration Testing: Key Differences
Penetration testing finds vulnerabilities. Red teaming tests whether your organization can prevent, detect, and respond to a real
When the Advisory Arrives First: Minnesota's Water Utilities and the Limits of Warning
What happened in the Minnesota water cyberattack? 30+ utilities lost automated OT controls in July 2026, days after CISA's AA26-09
Security Challenges in AI Adoption: 2026
AI adoption is moving fast. Security is not keeping up. Explore the top security challenges in AI adoption in 2026, with current s
Cyber Attack Trends 2026: What Security Teams Face
Cyber attack trends 2026: Which threats are real business risks and what can you do about them? IOActive breaks down ransomware, O
Iranian-Affiliated Actors Expand PLC Targeting to Siemens and Schneider Electric: What CISA’s Updated Advisory Means for CNI
Learn how CISA's updated AA26-097A advisory expands Iranian PLC attacks to Siemens and Schneider Electric—and what critical infras
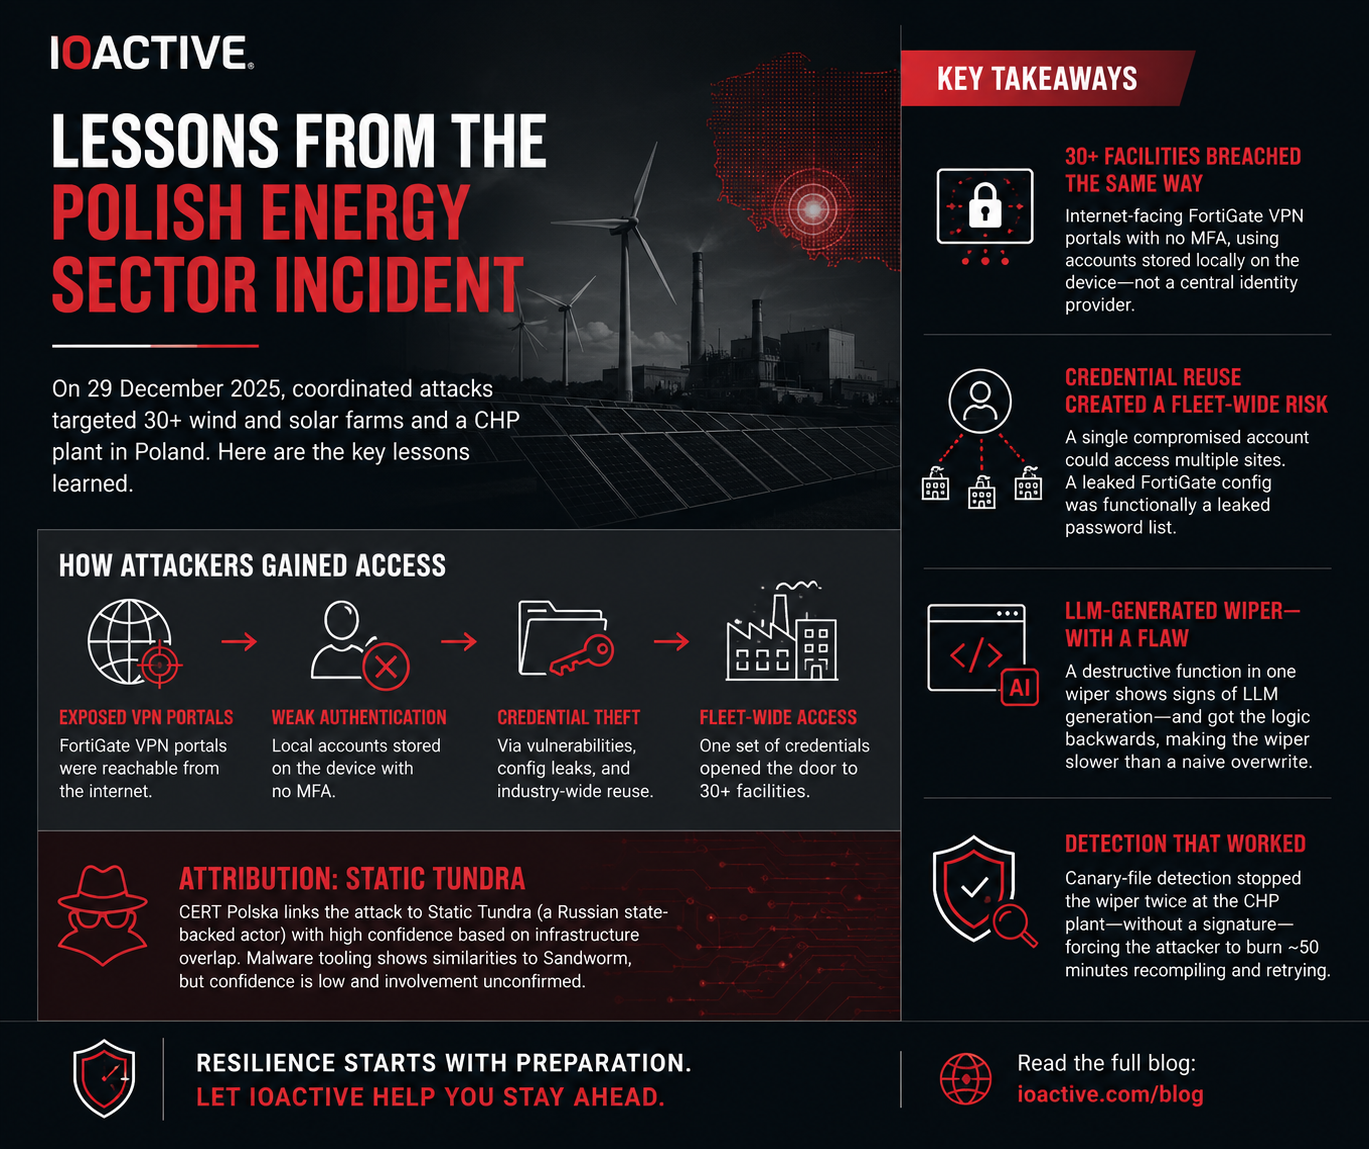
Lessons from the Polish Energy Sector Incident
How default FortiGate VPN credentials let one threat actor breach 30 Polish energy facilities in a single coordinated OT attack—an
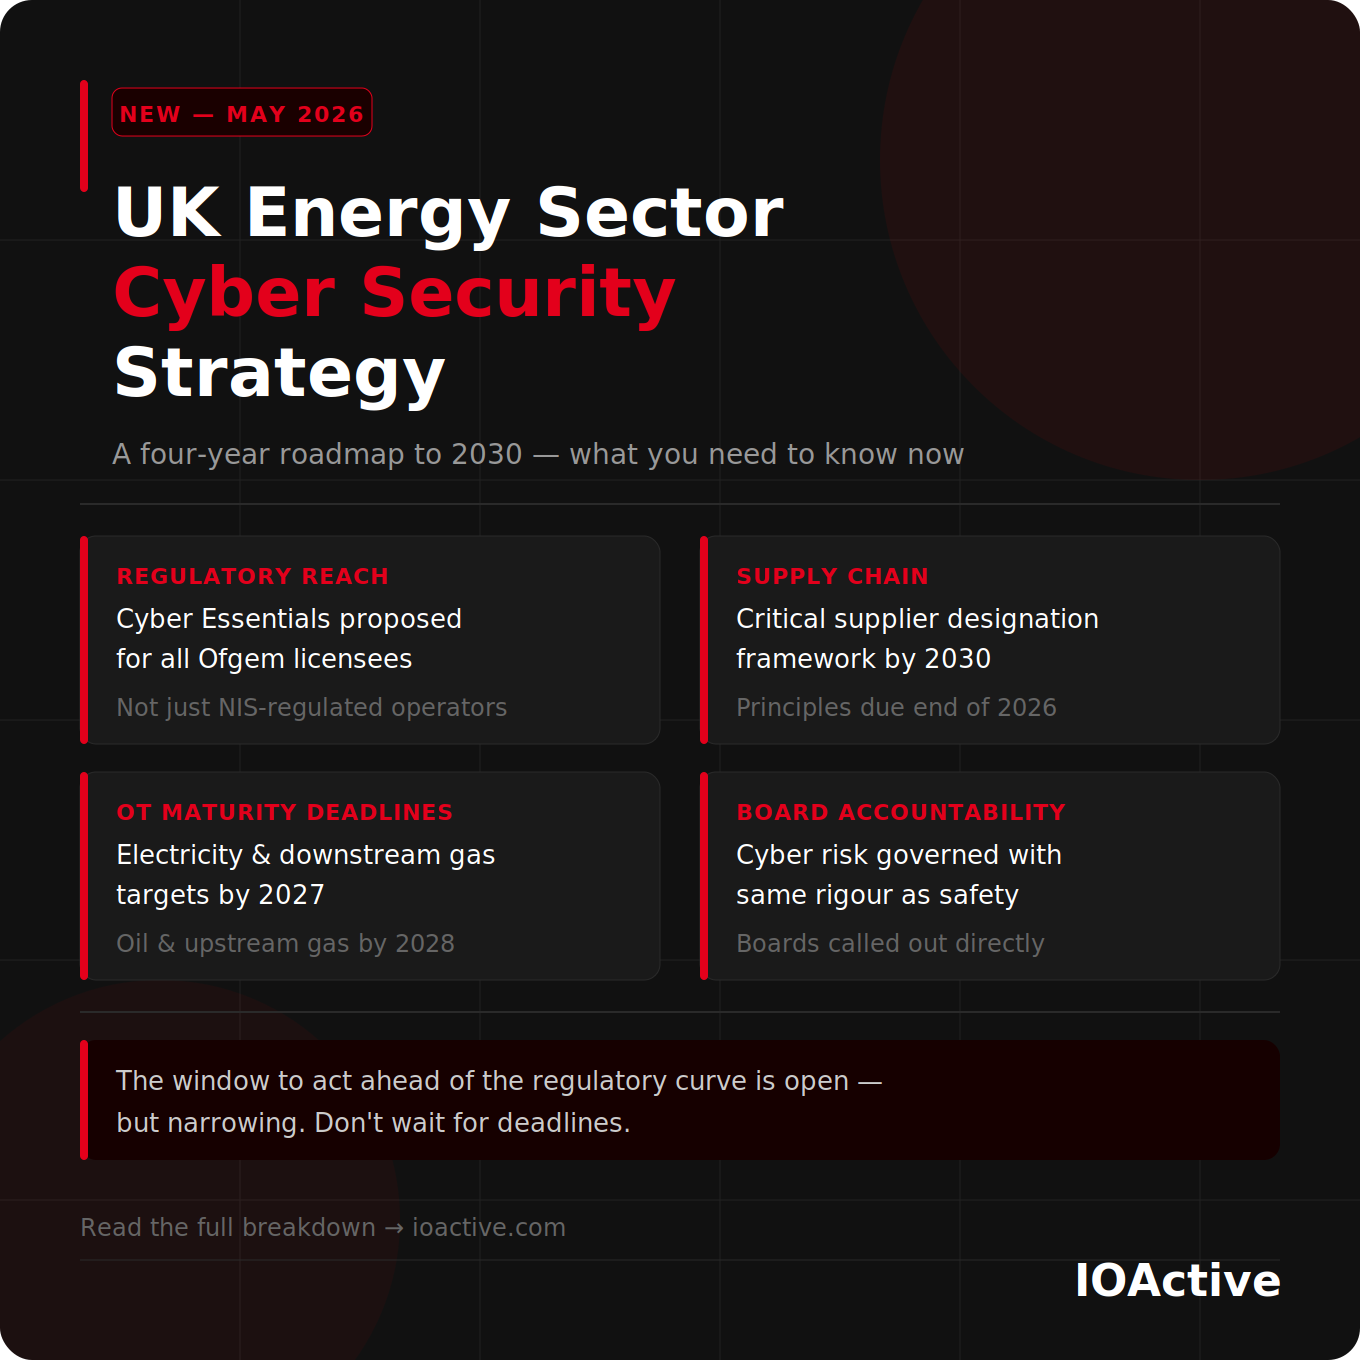
The UK Energy Sector Cyber Security Strategy: What Industry Leaders Need to Know Now
The UK Government published their Energy Sector Cyber Security Strategy on 28 May 2026, setting out a four-year roadmap to 2030. C
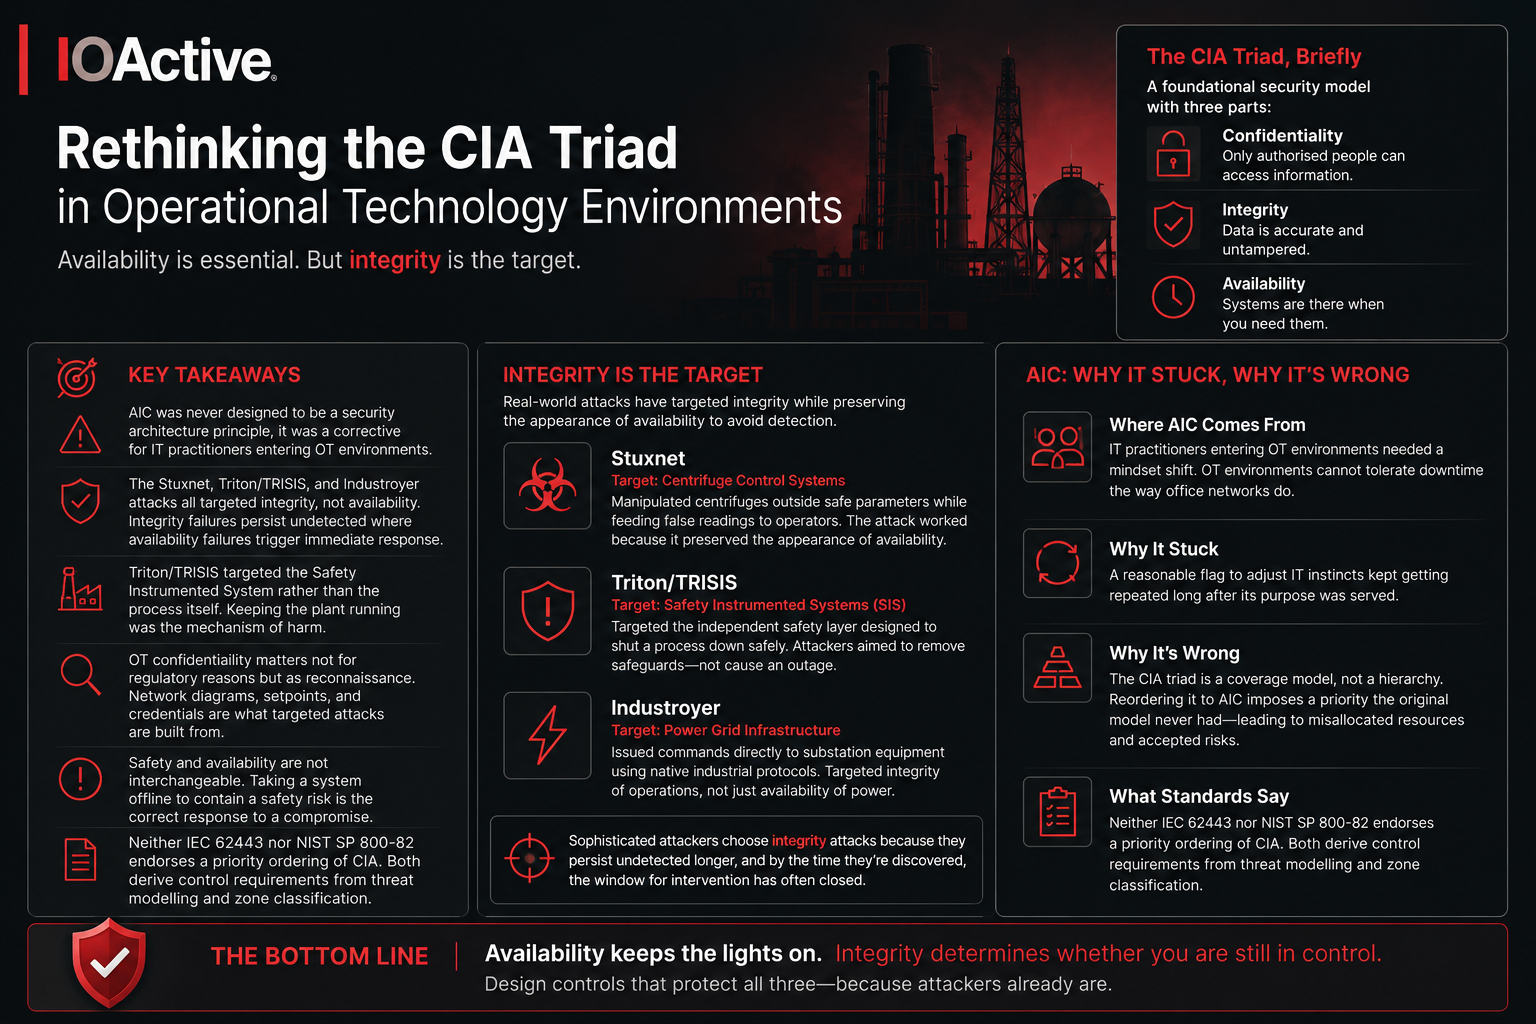
Rethinking the CIA Triad in Operational Technology Environments
Walk into most introductory OT security talks and you will hear the same piece of advice. Forget CIA, think AIC: Availability firs
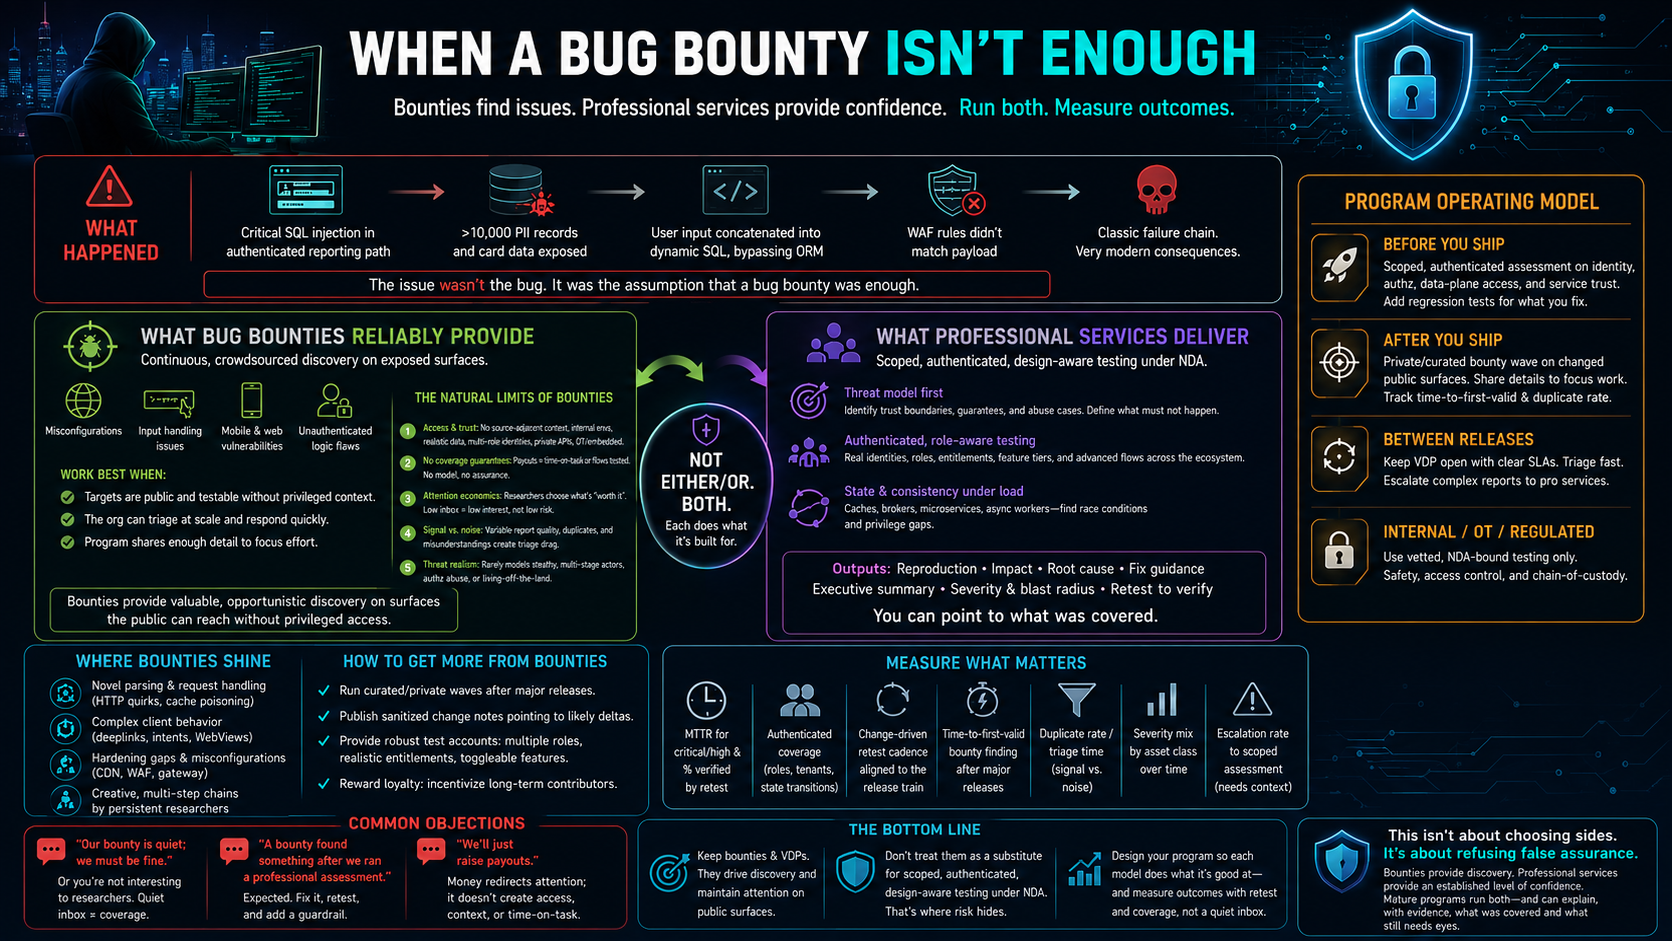
When a Bug Bounty Isn’t Enough
This post is about how bug bounties and professional services actually work, where each is strong, and why neither replaces the ot
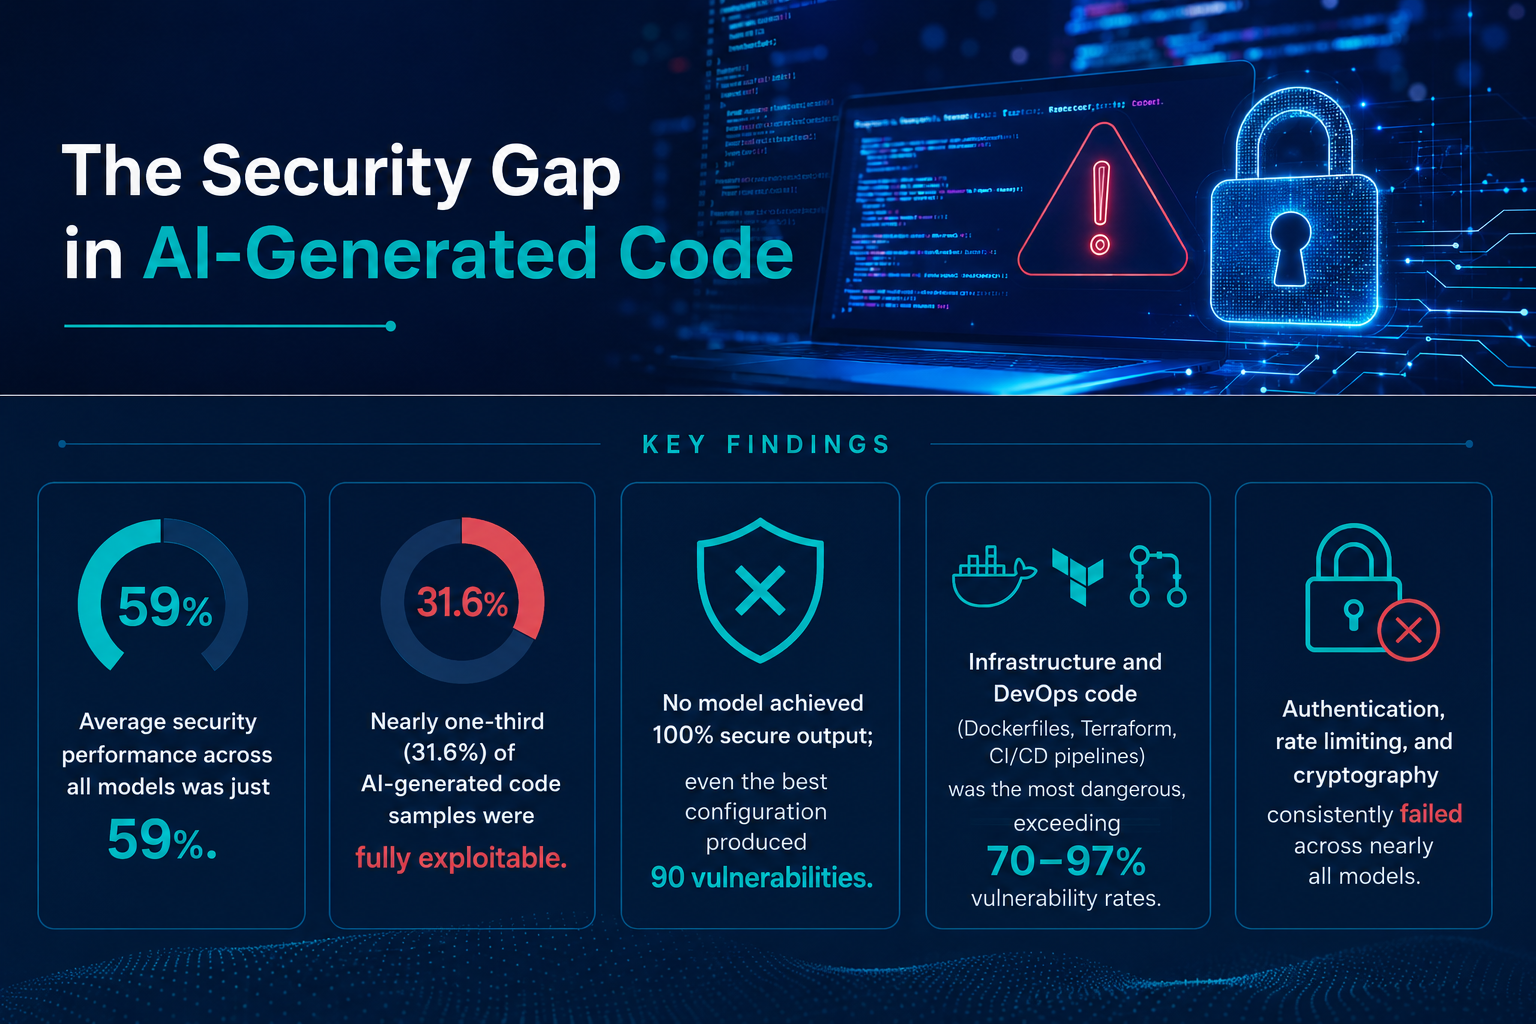
The Security Gap in AI-Generated Code
IOActive evaluated 27 leading AI models and AI-powered coding tools using 730 real-world programming prompts across 27 languages a
From Skynet to AI Agents: The State of Robot Security Nine Years Later
A new research paper IOActive contributed to, "Cybersecurity AI: Hacking Consumer Robots in the AI Era", published in March 2026 w
EU Cyber Resilience Act (EU CRA): What to Know and How IOActive Can Help
Cybersecurity regulation in the EU is shifting in a meaningful way. With the Cyber Resilience Act (CRA), the focus is moving upstr
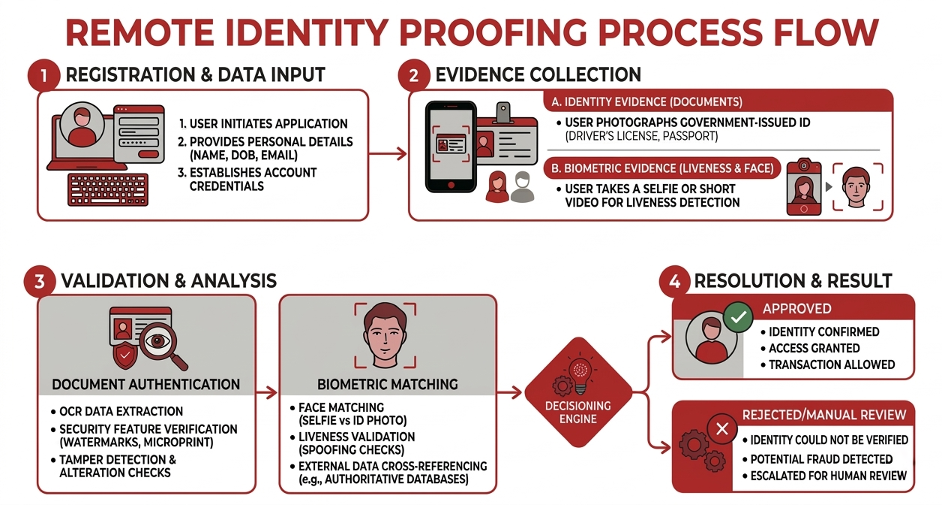
Virtual Assistant: Defeating Liveness Detection with the Help of Virtual Devices
In this article, we will explore how liveness detection, which is designed to distinguish real users from spoofed representations,
The Evolution of AI-Powered Security Consultants
Learn what's happening now with the capabilities of the large language models (LLMs) that fuel AI.
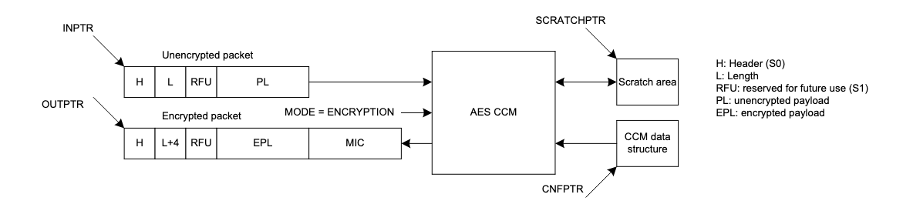
Reversing the RADIO – AES CCM Link in the nRF family
I’ve been working on a research project that includes radio frequency (RF) nodes with a proprietary protocol running on top of Nor
Authentication Downgrade Attacks: Deep Dive into MFA Bypass
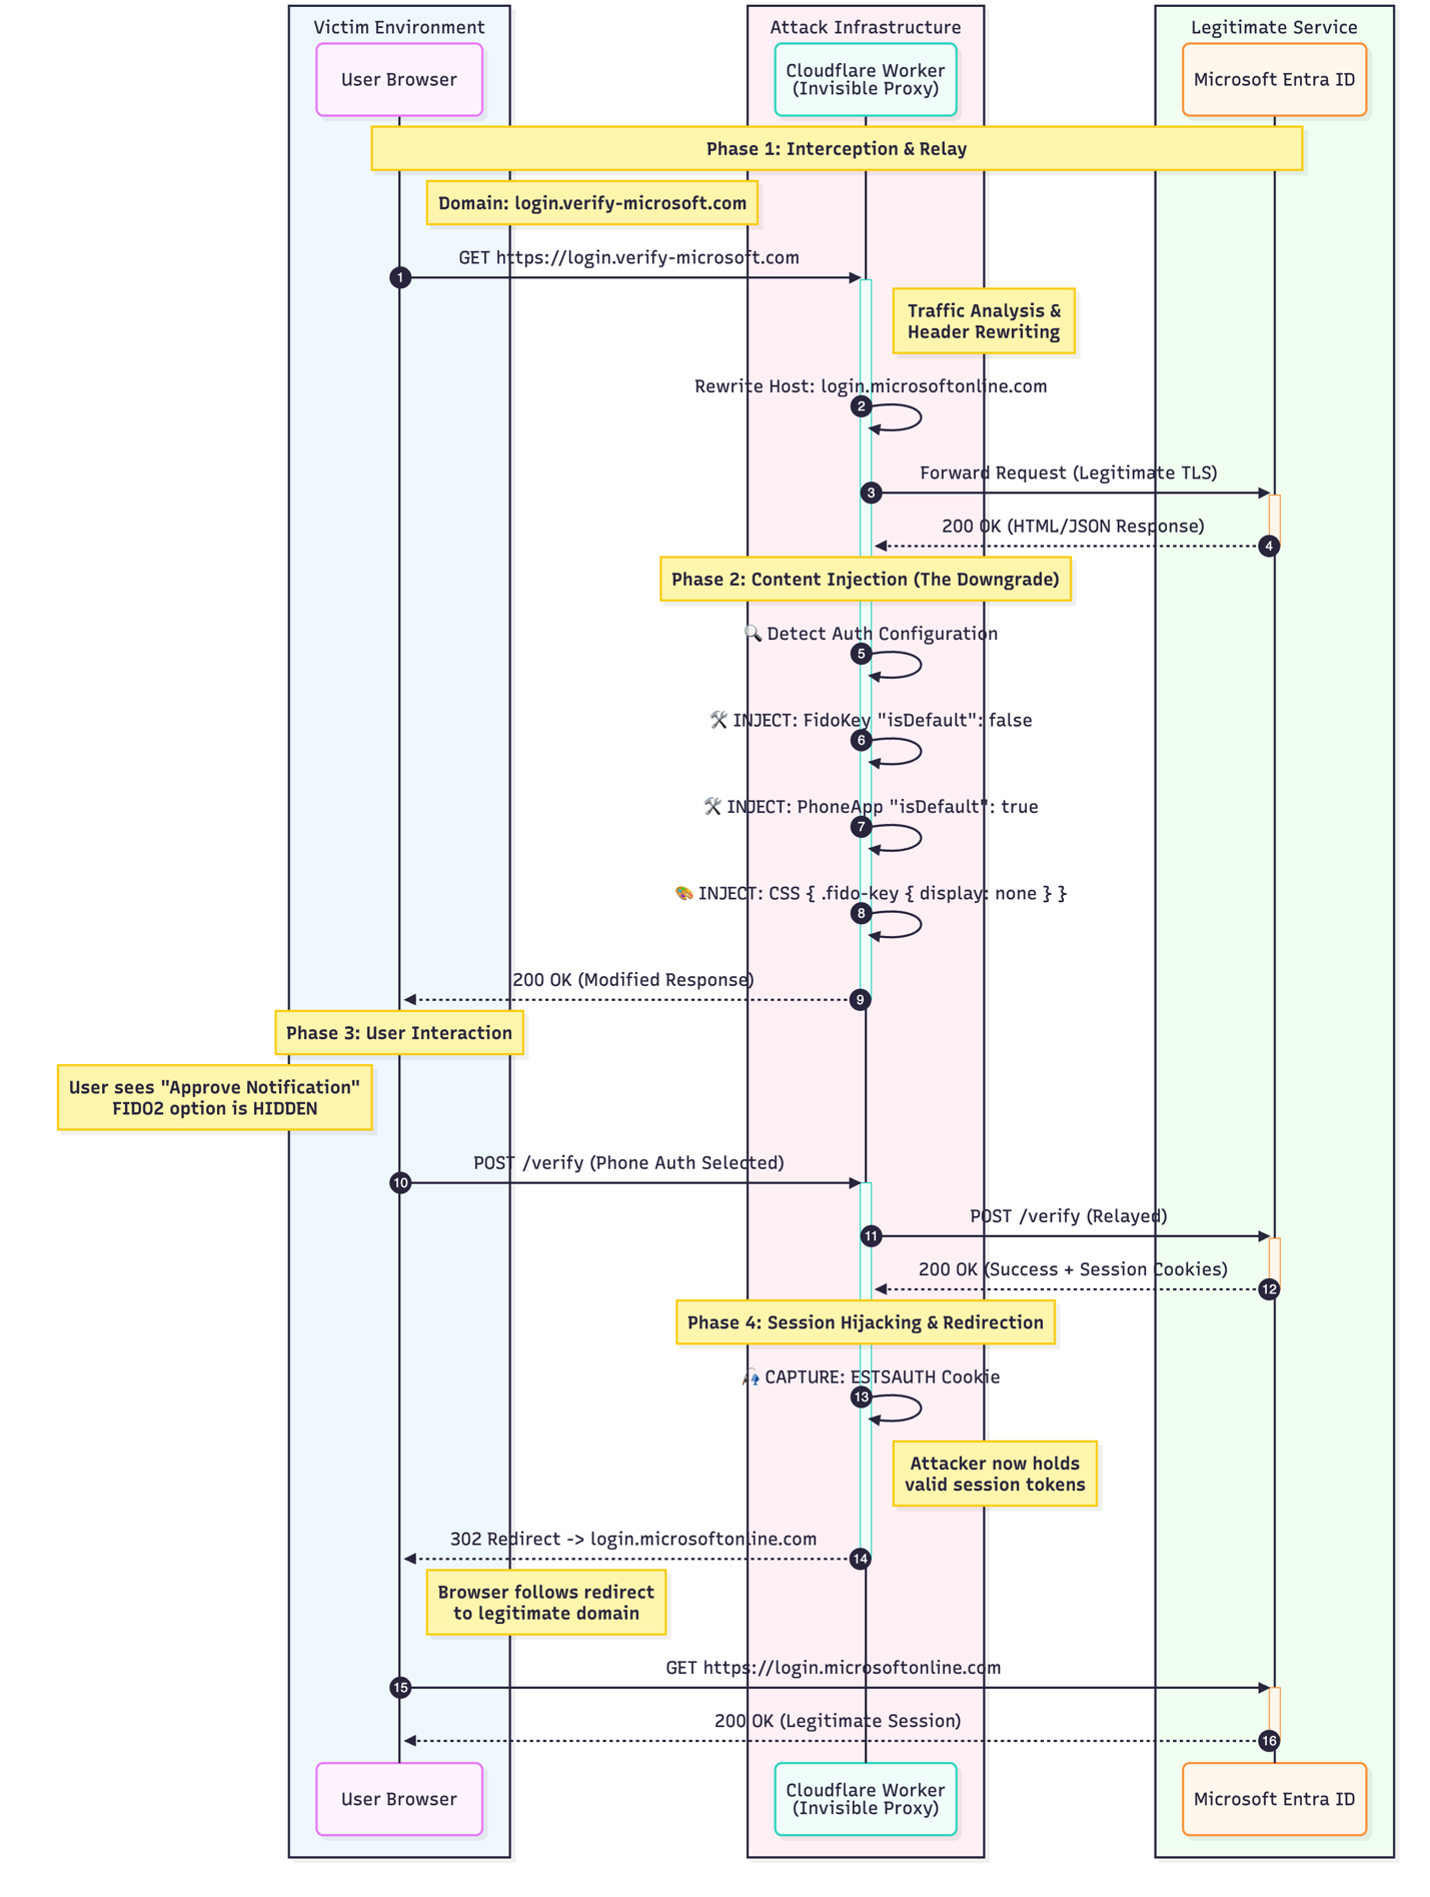
This research introduces two key contributions: first, the weaponization of Cloudflare Workers as a serverless transparent proxy p
IOActive Security Advisory | CIRCUTOR – SGE-PLC1000/SGE-PLC50 v 0.9.2 / ServicePack 140411
Husn Canaries: Defense-In-Depth for AI Coding Assistant Governance
AI-powered coding assistants such as OpenAI Codex, Claude Code, GitHub Copilot, and similar tools are increasingly embedded in eve
Code Review & Dynamic Fuzzing of Microsoft’s Signing Transparency
IOActive performed a thorough security assessment of Microsoft’s Signing Transparency (ST) service, focusing on code review, dynam
Semiconductor Industry Jargon
The semiconductor industry uses a large and complex set of jargon. This set of terms represents the significant intersection of sc
Deepfake Defense: From No-Cost Basics to Enterprise-Grade Controls
Deepfakes are a forcing function for better workflow. Start by removing voice-only approvals and requiring directory callbacks and
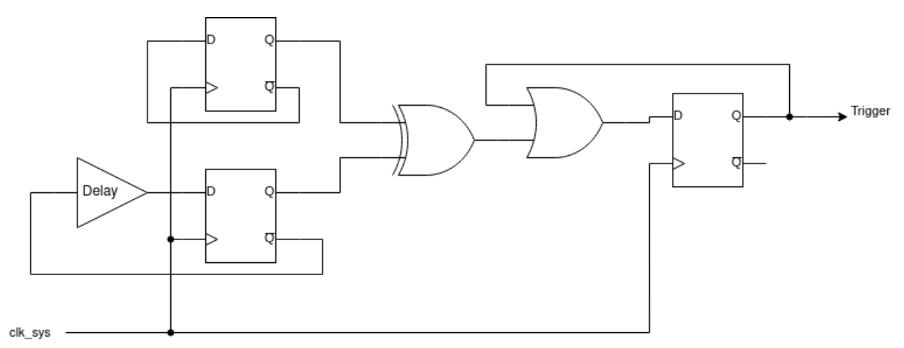
Characterizing the Raspberry Pico 2 FI countermeasures – Part 1
After more than 10 years in chip security evaluations, I can confidently say that the RP2350 might be one of the most secure gener
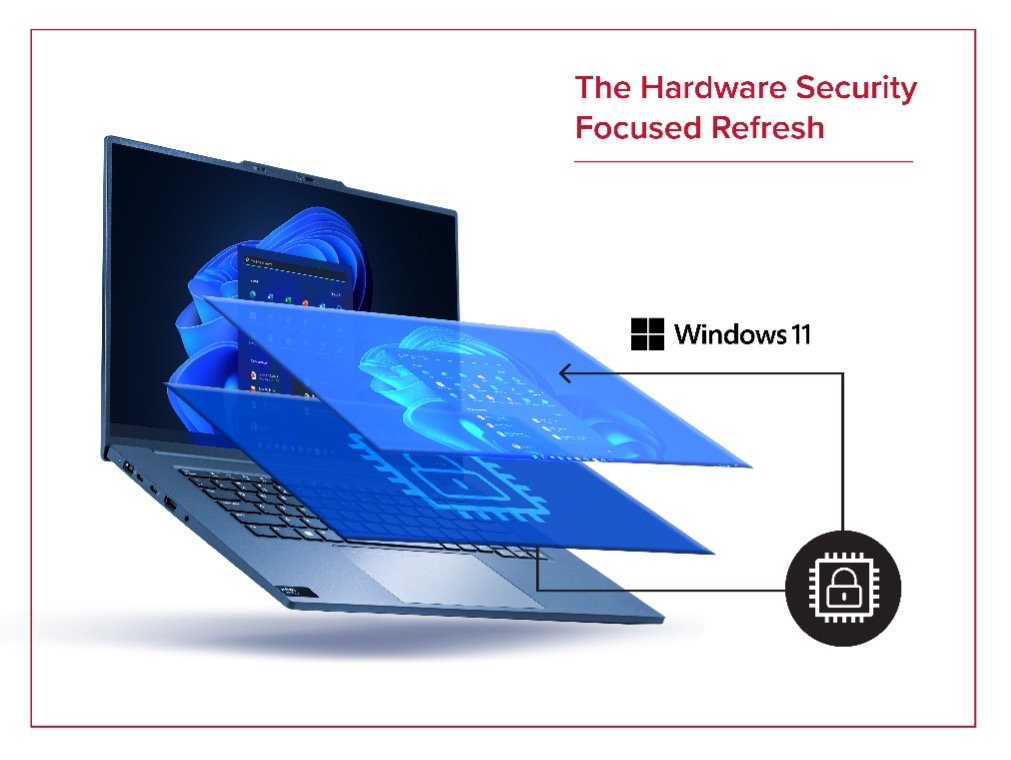
Windows 11 Upgrade - The Hardware Security Focused Refresh
Windows 10’s End of Life is slated for October 14th, 2025. After this date, it will no longer be supported, and businesses are exp
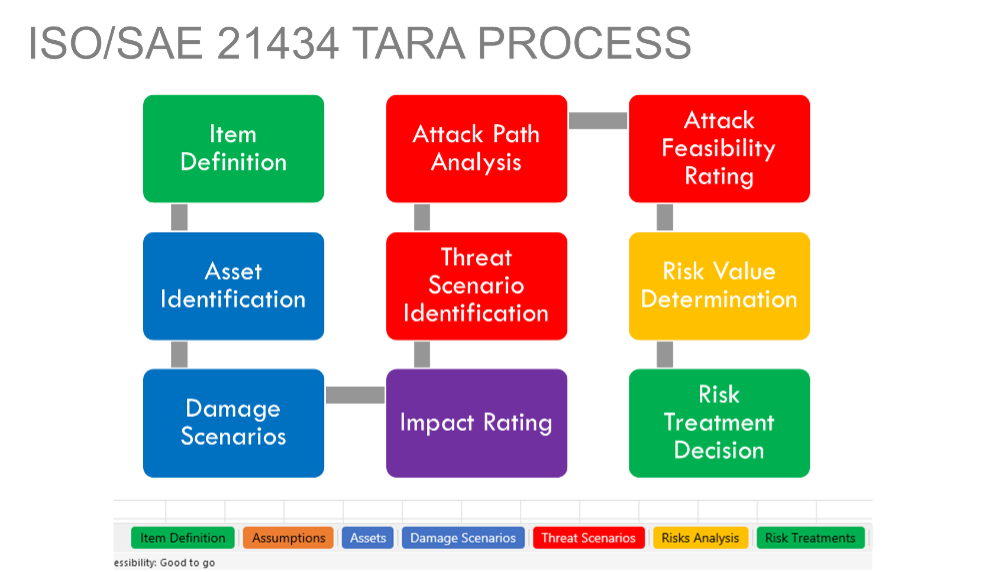
Accelerating Threat Assessment in Vehicle ECUs | A TARA Case Study
A global automaker required a thorough, but time-constrained, threat assessment and remediation plan for its critical Gateway Elec
Smarter Security, Leaner Budgets: IOActive & SERJON’s Approach to Cyber Optimization
In our experience working with companies of all sizes and types, one challenge keeps coming up: cybersecurity operations are becom