- Limited to iOS platform
- Black box approach
- All tests were only performed on the app (client side); my research excluded any server-side testing
- This research does not describe the vulnerabilities I found or how to exploit them in order to protect the owners of the apps and their customers
- Some of the affected banks were contacted, and the vulnerabilities reported
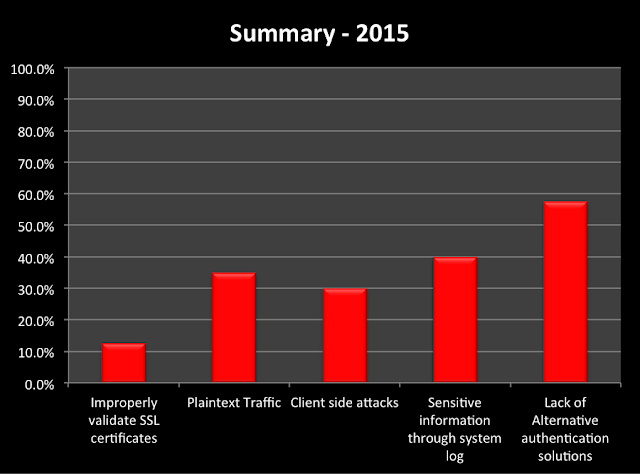
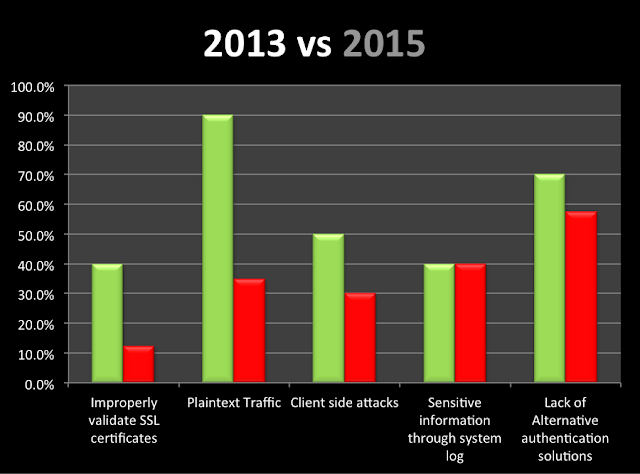
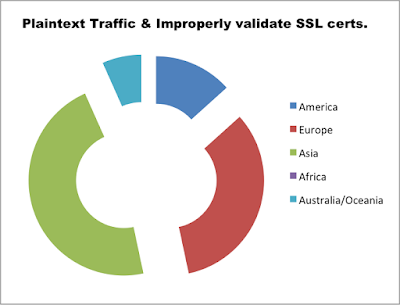
- Transport Security Plaintext traffic
- Improper session handling
- Properly validate SSL certificates
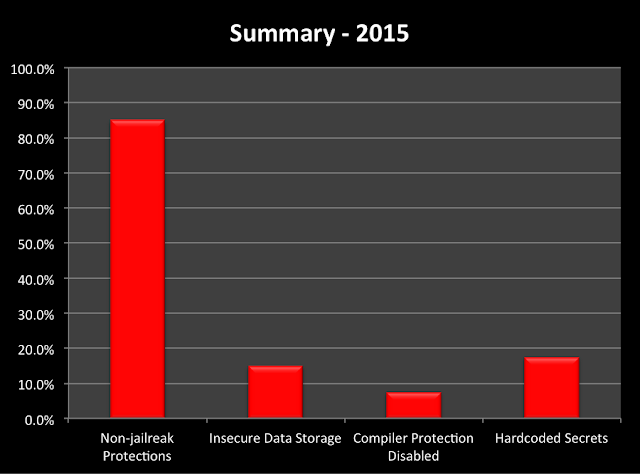
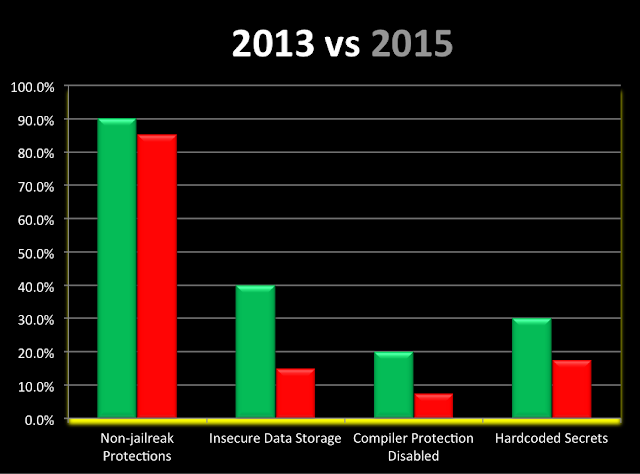
- Anti-jailbreak protection
- Compiled with PIE
- Compiled with stack cookies
- Automatic reference counting
- Data validation (input, output)
- UIWebView implementations
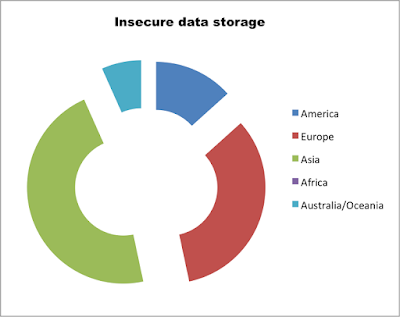
- SQLlite database
- File caching
- Property list files
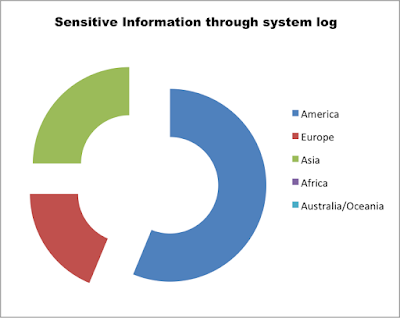
- Log files
- Custom logs
- NSLog statements
- Crash reports files
- Disassemble the application
- Detect obfuscation of the assembly code protections
- Detect anti-tampering protections
- Detect anti-debugging protections
- Protocol handlers
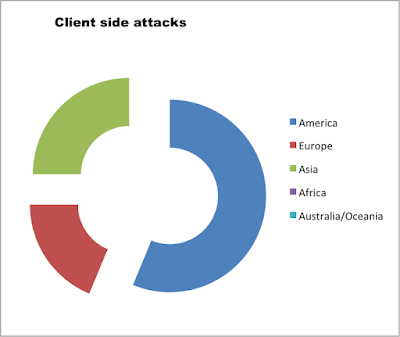
- Client-side injection
- Third-party libraries
- Network and Logging Analysis
- Binary and File System Analysis