

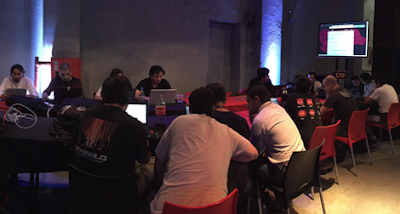
EKOPARTY Conference 2015, one of the most important conferences in Latin America, took place in Buenos Aires three months ago. IOActive and EKOPARTY hosted the main security competition of about 800 teams which ran for 32 hours, the EKOPARTY CTF (Capture the Flag).
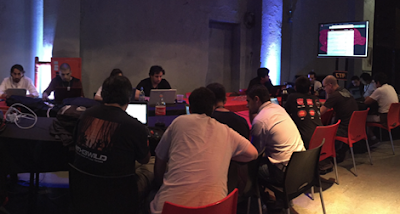
Teams from all around the globe demonstrated their skills in a variety of topics including web application security, reverse engineering, exploiting, and cryptography. It was a wonderful experience.
Competition, types, and resources
- Fun while learning.
- Legally prepared environments ready to be hacked; you are authorized to test the problems.
- Recognition and use of multiples paths to solve a problem.
- Understanding of specialized attacks which are not usually detectable or exploitable by common tools.
- Free participation, typically.
- Good recruiting tool for information security companies.
- CTFs (Capture the Flag) are restricted by time: Jeopardy: Problems are distributed in multiple categories which must be solved separately. The most common categories are programming, computer and network forensics, cryptography, reverse engineering, exploiting, web application security, and mobile security.
- Attack – defense: Problems are distributed across vulnerable services which must be protected on the defended machine and exploited on remote machines. It is the kind of competition that provides mostly a vulnerable infrastructure.
EKOPARTY CTF 2015
- Trivia problems: questions about EKOPARTY.
- Web application security: multiple web application attacks.
- Cryptography: classical and modern encryption.
- Reversing: problems with the use of different technologies and architectures.
- Exploiting: vulnerable binaries with known protections.
- Miscellaneous: forensic and programming tasks.
To review the challenges, go to the EKOPARTY 2015 github repository.