

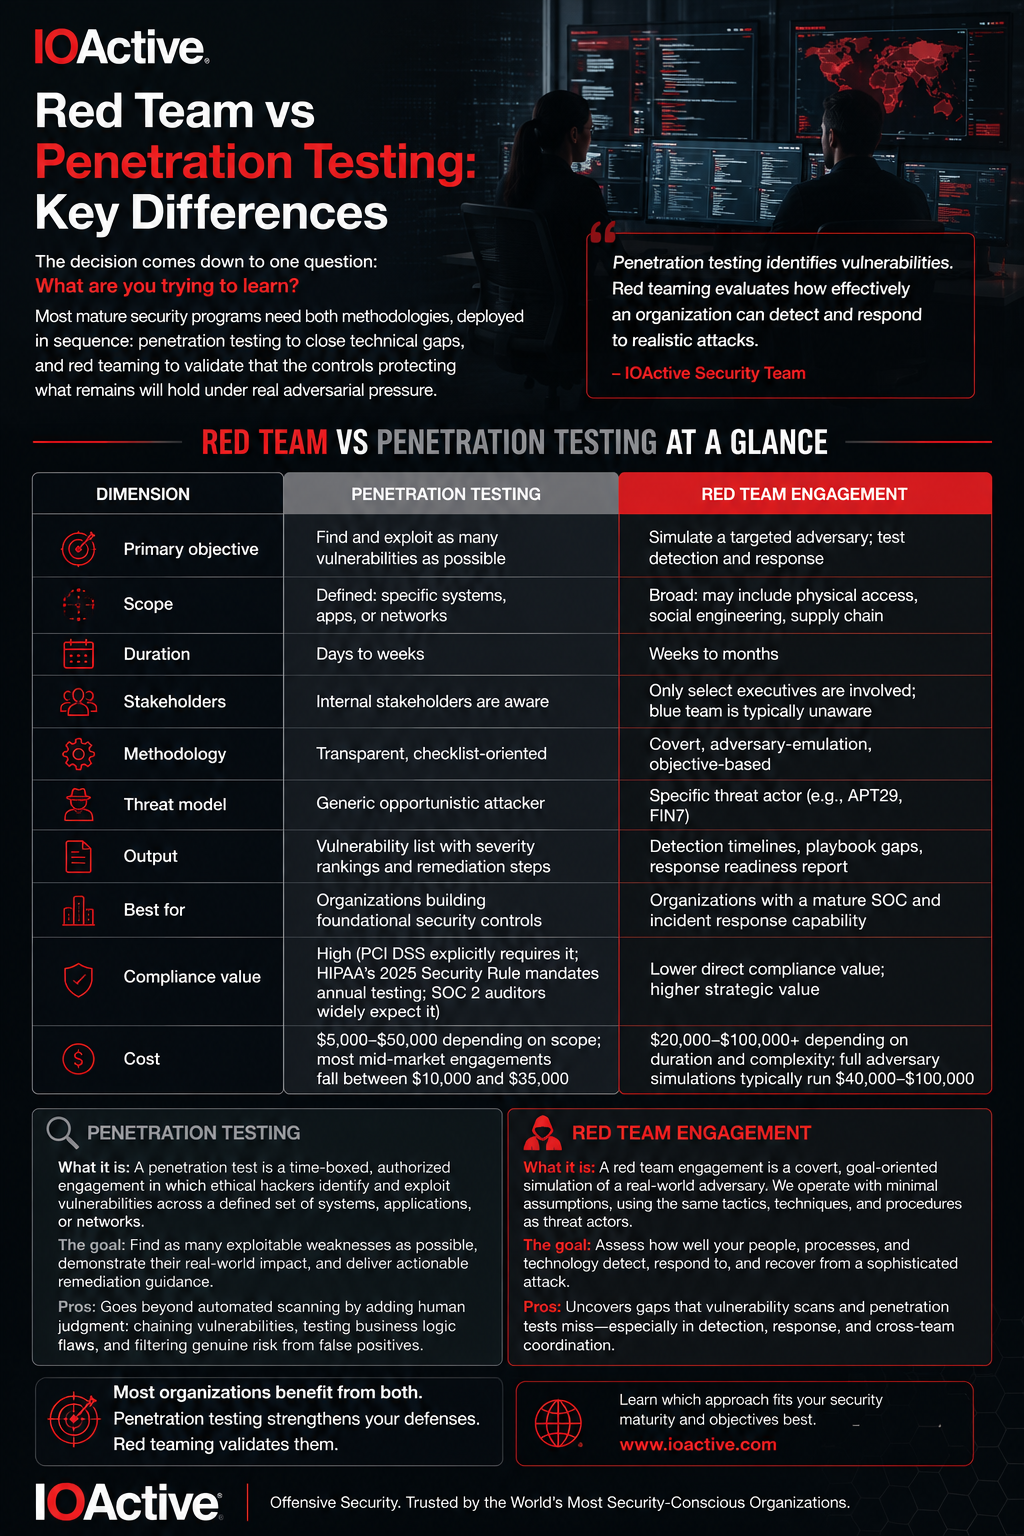
“Penetration testing identifies vulnerabilities. Red teaming evaluates how effectively an organization can detect and respond to realistic attacks.” IOActive Security Team
The decision between red team vs penetration testing comes down to one question: What are you trying to learn? Most mature security programs need both methodologies, deployed in sequence: penetration testing to close technical gaps, and red teaming to validate that the controls protecting what remains will hold under real adversarial pressure.
This article breaks down the differences between red team vs penetration testing so your organization can choose the right approach.
Red Team vs Penetration Testing at a Glance
Penetration Testing
What it is: A penetration test is a time-boxed, authorized engagement in which ethical hackers identify and exploit vulnerabilities across a defined set of systems, applications, or networks.
The goal: Find as many exploitable weaknesses as possible, demonstrate their real-world impact, and deliver actionable remediation guidance.
Pros: Penetration testing goes beyond automated vulnerability scanning by adding human judgment: chaining vulnerabilities, testing business logic flaws, and filtering genuine risk from noise. Findings are immediately actionable.
Cons: Internal teams are typically aware the test is underway, which limits the value for measuring detection and response.
Choose a pentest when:
- A compliance mandate requires it (PCI DSS, HIPAA, SOC 2 Type II)
- You have deployed new infrastructure, applications, or cloud environments
- You are validating remediation from a prior assessment
- You are establishing your organization’s first formal testing program
Red Team Testing
What it is: A red team engagement is a full-scope adversarial simulation in which expert ethical hackers pursue specific objectives, such as accessing sensitive data or compromising executive accounts. Red team engagements use the same tactics, techniques, and procedures (TTPs) as real-world threat actors.
The goal: Determine whether your organization’s people, processes, and technology can detect, contain, and respond to a sophisticated attacker pursuing a specific objective, before a real adversary tests those same capabilities.
Pros: The engagement runs covertly, often without notifying the organization’s own security staff. This generates realistic data on detection timelines and incident response effectiveness.
Cons: Red team engagements are not optimized for cataloging technical vulnerabilities at scale. If foundational controls are weak, the red team will often achieve its objectives before meaningful detection data can be collected. In those cases, a penetration test would have surfaced the same findings faster and at lower cost.
Choose a red team engagement when:
- Your SOC monitors alerts but has never been validated against a sophisticated intrusion
- You need to test people and processes, not just technical controls
- You want to measure detection and response against a specific, realistic threat scenario
- Your security program has matured beyond foundational vulnerability management
Choose Based on Security Maturity
The most reliable decision factor is security maturity, which determines which question you are ready to answer. Organizations that have not yet closed known vulnerabilities will get more value from a pentest than from a red team engagement.
Organizations early in their security journey should run penetration tests first. If a red team can compromise your environment in hours without triggering a single alert, those findings could have been reached more efficiently with a pentest. Closing known vulnerabilities first allows a red team engagement to surface detection and response gaps that actually matter.
Security Maturity and Testing
Most organizations overestimate their maturity. If you have not run a penetration test within the past 12 months, or if your SOC has never responded to a simulated intrusion, a red team engagement will tell you less than a rigorous pentest will.
How the Two Methodologies Work Together
Penetration testing and red teaming are not competitors: they serve different stages of a security program. The typical progression is to run a pentest, remediate vulnerabilities, and build detection and response capabilities. From there, a red team engagement tests whether the SOC would detect a sophisticated attacker exploiting what remains.
Red team findings routinely drive improvements to SIEM detection rules, incident response playbooks, and security awareness training. It’s also recommended to use purple team exercises, which pair red team attackers with the organization’s blue team in a collaborative format to accelerate control tuning in real time.
Work With IOActive for Red Team Engagements and Penetration Testing
With over 25 years of offensive security research and engagements across some of the world’s most complex environments, IOActive has the experience to determine the right methodology for your risk profile and execute it with precision. IOActive’s penetration testing practice goes beyond off-the-shelf tooling, applying an attacker’s perspective and human judgment to chain vulnerabilities, expose business logic flaws, and deliver findings with clear remediation priority. Our red and purple team engagements run multi-vector, goal-based adversary simulations across technical, physical, and human attack surfaces, testing prevention, detection, response, and recovery under realistic conditions.